What is a bulletproof host?
A bulletproof host ignores legitimate takedown requests from stakeholders and refuses to cooperate with legitimate organisations — whether private or public — in taking action against malicious activity, ranging from online piracy and trademark infringement to malware, phishing, and more serious threats to internet users and national security.
A bulletproof host also explicitly advertises or markets itself as “bulletproof”, “DMCA-ignored”, or “anonymous” on its own website, forums, or social media platforms.
A bulletproof host also may not perform Know Your Customer (KYC) checks or keep logs for its customers, and does not cooperate with law enforcement in criminal investigations. It typically accepts cryptocurrency for payments, in addition to or instead of traditional payment methods.
How do they operate?
A bulletproof hosting network can operate under a low-to-high operational security (OpSec) model. Some register in offshore jurisdictions, maintain a minimal online presence to protect themselves, and advertise only on darknet forums; others are more open and leave more traces on the open web that could lead back to their real-world identity.
They may target customers in high-risk environments such as darknet forums, operating under fake monikers and inactive websites, or they may be more open and advertise on social media, on their own websites, and through search-engine ads.
Ultimately, a bulletproof host has little regard for who its customers are or what they actually host. A customer may claim to be running a legitimate online clothing shop while, in reality, also running a phishing operation. The verification (KYC) processes a bulletproof host applies to its customers are typically poor or non-existent.
Xploratio Platform
The Xploratio platform includes over 600 profiles of hosting providers. Each has been investigated, with data verified, validated, and enriched through OSINT and test purchases.
57.3% of them are included on the Xploratio ASN blocklist due to their involvement in malicious hosting activities and risky connections.
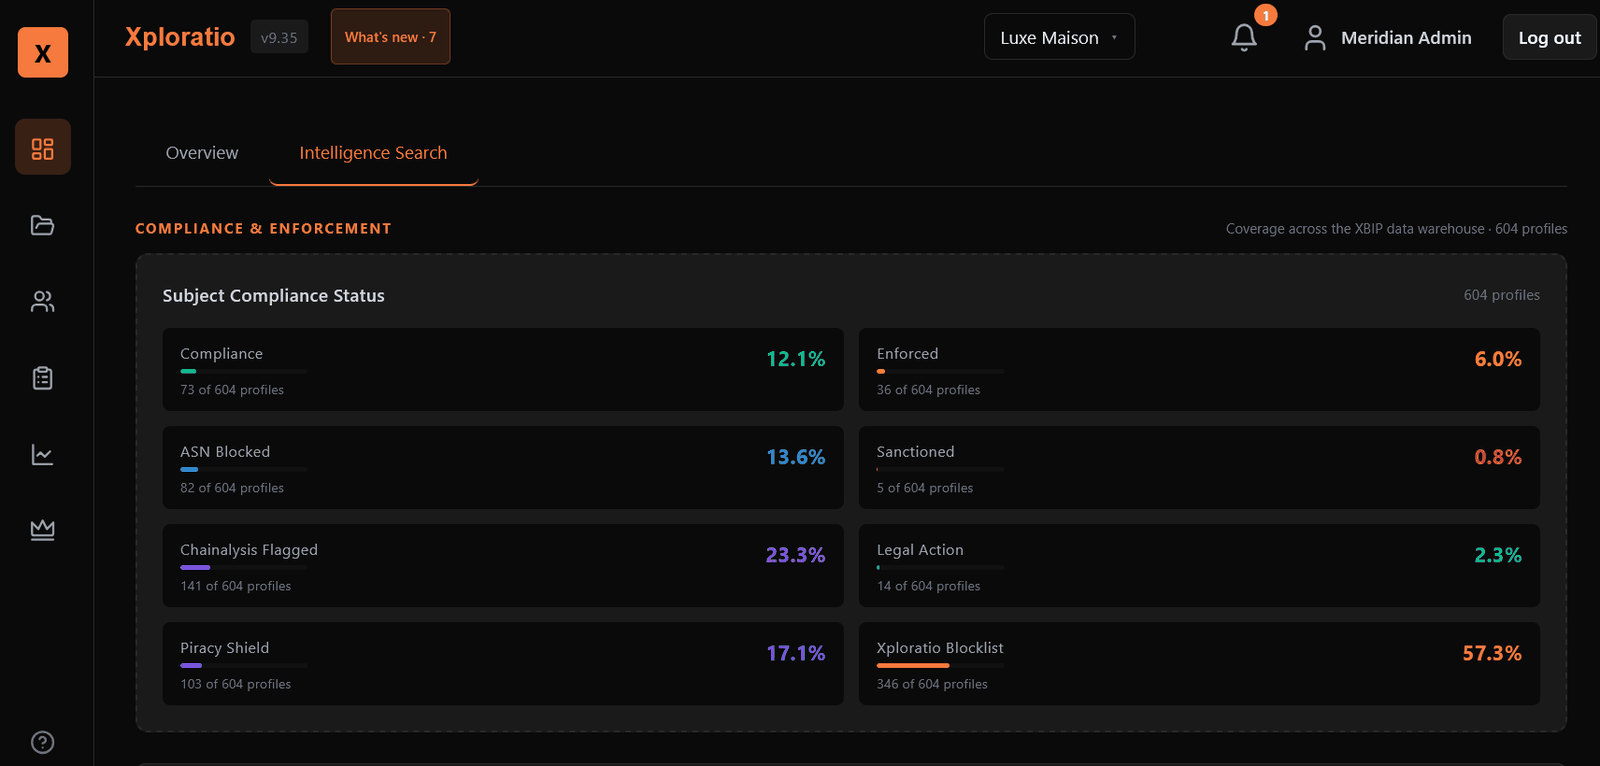
The Xploratio platform consists of four main components:
- Intelligence Search — quickly search for a bulletproof host to retrieve its profile for investigation, disruption, or escalation purposes
- Agile Case Management — add an entity to a case for investigation, tracking, and corroboration with your own data through the Connections Module, as well as disruption actions
- Connections Module — identify whether an entity is connected to other entities or to your own data points, helping to pinpoint choke points for legal process (e.g., subpoenas), disruption, escalation, or enforcement
- Tasks — order specific actions (e.g., offshore investigation, online undercover operations, test purchases, ASN Intelligence, etc.) or collaborate with Xploratio’s team on investigation, disruption, escalation, or enforcement
IP Solus Inc Case
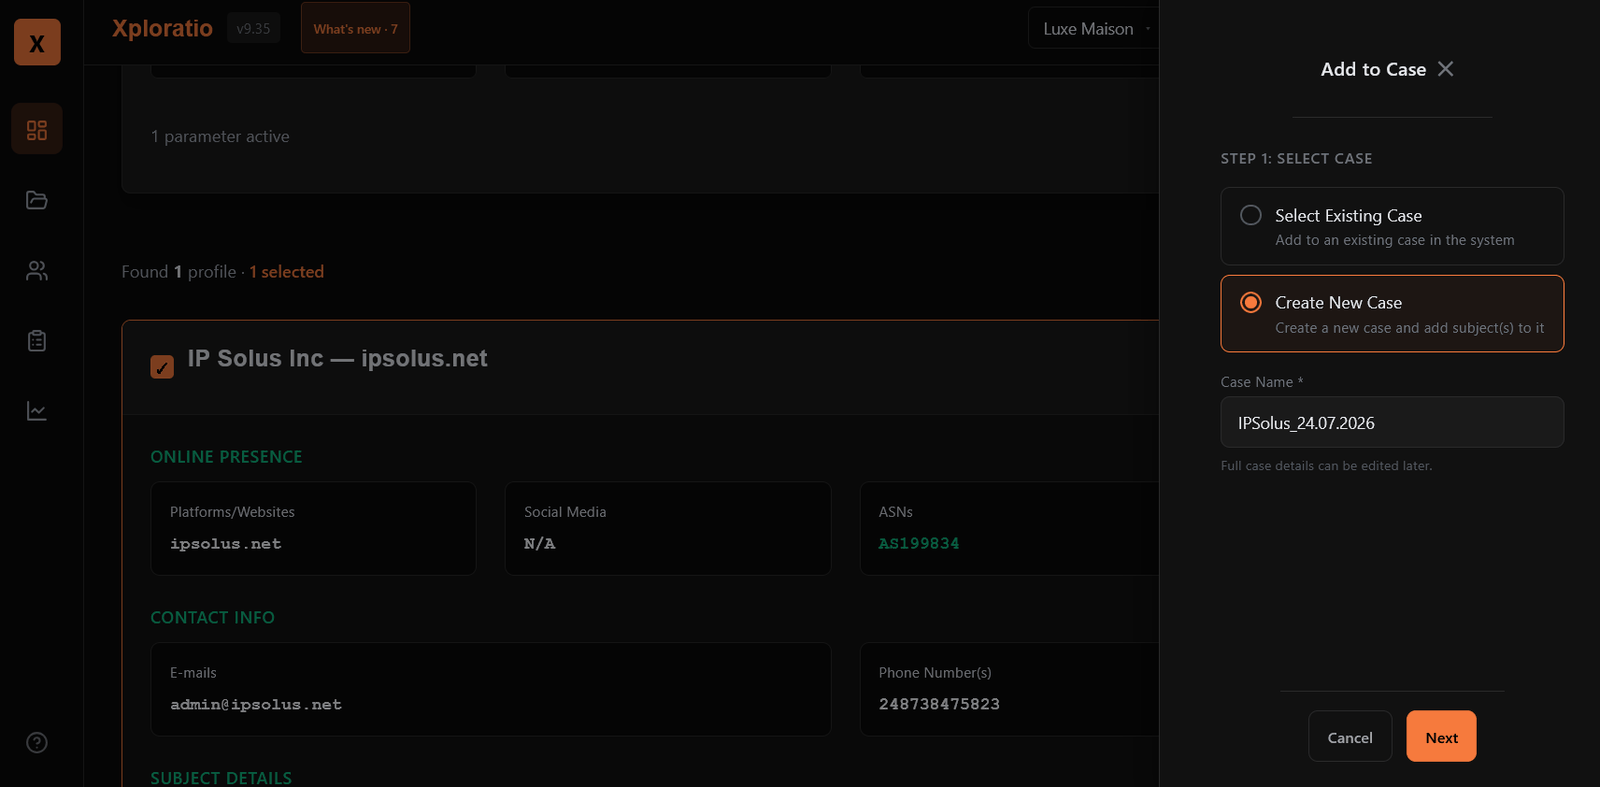
IP Solus Inc (Company No. 234666) was incorporated in Seychelles on 13 July 2022 through registered agent c/o Fidelity Corporate Services. The company operates through the website ipsolus[.]net, which was registered through NameCheap on 1 September 2022.
No information about shareholders or directors is available on file.
RIPE Database Search
What is an ASN?
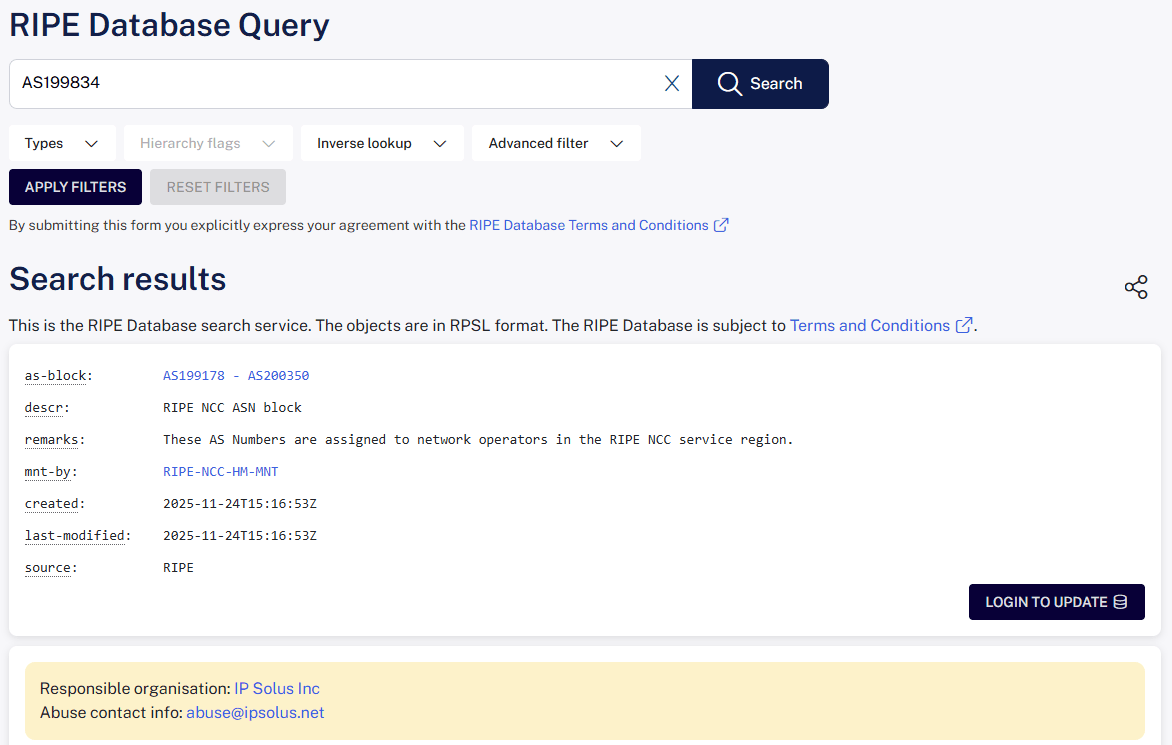
An Autonomous System Number (ASN) is a unique identifier assigned by a Regional Internet Registry (such as RIPE NCC) to a network that manages its own routing on the internet, allowing its IP address space to be advertised and reached globally.
AS199834 was identified to be assigned to IP Solus Inc on 15 February 2023 via RIPE NCC.
The admin contact address, admin@ipsolus[.]net, was not found registered on any online platforms during OSINT verification.
Server Localisation
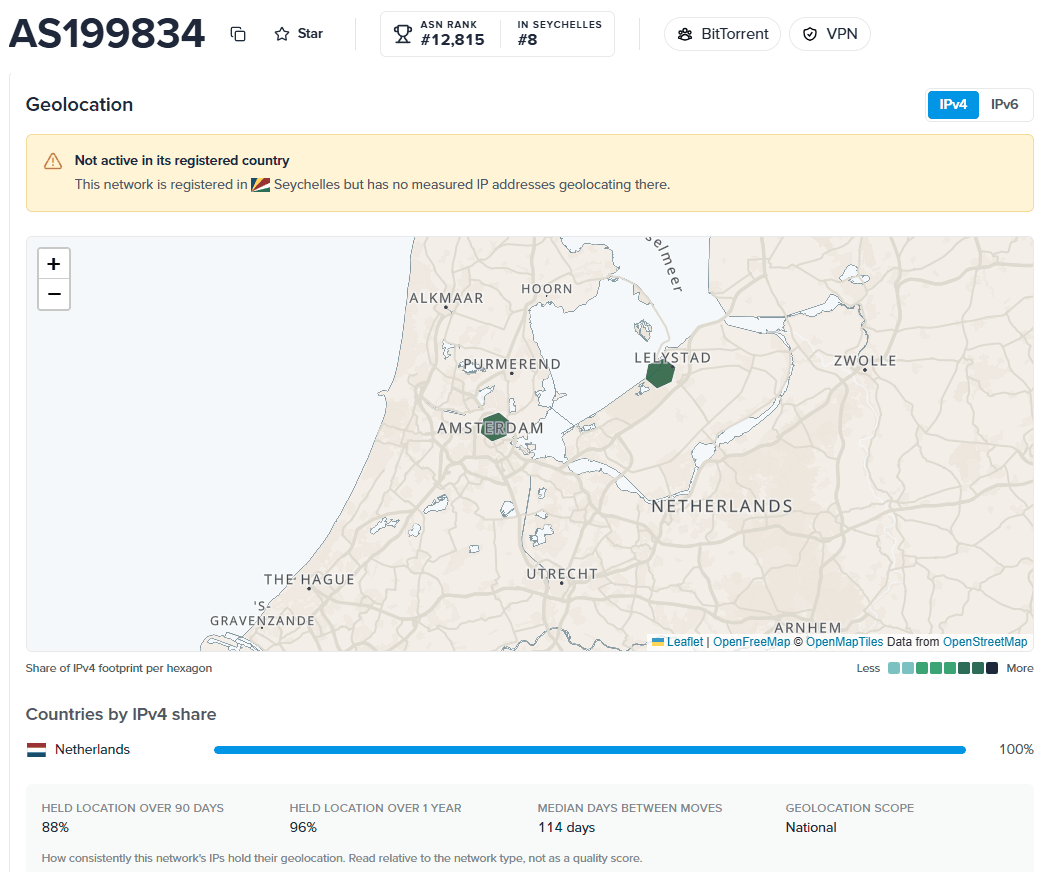
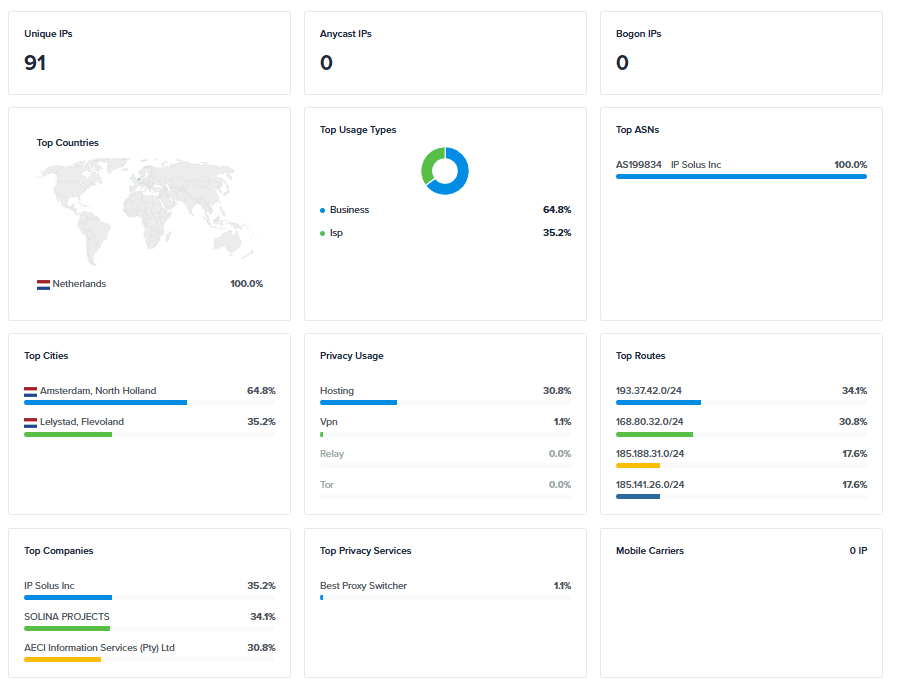
According to ipinfo.io, AS199834 hosts its IPv4 servers in Amsterdam and Lelystad, Netherlands.
IP netblocks and Privacy Services
What is an IP netblock or prefix?
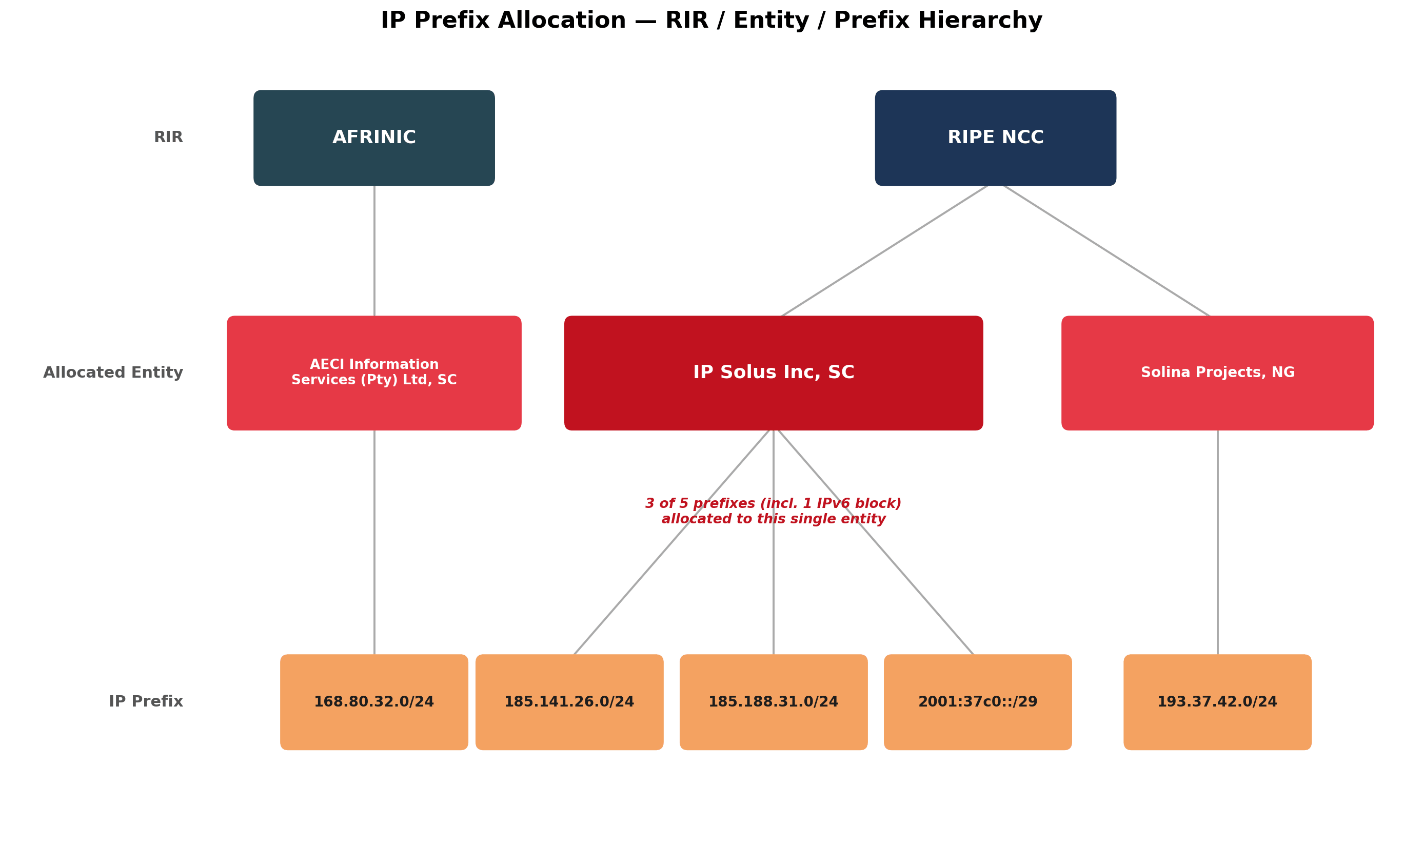
An IP netblock, or prefix, is a contiguous range of IP addresses (e.g., 185.141.26.0/24) allocated to an organisation by a Regional Internet Registry and used to route traffic to the servers within that range.
Four (4) IPv4 prefixes and one (1) IPv6 prefix were identified as allocated to AS199834. A summary chart is provided below.
Verification of the IPv4 addresses through ipinfo.io against known VPN and residential-proxy usage uncovered only one (1) IP address associated with Best Proxy Switcher.
Upstream & Downstream networks
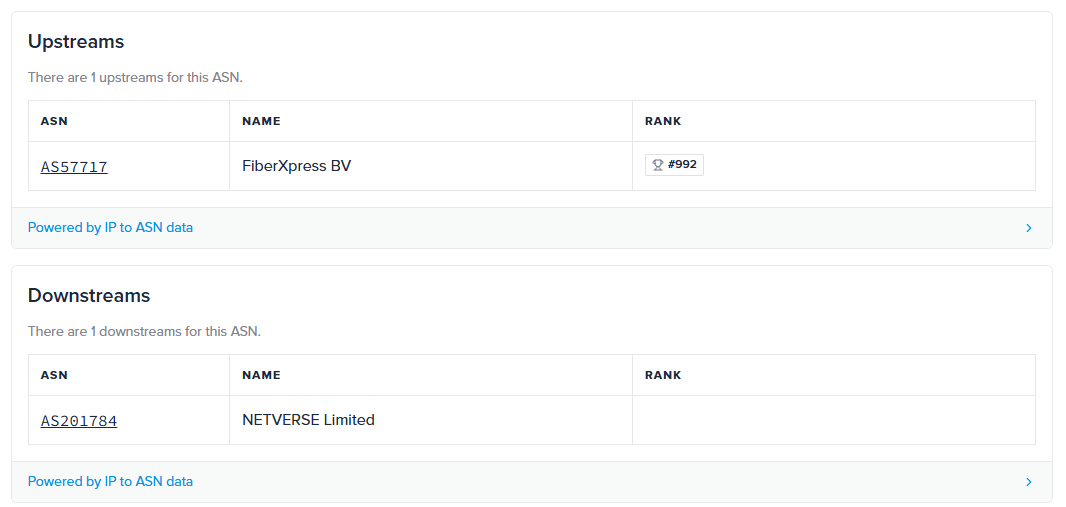
An upstream provider is a network that supplies internet connectivity (IP transit) to another network, carrying its traffic to the rest of the internet.
A downstream hosting network is a smaller network that purchases connectivity from an upstream provider and, in turn, hosts content or allocates IP space to its own customers.
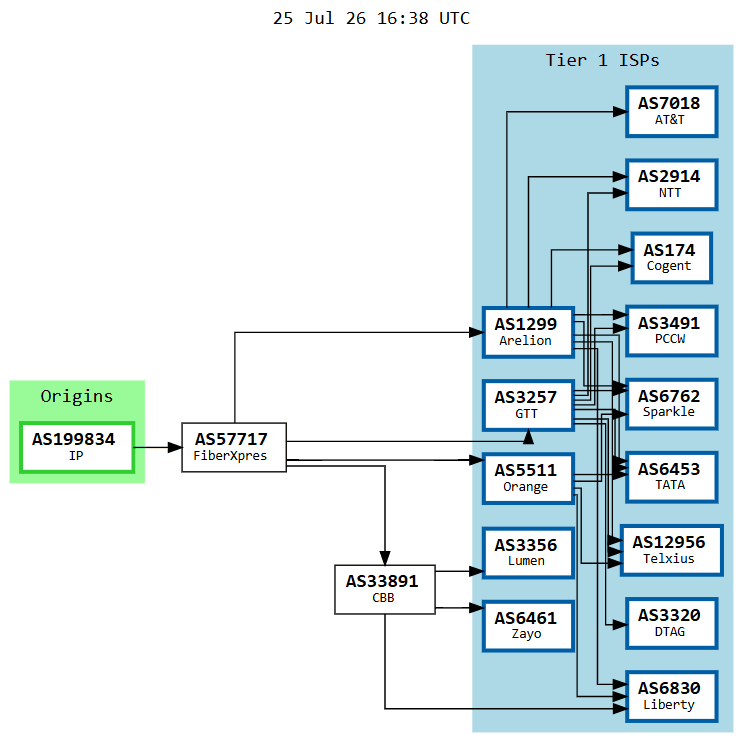
AS199834 was identified as using FiberXpress BV (AS57717; part of the IP Volume Inc network) as its sole upstream provider. Its sole downstream hosting network is NETVERSE Limited (AS201784).
NETVERSE Limited is a company registered in Saint Kitts and Nevis, associated with the website ddosward[.]com, a domain registered through NameCheap on 12 November 2025. Per ipinfo.io, AS201784 hosts two (2) IPv4 prefixes located in Amsterdam, Netherlands. Further investigation into this network was not conducted for this article.
Xploratio ASN Intelligence
ASN Intelligence is Xploratio’s in-house solution that collects data across an entire ASN or specific IP ranges, automatically maps activity using various threat intelligence feeds (open-source and commercial), and applies verification and validation processes aligned with standards used by the law enforcement community.
The Xploratio platform allows stakeholders to choose between various tasks, including ASN Intelligence’s “Collect ASN data” function.
A scan of AS199834 uncovered the hosted activity shown below. The chart includes only hosting activity on IPv4 space; the IPv6 prefix (2001:37c0::/29) was scanned against DNS and TLS certificate records, but no activity had been identified at the time of scanning.
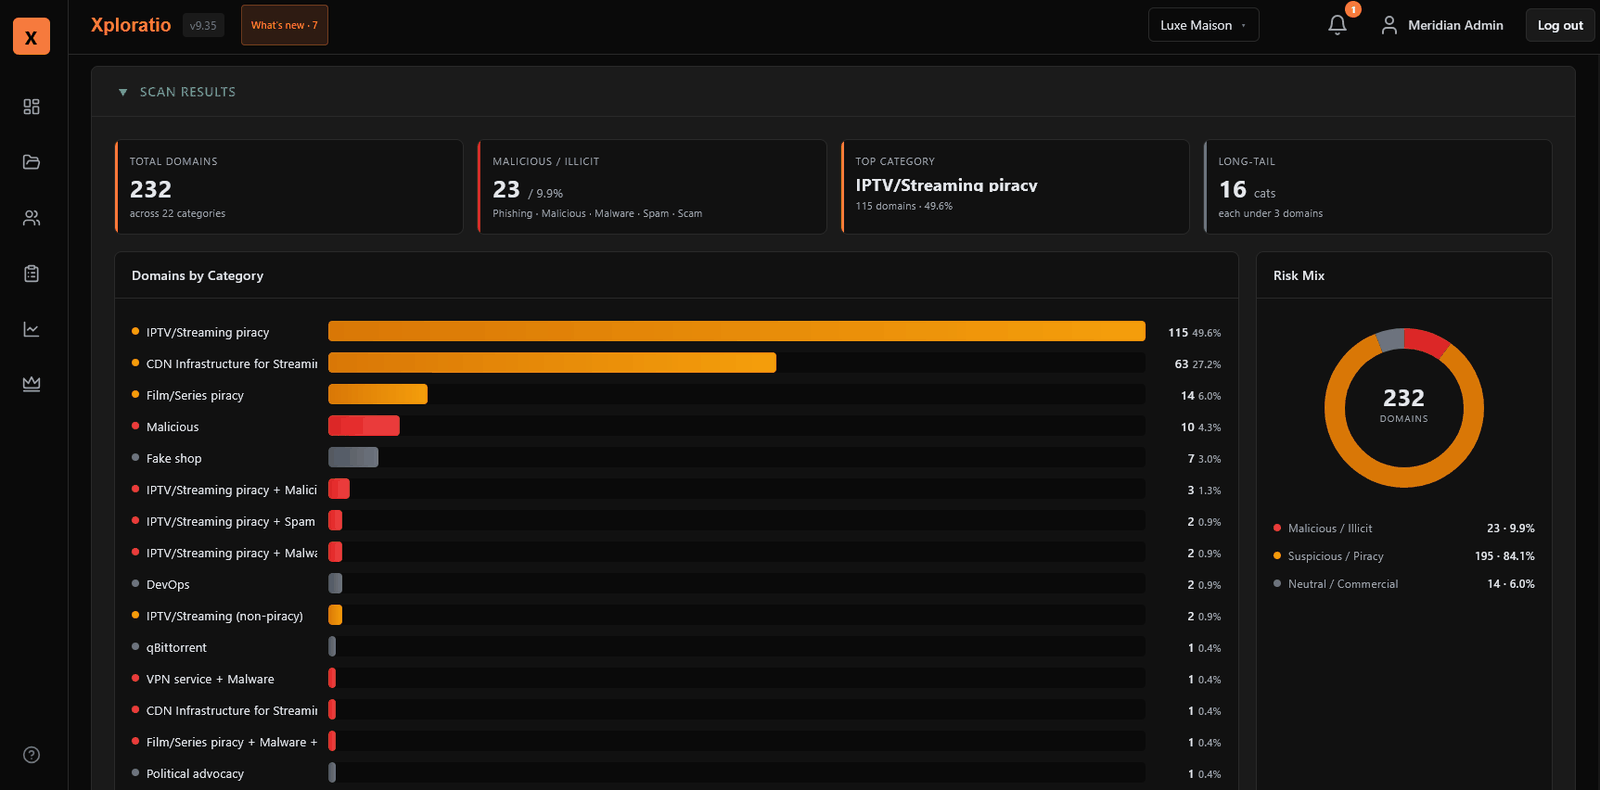
50.0% of hosted content on AS199834 was identified as related to IPTV/streaming piracy, followed by content delivery network (CDN) infrastructure for streaming piracy (27.0%). 6.0% of hosted activity relates to film and series piracy, and 3.0% is represented by fake online shops.
A further 9.9% of hosted activity is classified as malicious — including phishing, malware, spam, or scam. The remaining ~4% is spread across other categories.
Live Stats
At the time of scanning, 115 domains, subdomains, or IP addresses were identified as active or accessible.
A summary chart of the domain category vs operational status is provided below.
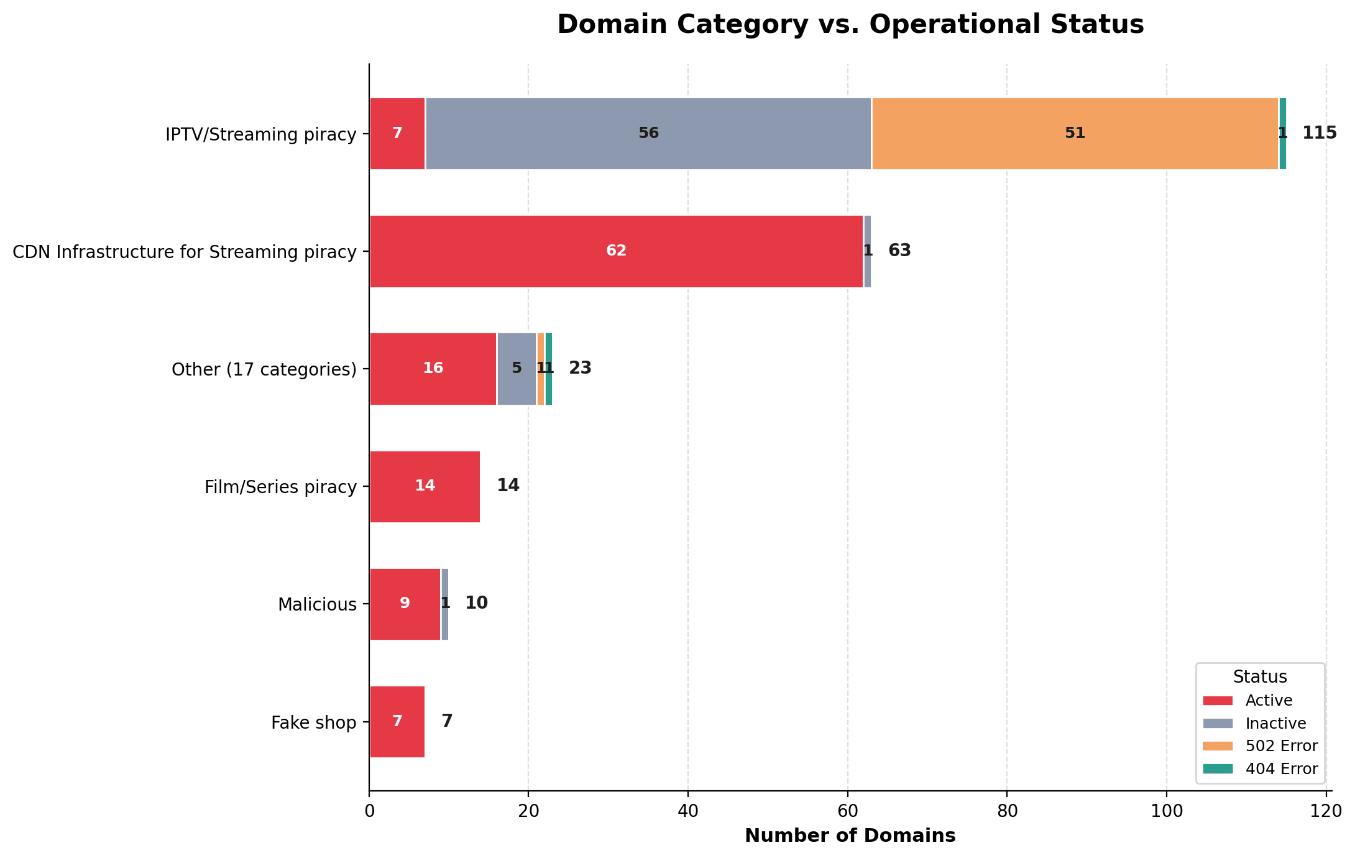
Note: within this classification, a domain or server is labelled “Malicious” when independent security tools such as VirusTotal flag it as harmful and Xploratio’s investigators confirm that assessment through manual review, but there is not yet definitive evidence to attribute it to a specific known threat category, such as phishing, malware, or a named threat actor.
Mapping the Networks
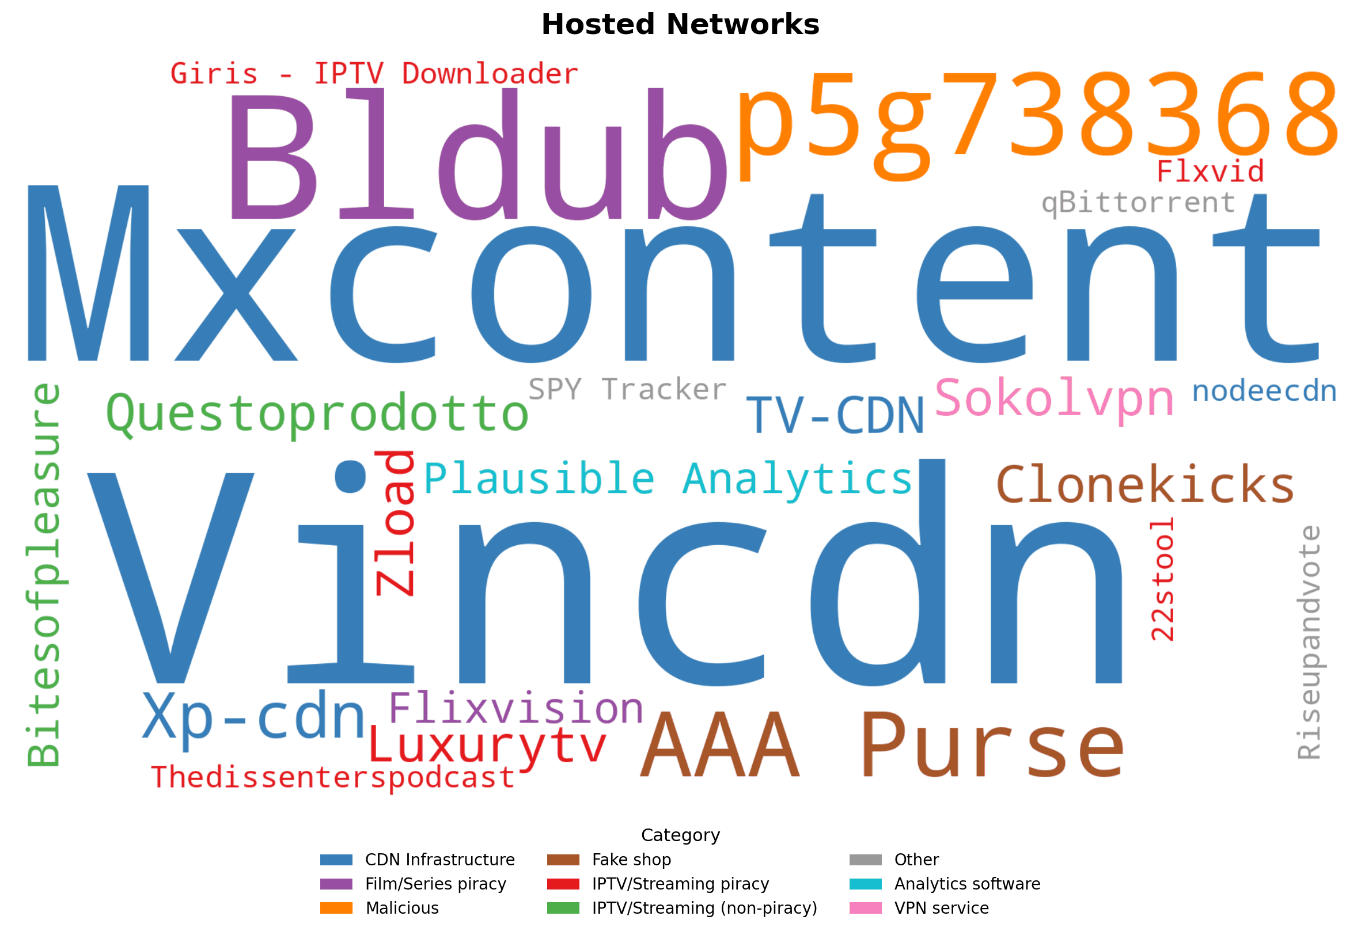
The chart below shows the domains, subdomains, and IP addresses attributed to their relevant network names.
Verification & Validation Processes — Examples
Beyond automated matching against threat-feed categories from trusted threat intelligence providers, Xploratio maintains a human-in-the-loop process to verify and validate results manually, following law enforcement standards. The networks below are examples of how Xploratio verifies, validates, and further expands an investigation into a specific network when needed.
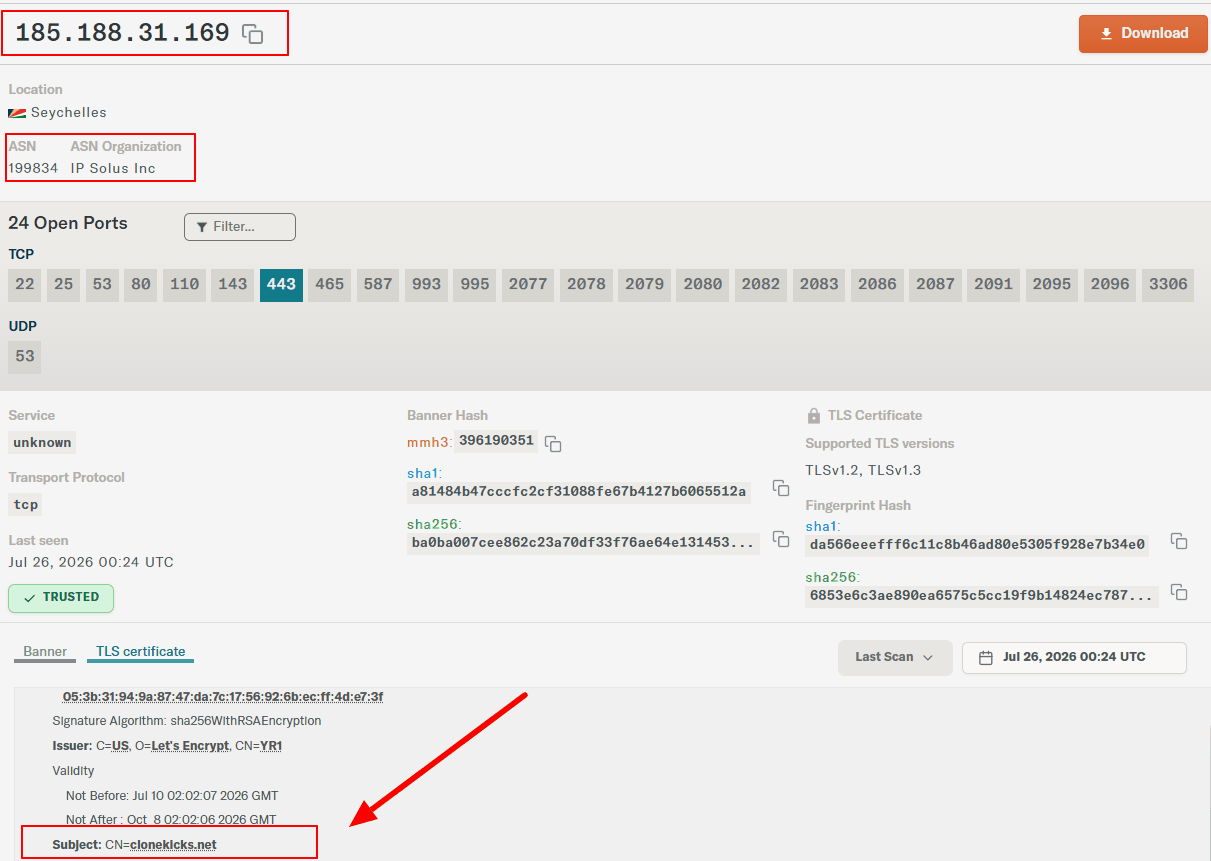
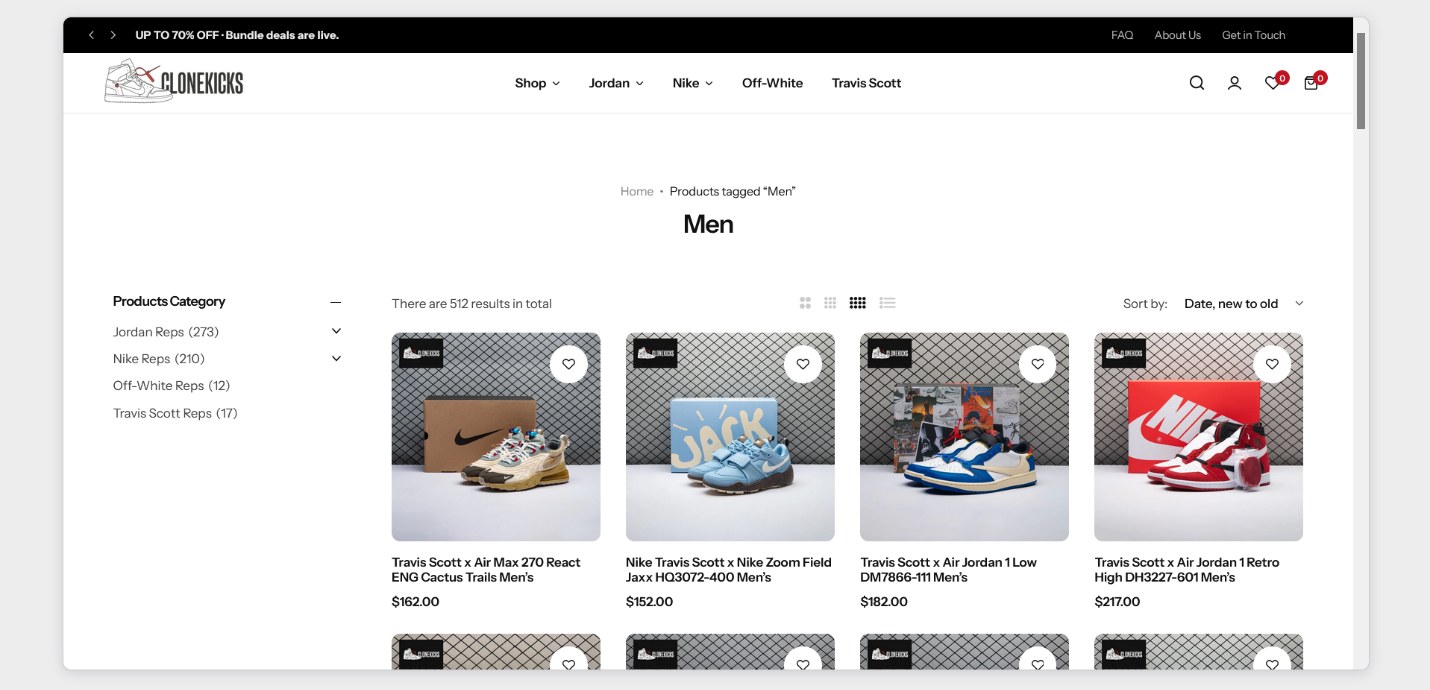
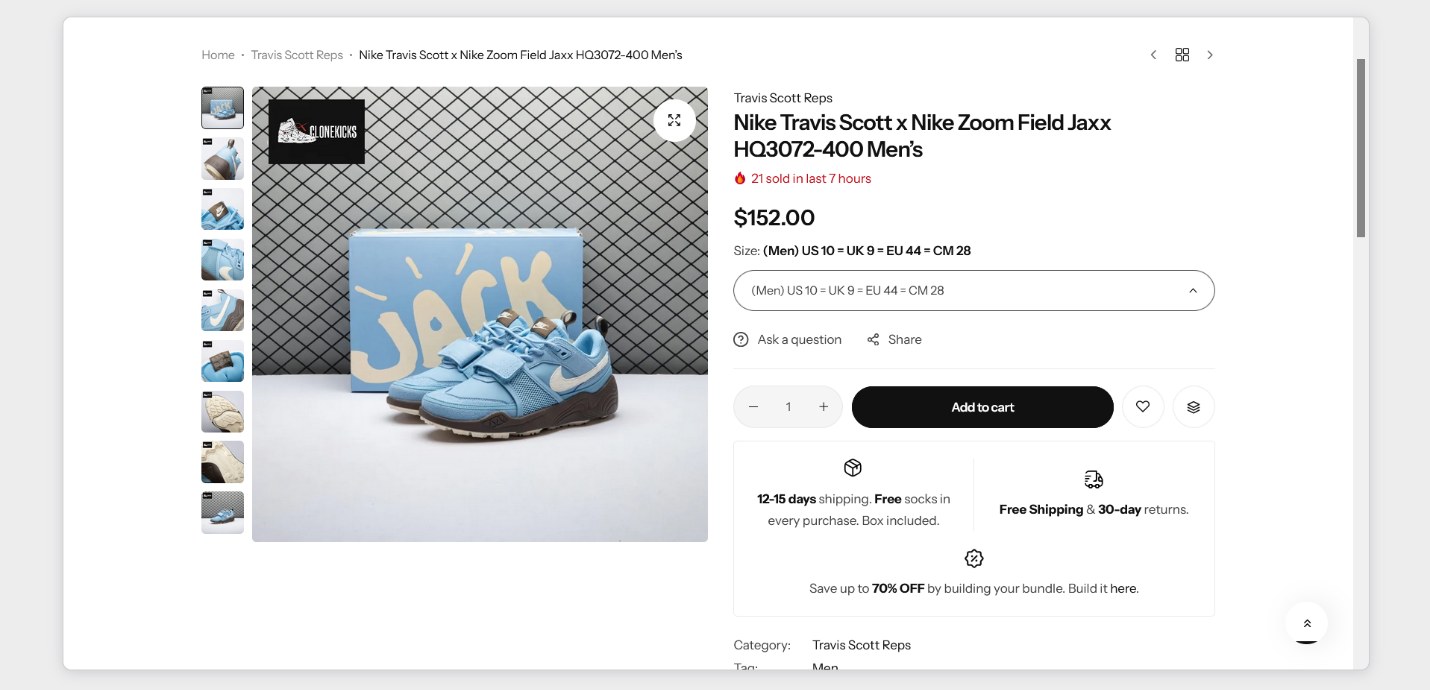
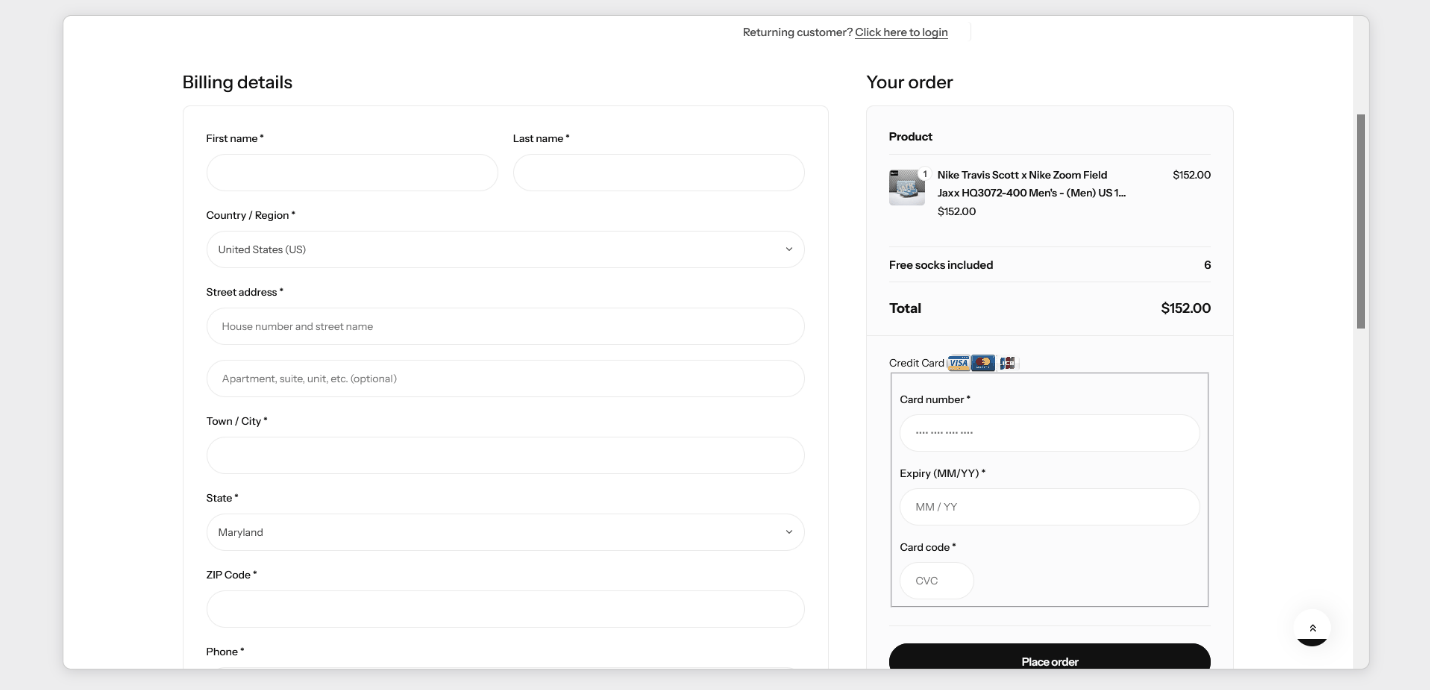
Clonekicks — Fake Shop
Clonekicks was identified to be a fake shop offering Jordan, Nike, Off-White, Travis Scott sneakers. The website, clonekicks[.]net, displays a fake physical address in Bethesda, Maryland and a US phone number +1-(305)-914-6478 (Carrier: ONVOY LLC — FL; Locality: North Miami). The domain clonekicks[.]net was registered on 3 March 2026 through GoDaddy.com. Payments are processed via credit card.
AAA Purses — Fake Shop
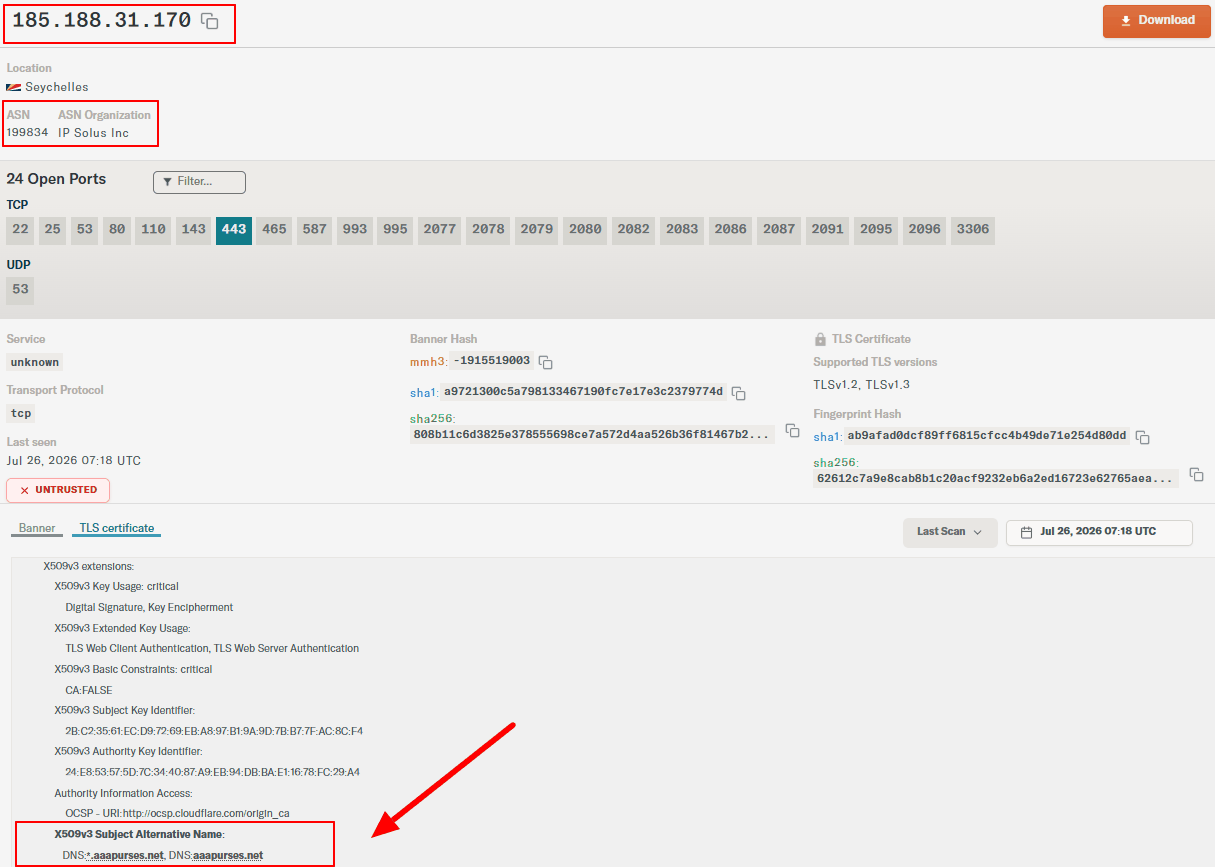
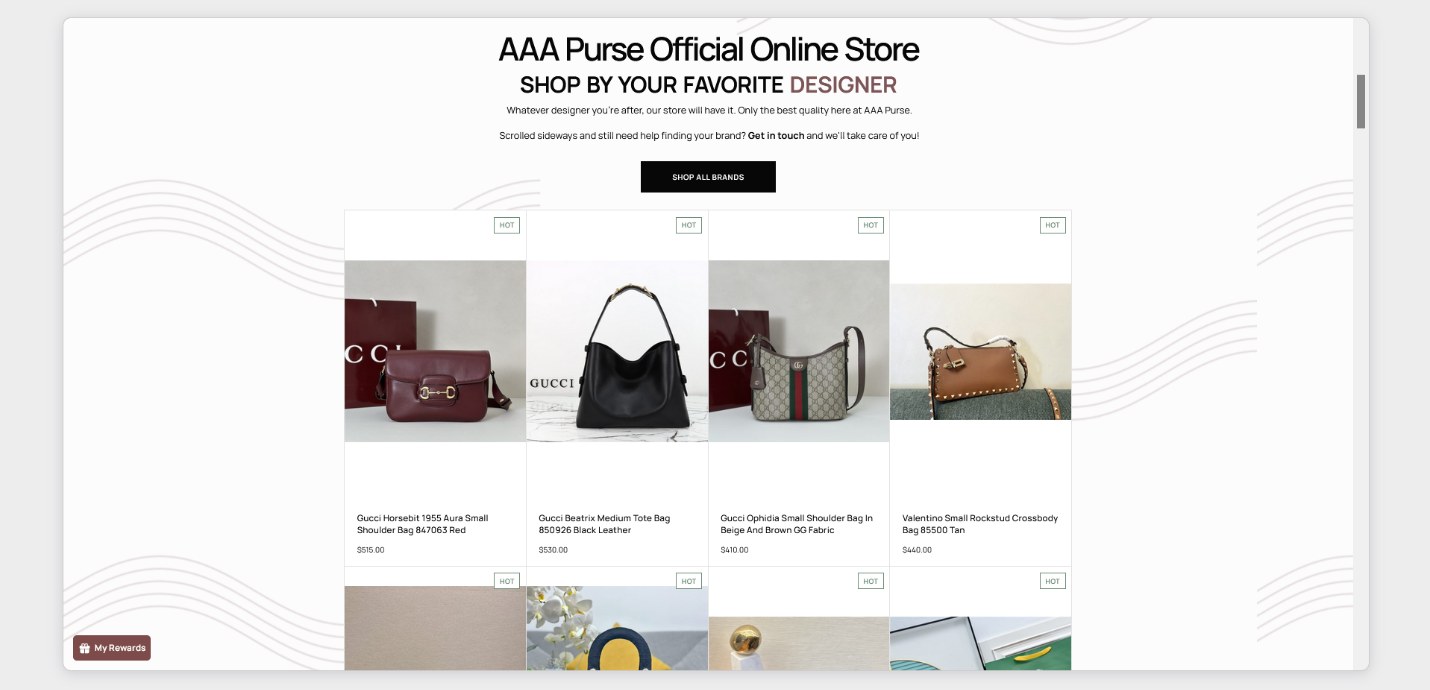
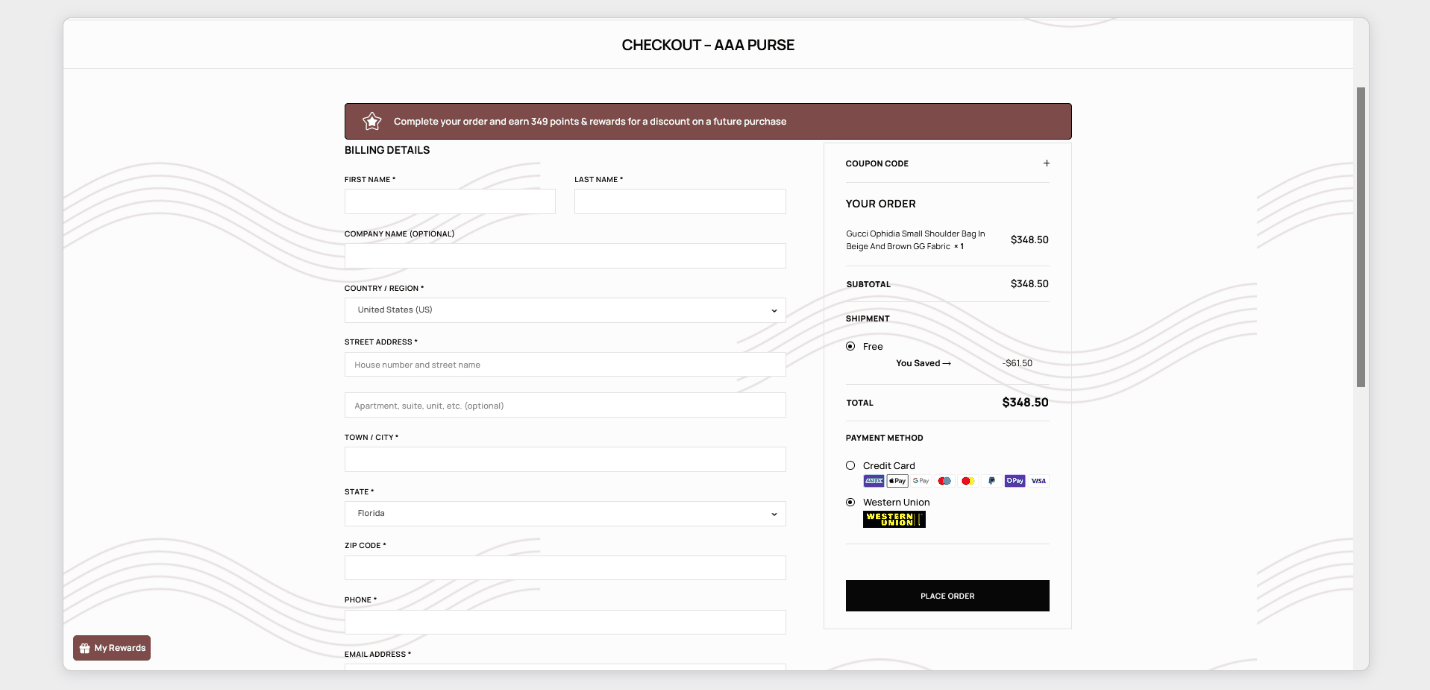
AAA Purses (aaapurses[.]net, aaapurse[.]st, aaabags[.]nu) is a cluster of fake online shops offering luxury handbags (Gucci, Valentino, Dior, Prada, etc.), shoes (Gucci, Prada), jewellery (Valentino, Loewe, Fendi), and watches (Rolex, Hublot, Richard Mille, etc.). aaapurses[.]net displays an address in Miami, Florida, and a US phone number, 1-(305)-280-4724 (carrier: ONVOY LLC — FL; locality: Key West). aaapurses[.]net was registered on 14 September 2025 through Realtime Register B.V.; aaapurse[.]st was registered on 22 December 2025 through NordNIC; and aaabags[.]nu was registered on 30 July 2016 through SpaceDump IT AB. AAA Purses accepts payments via credit/debit card and Western Union.
FlixVision APK — Film/Series Piracy
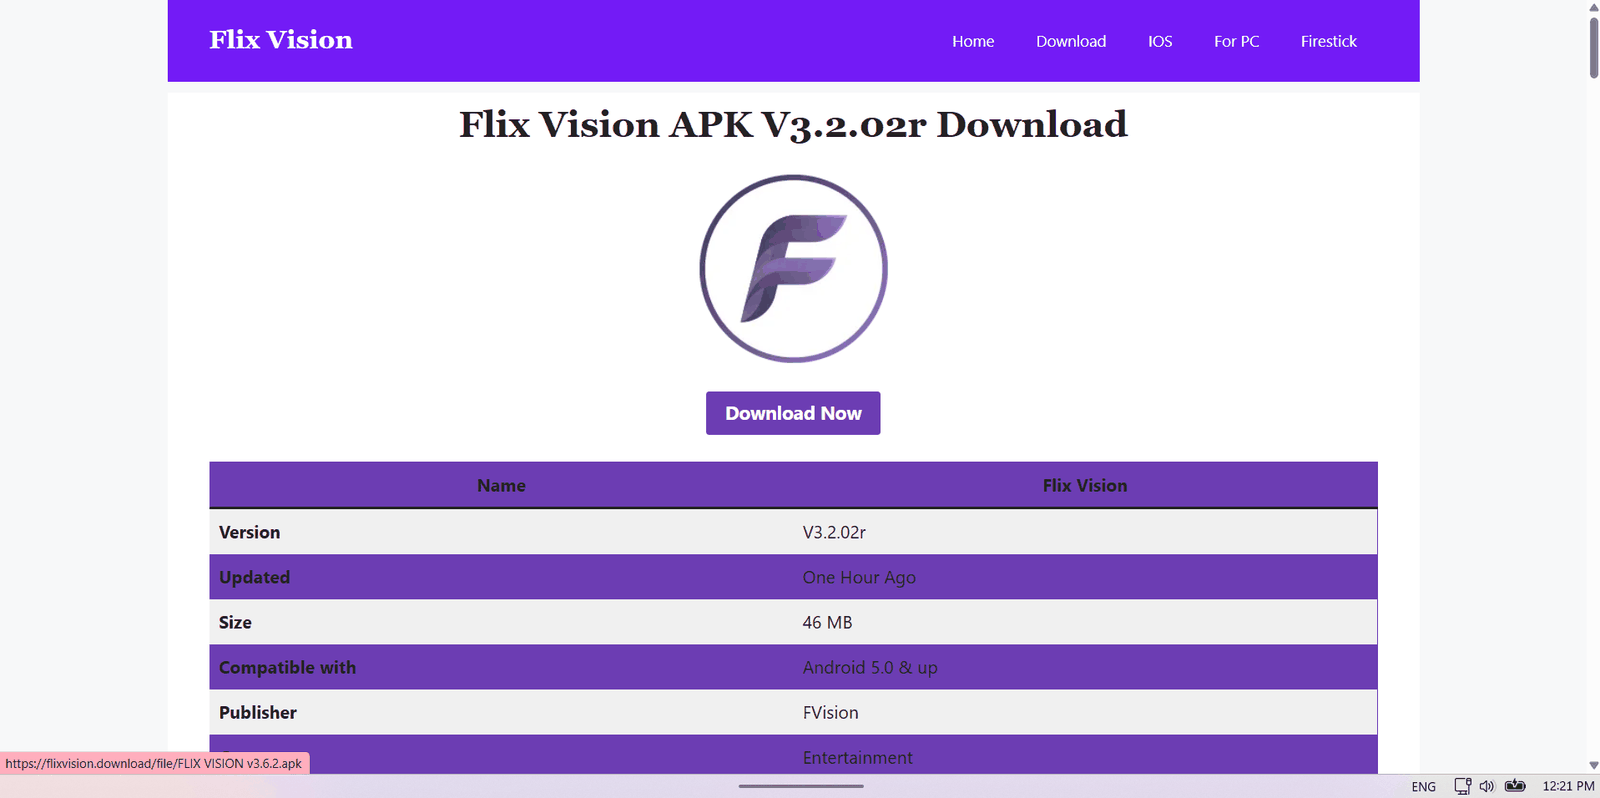
FlixVision APK (flixvision[.]us) is a pirated media-streaming application used to watch movies and TV shows. The domain flixvision[.]us was registered on 9 September 2025 by a Pakistani national.
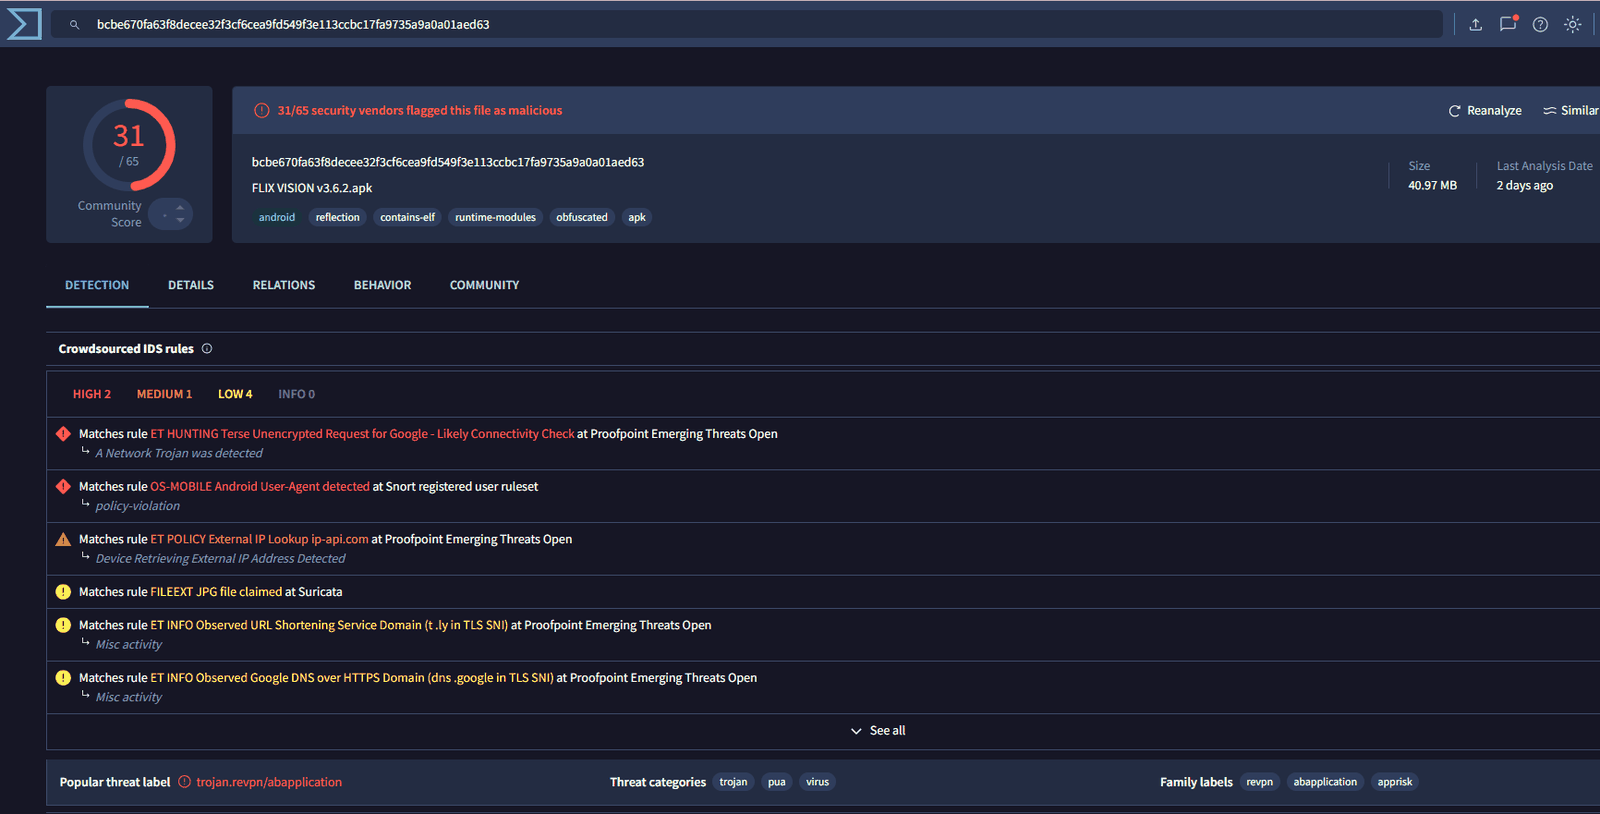
A security analysis via VirusTotal saw the “FLIX VISION v3.6.2.apk” file flagged as malicious by 31 of 65 security vendors, including detection of a network Trojan.
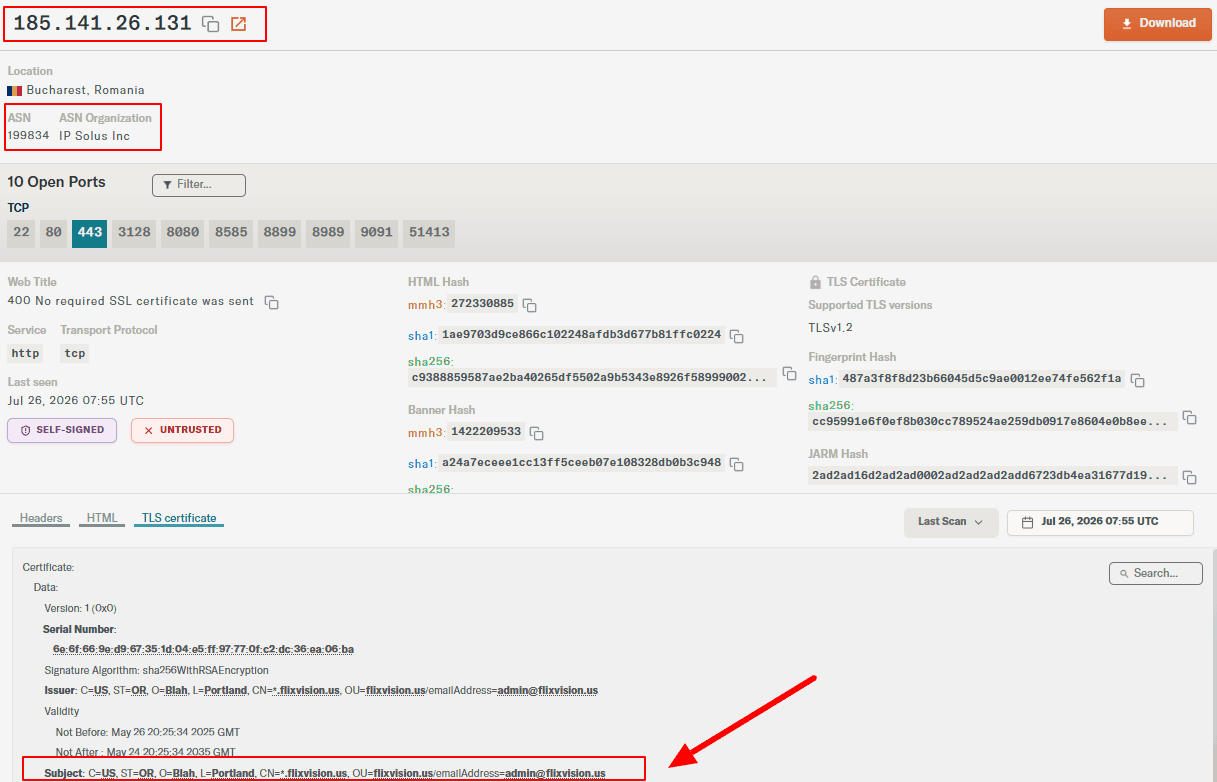
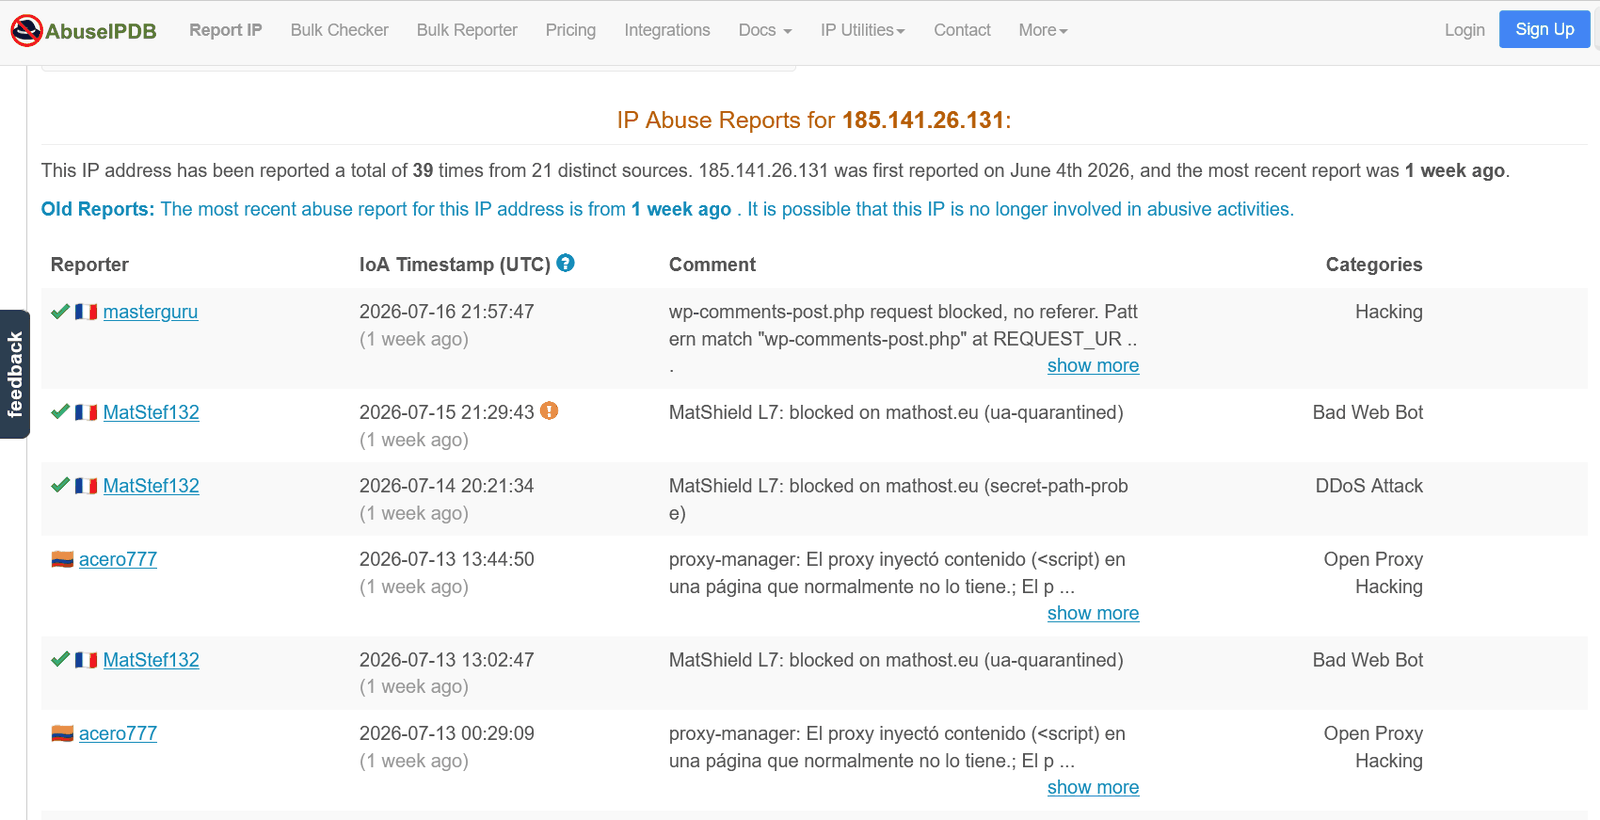
Reports for 185.141.26[.]131 via AbuseIPDB show that the IP was flagged for botnet activity, DDoS attacks, and hacking. Per ipinfo.io, the address is also flagged as associated with Best Proxy Switcher.
Giris - IPTV Downloader — IPTV/Streaming piracy
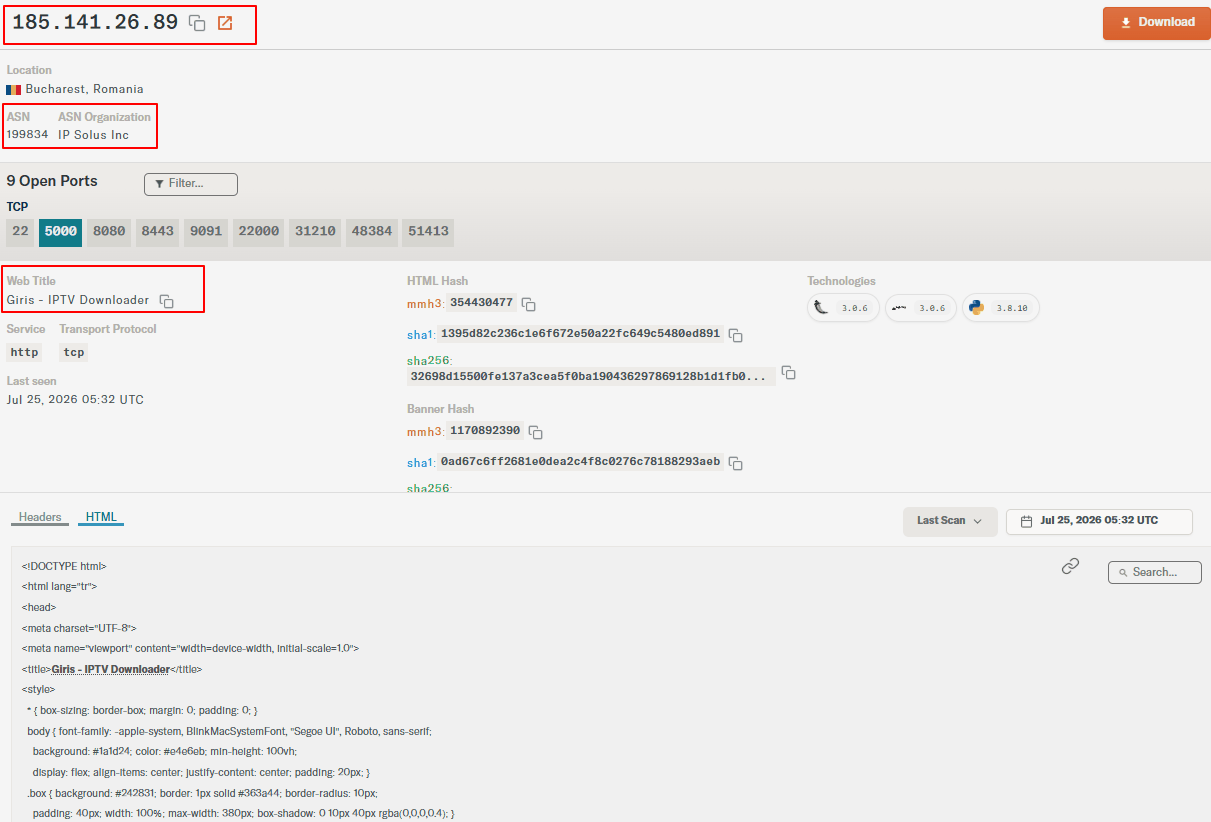
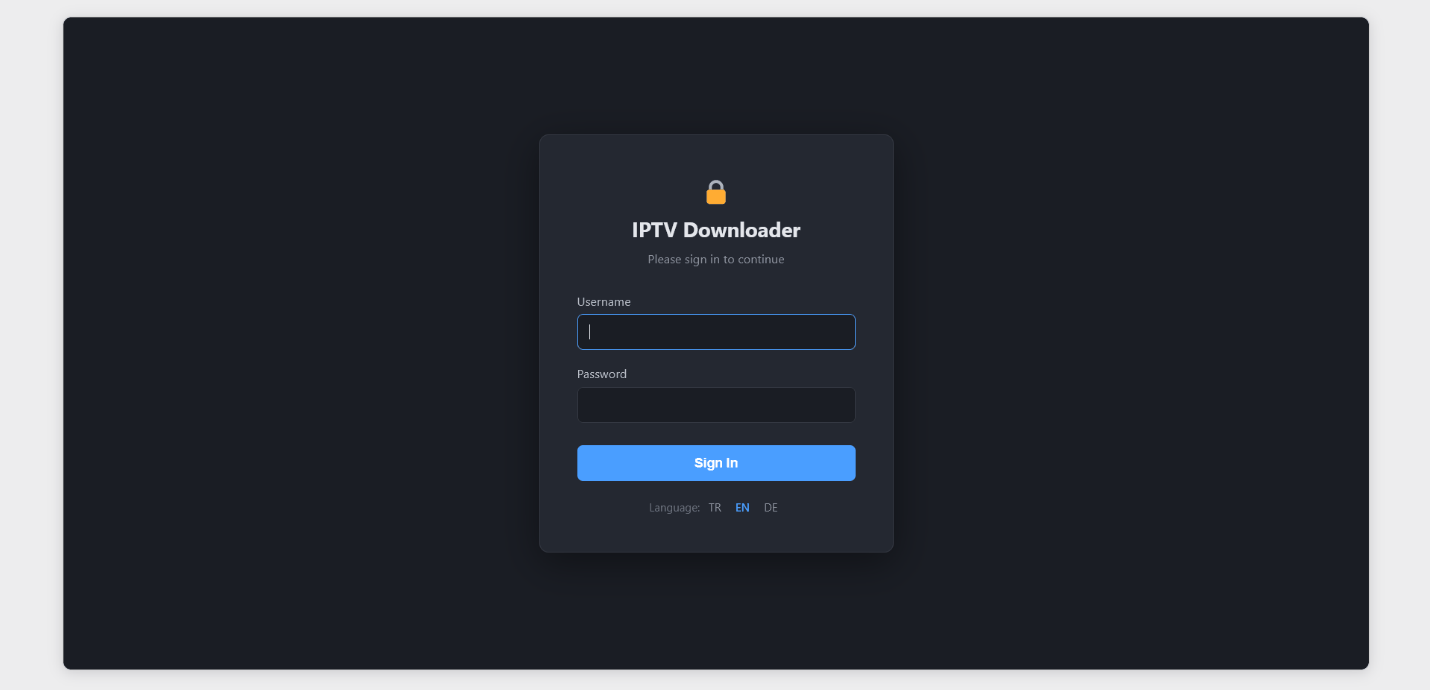
Giris - IPTV Downloader was identified as a Turkish login panel hosted on IP address 185.141.26[.]89, flagged by ipinfo.io for BitTorrent activity in the past 30 days. The panel is accessible via port 5000.
BLDUB — Film/Series Piracy
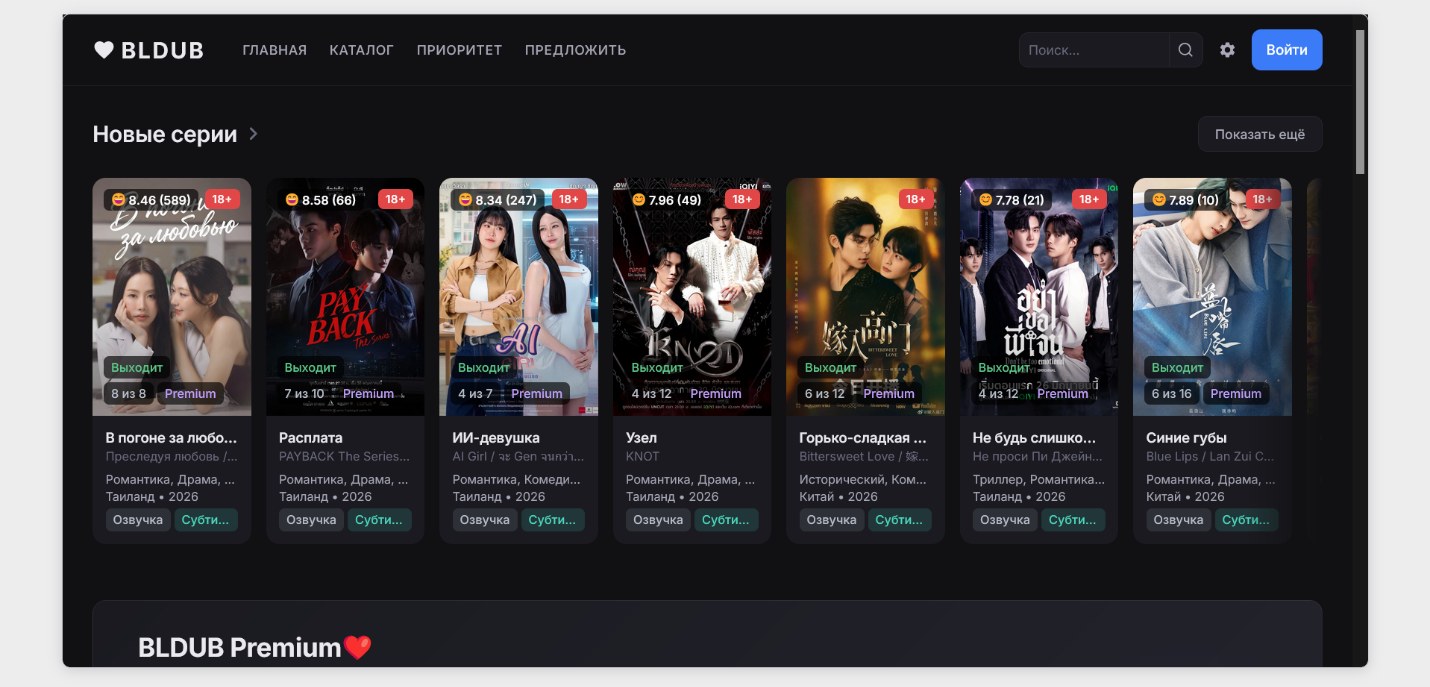
BLDUB (e.g., bldub[.]com) is a cluster of pirated, Russian-language streaming domains providing Russian voice-over dubbing and subtitling of Asian television series, specifically BL (Boys’ Love) and GL (Girls’ Love) dramas and lakorns.
BLDUB offers a paid tier (BLDUB Premium) that unlocks higher video resolutions, ad-free viewing, and early access to new episodes of ongoing series. BLDUB was identified with thirteen (13) unique subdomains, domains, and IP addresses hosted on AS199834.
What is a favicon hash?
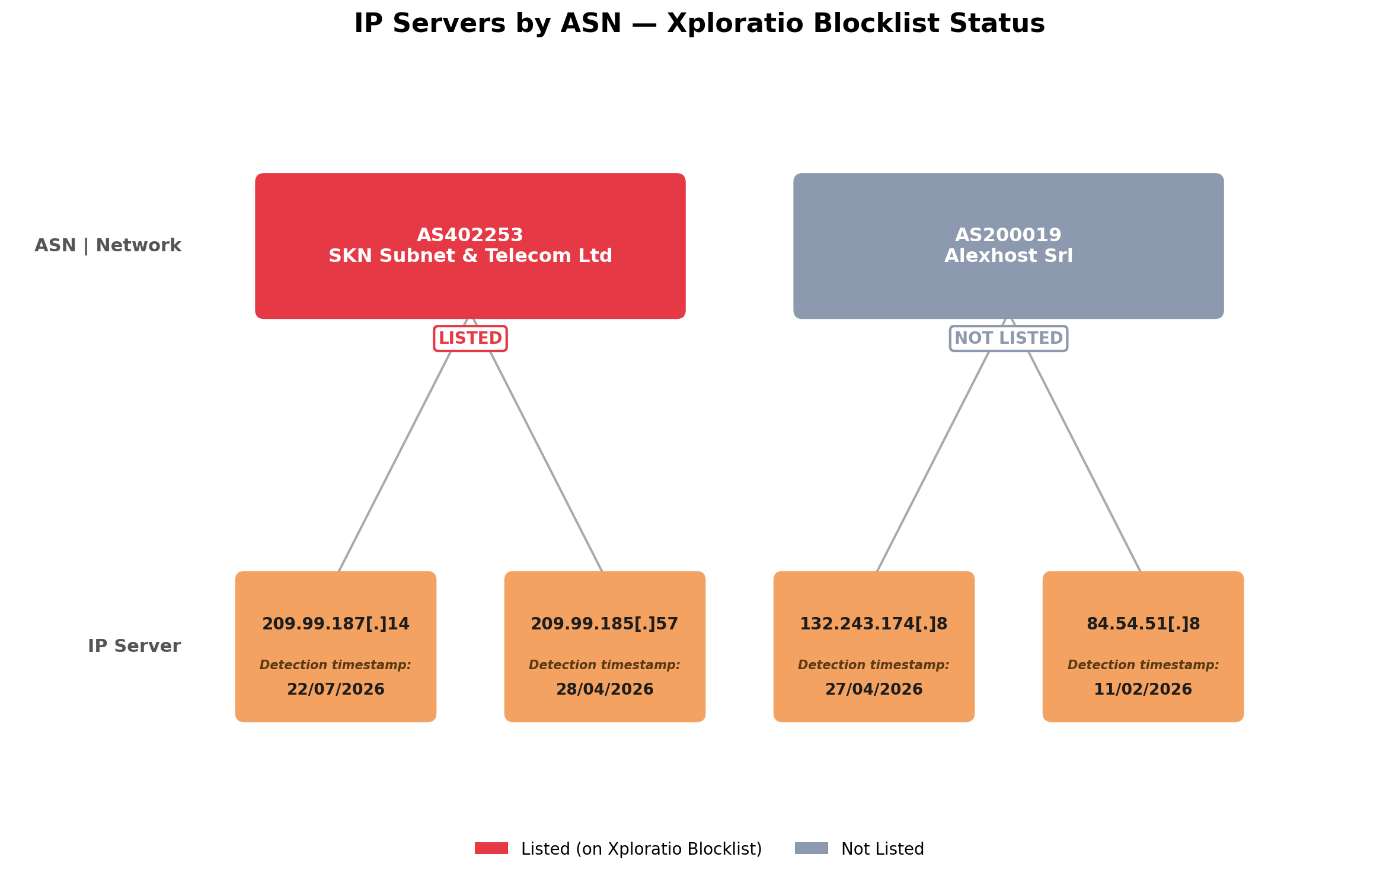
A favicon hash is a unique fingerprint generated from a website’s favicon — the small icon shown in a browser tab. Because operators often reuse the same favicon across related infrastructure, investigators can search for matching hashes across the internet (e.g., via Shodan, FOFA, or Censys) to uncover other servers or domains linked to the same operator.
A search for the favicon hash 1437934005 associated with bldub[.]com uncovered additional IP servers via fofa.info. A summary chart is provided below.
SOKOL VPN — Russian VPN service
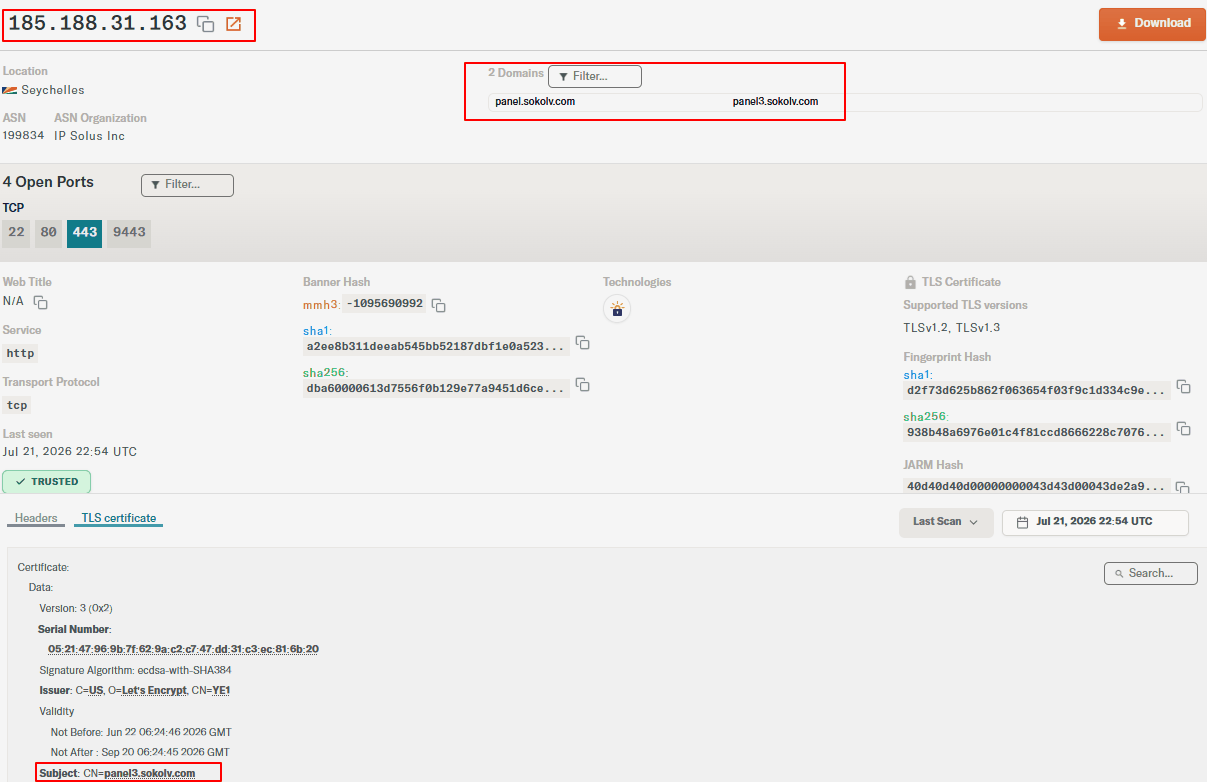
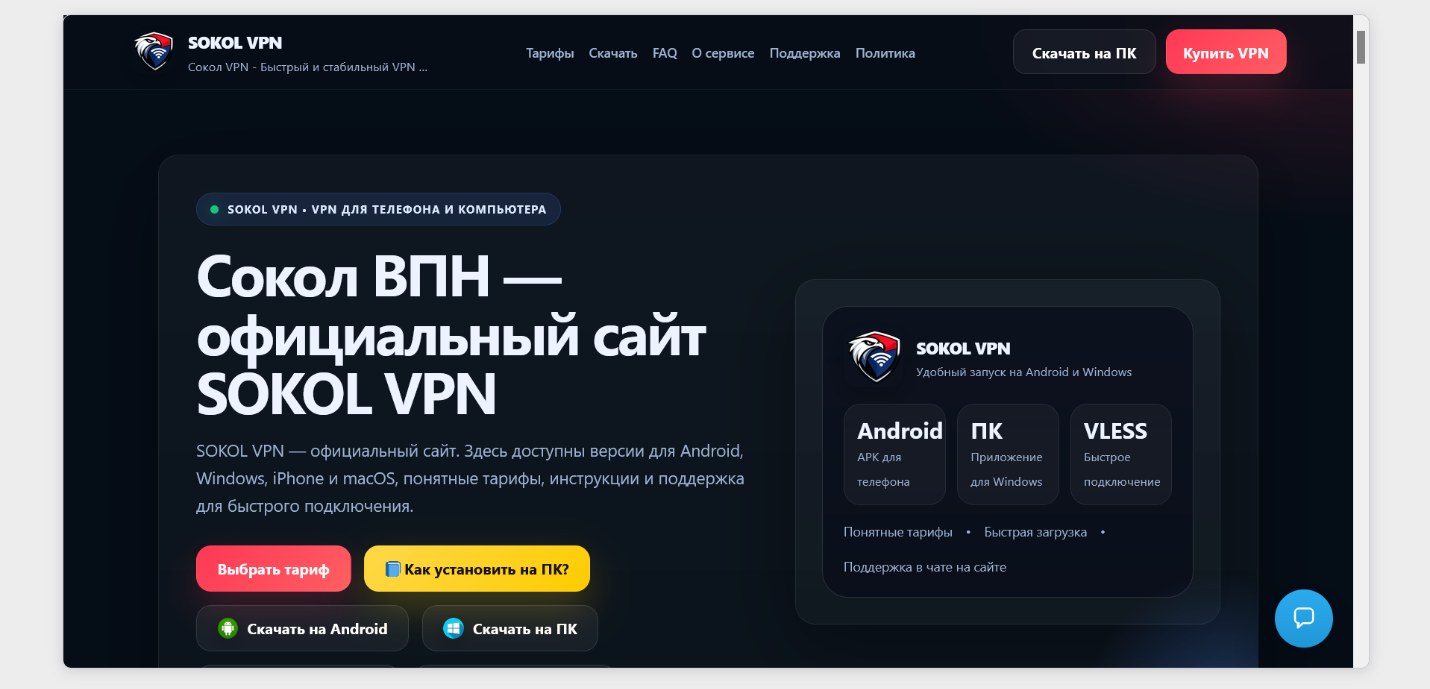
Sokol VPN (sokolv[.]com) was identified as a Russian VPN service. The subdomain panel.sokolv[.]com was hosted on IP address 185.188.31[.]163 at the time of scanning; sokolv[.]com now redirects to awerqsa[.]online.
Xploratio — Disruption Intelligence
This article was intended to show how ASN Intelligence, together with Xploratio’s verification and validation processes, works in practice. From here, further investigation strategies can be designed and implemented for the bulletproof network or the individual criminal networks identified, followed by disruption strategies across infrastructure, identities, and payment processors.