This article demonstrates how Xploratio’s attribution methodology works in practice. Our continuous monitoring of bulletproof hosting providers across darknet forums identified a seller operating on the Russian-language cybercrime forum Exploit[.]in. The seller, using the handle “Mehen”, joined the forum on 30 July 2026 and began posting advertisements — the listing below was posted on 10 August 2026 — for bulletproof VPS and dedicated servers hosted in the United States, the United Kingdom, and Russia.
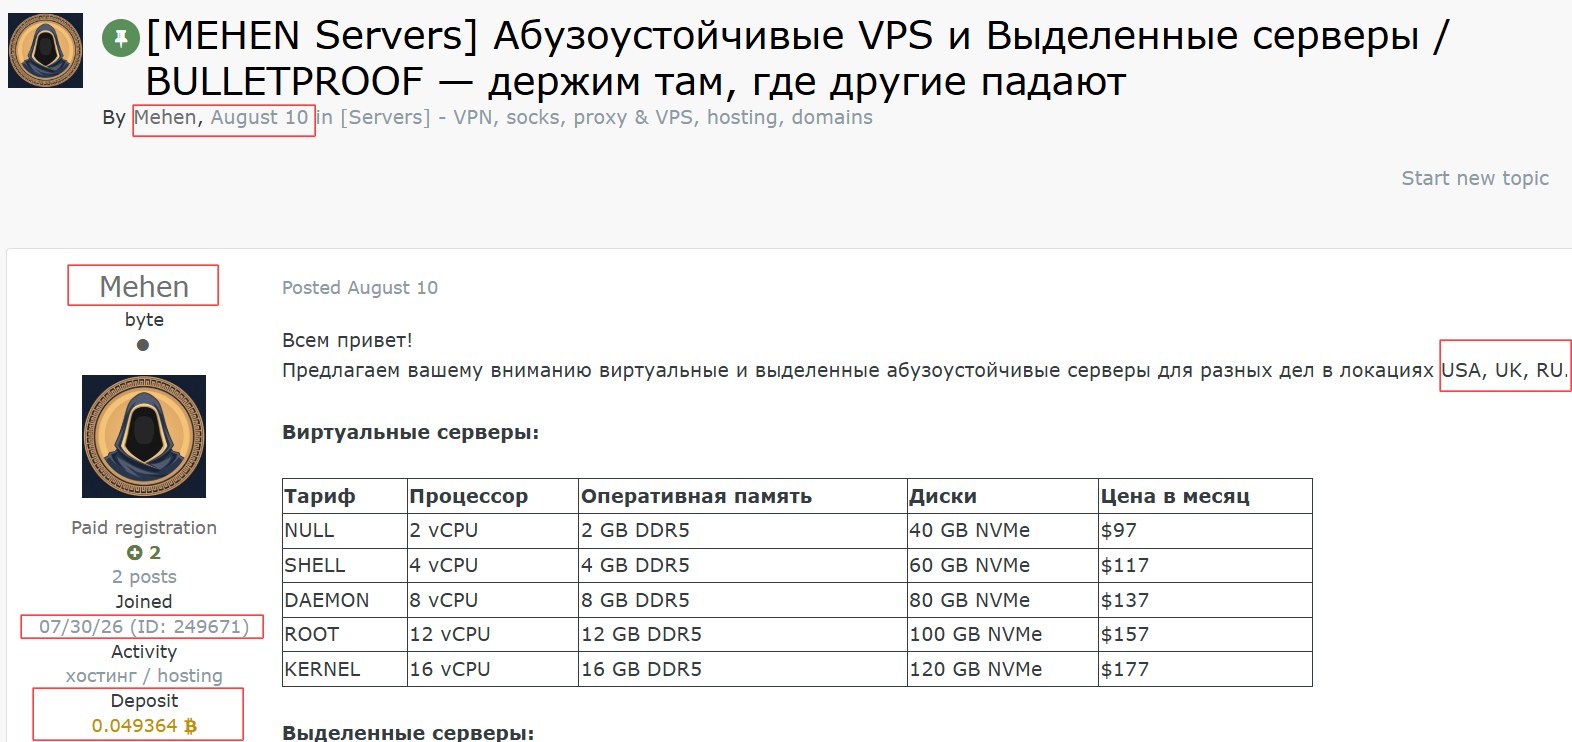
Additional information listed in the Exploit[.]in post led the Xploratio team to the seller’s Telegram account and public website, from which a controlled purchase was conducted to confirm the service and gather infrastructure details.
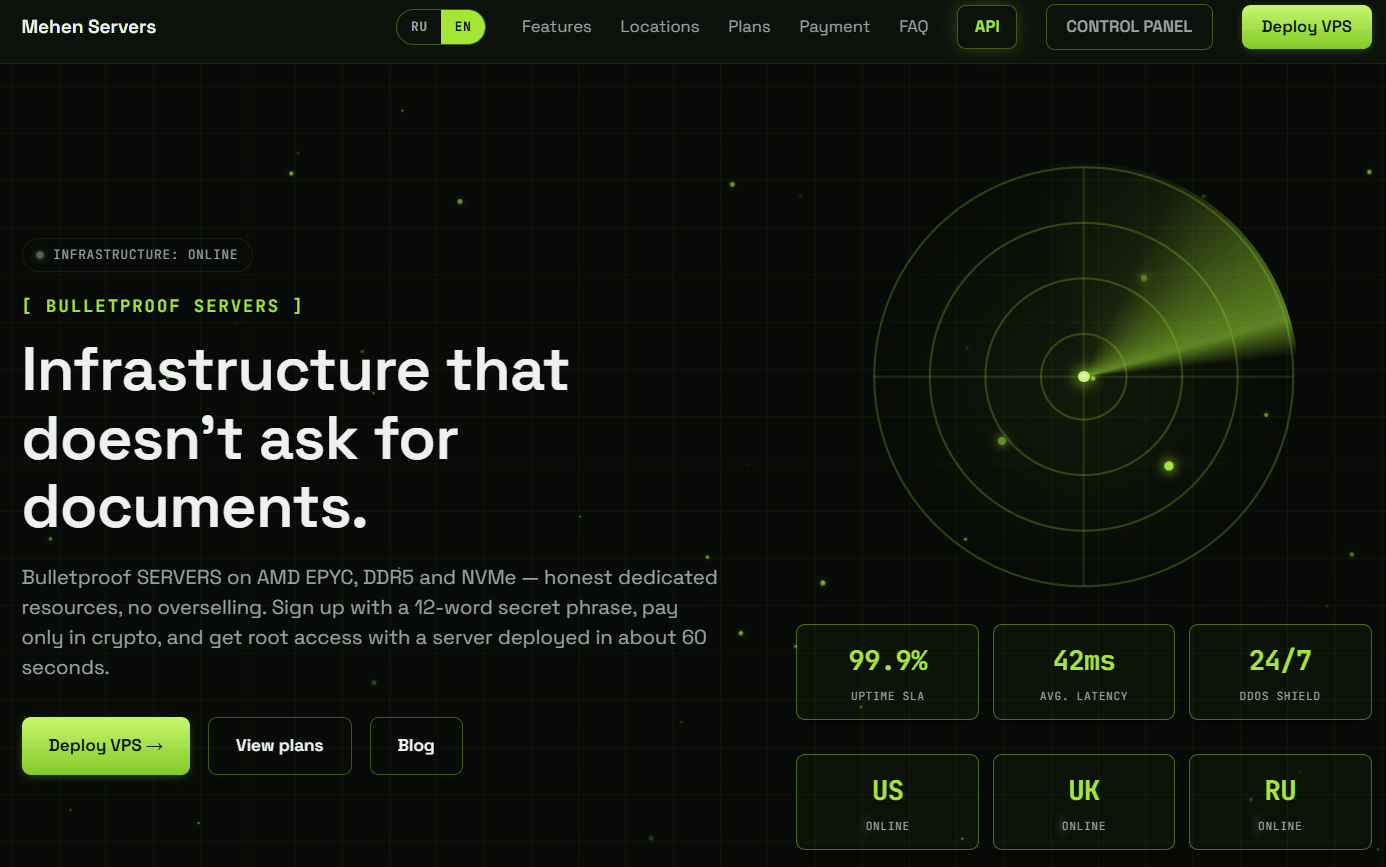
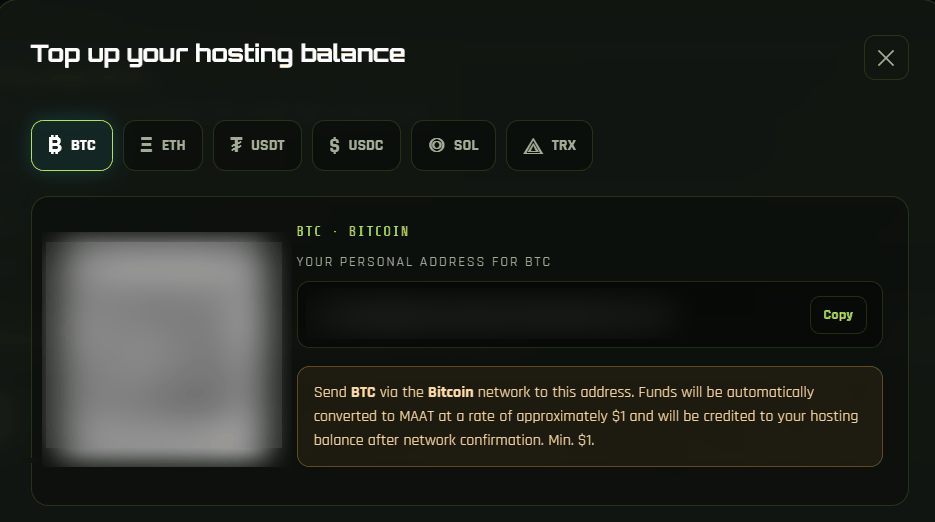
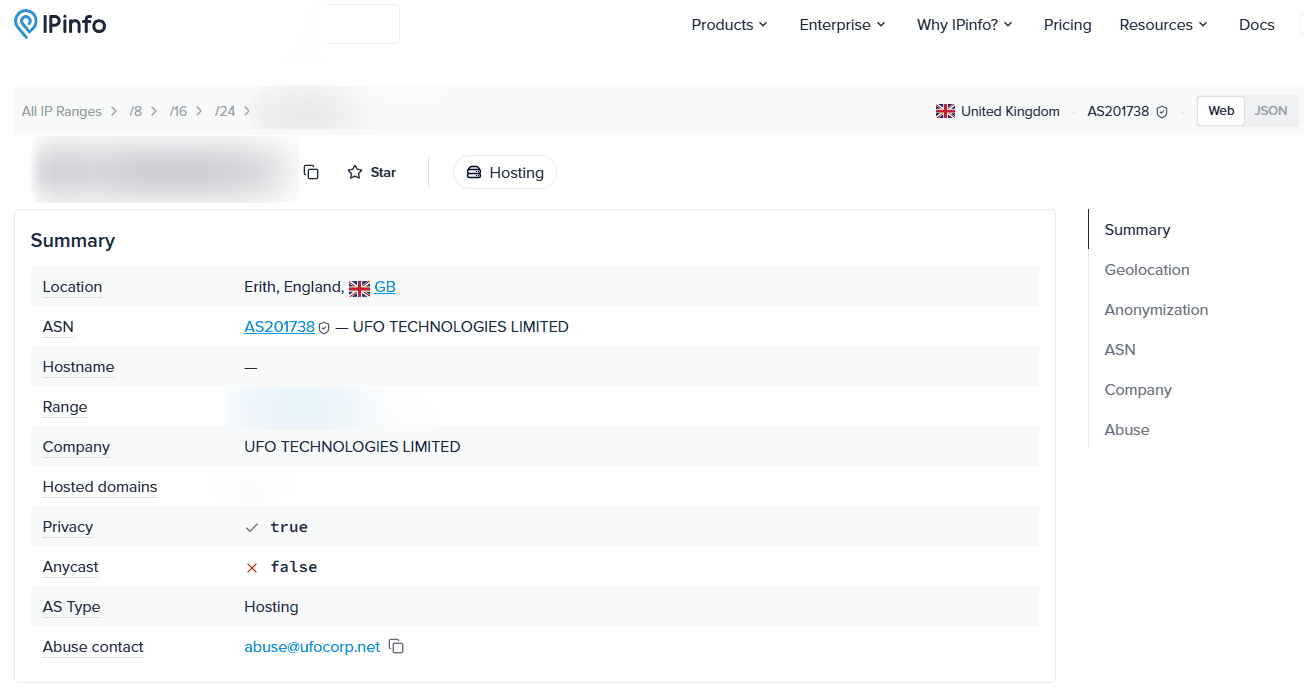
The purchased server was attributed to UFO Technologies Limited, a company incorporated in the United Kingdom on 9 February 2026 and controlled by a Russian operator. Open-source information links this operator by name to the “Bearhost” bulletproof hosting brand — a long-running name within the Russian-language bulletproof hosting scene.
UFO Technologies Limited is associated with multiple inactive and active ASNs on the Xploratio platform, including the recent ones, AS201738 and AS218974, both registered via RIPE NCC.
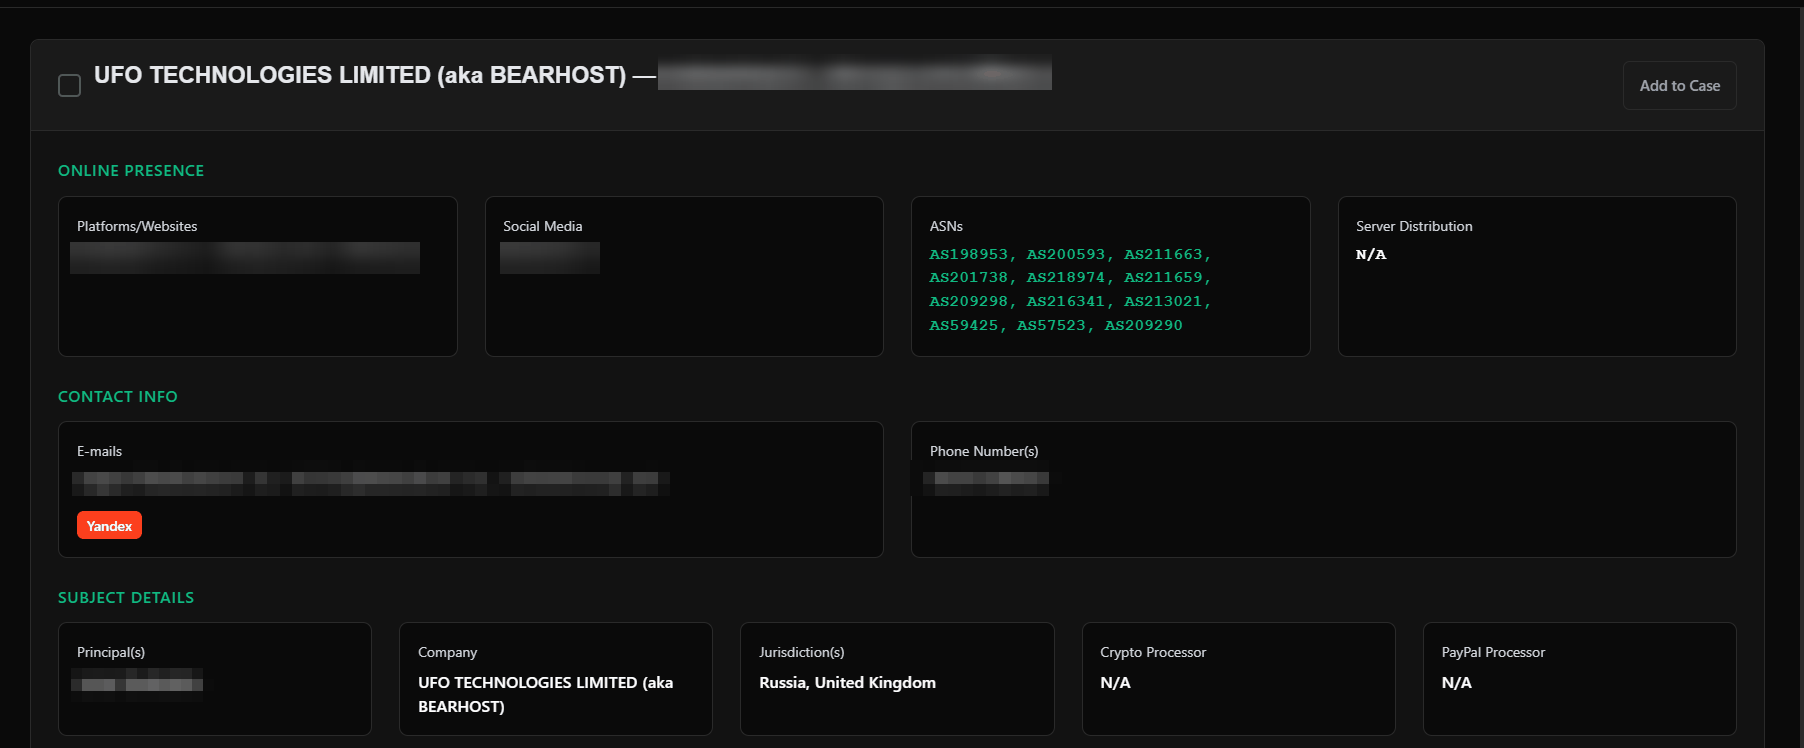
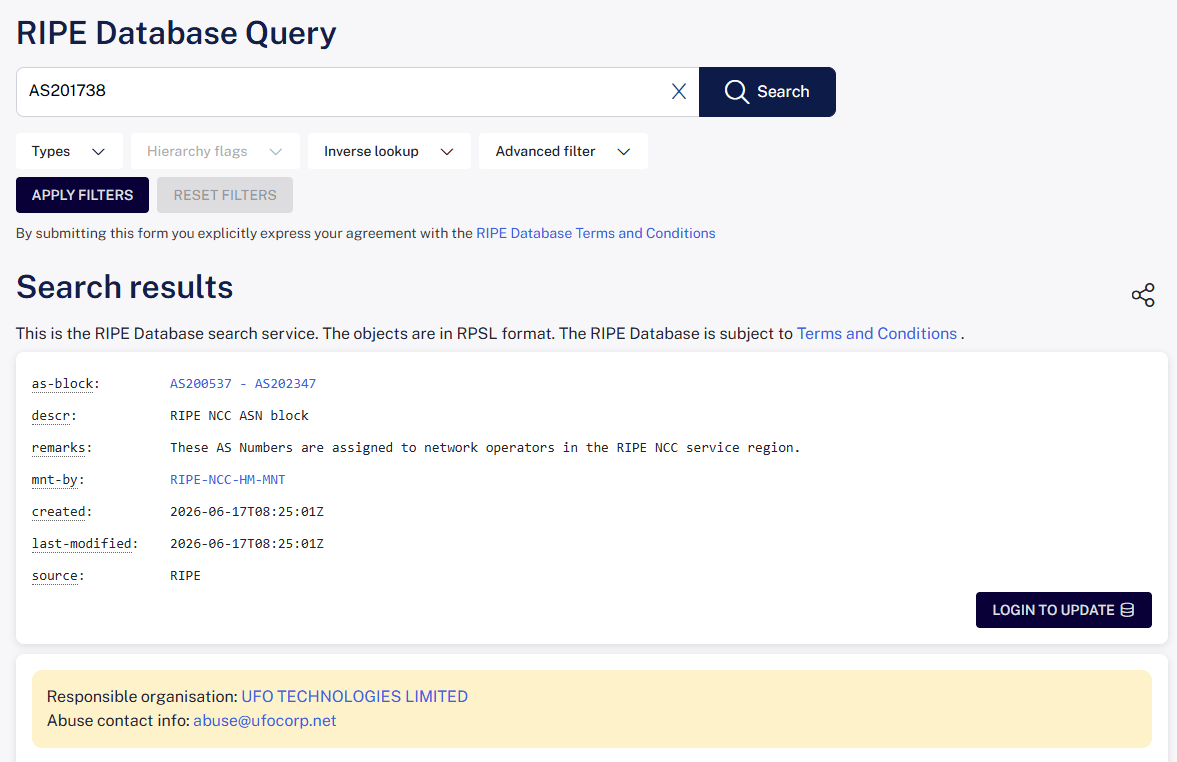
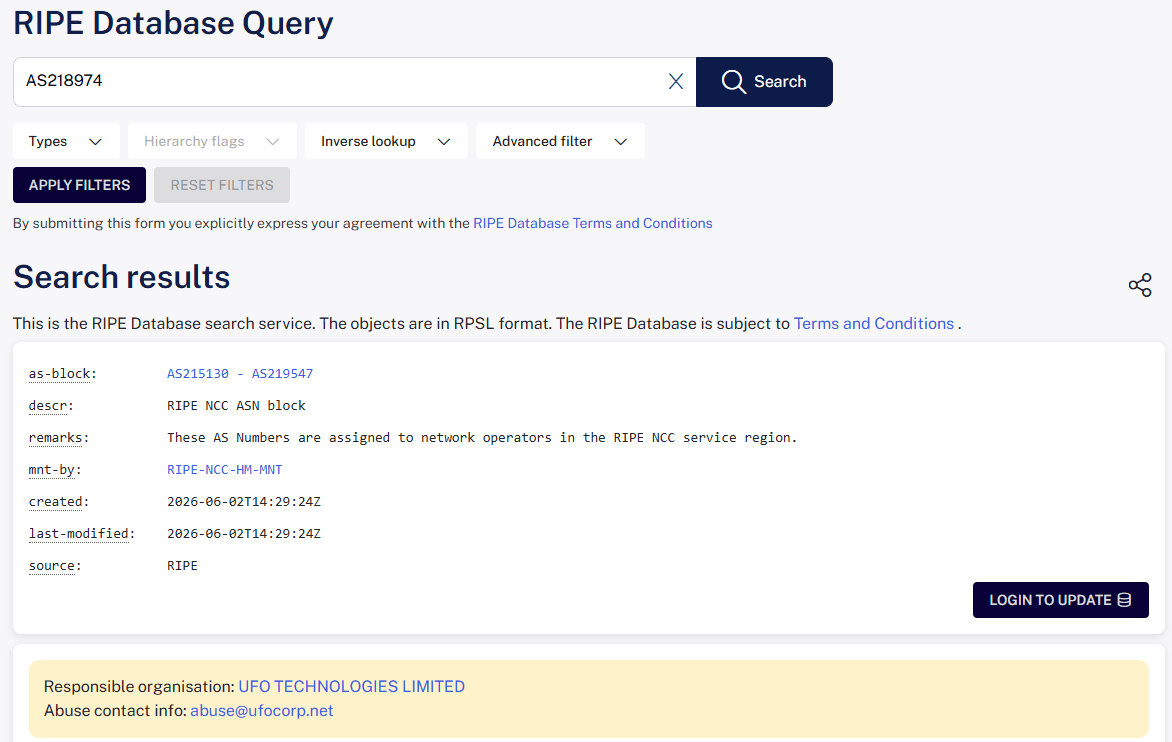
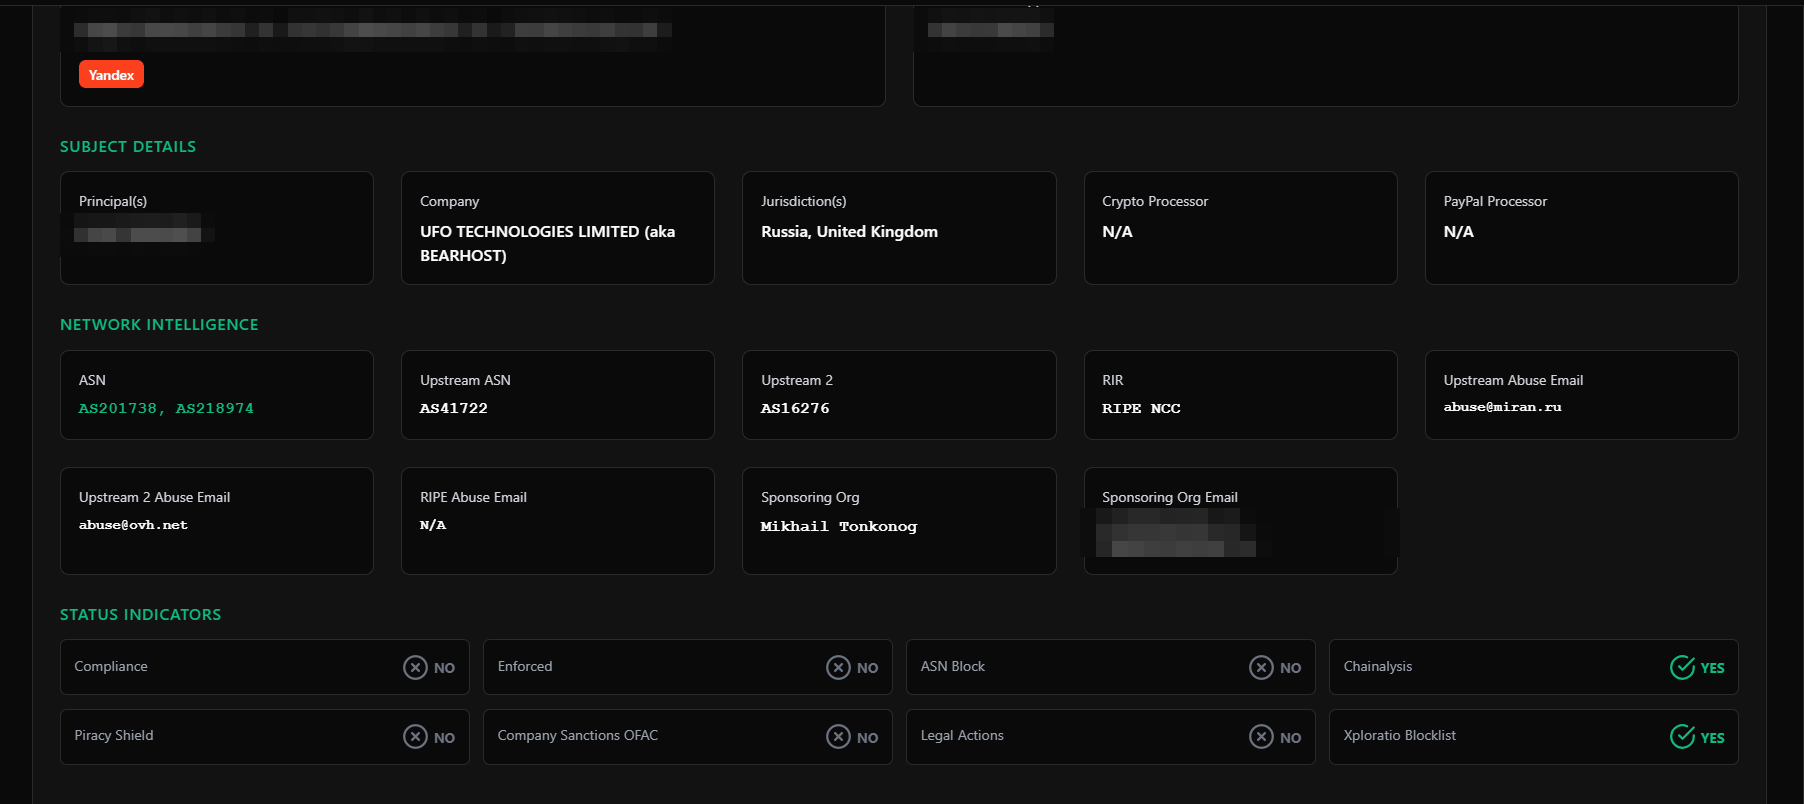
The hosting network is flagged on Xploratio’s ASN blocklist, owing to a high volume of infringing activity and/or a number of risky connections identified during our investigation.
AS201738 — Server Infrastructure
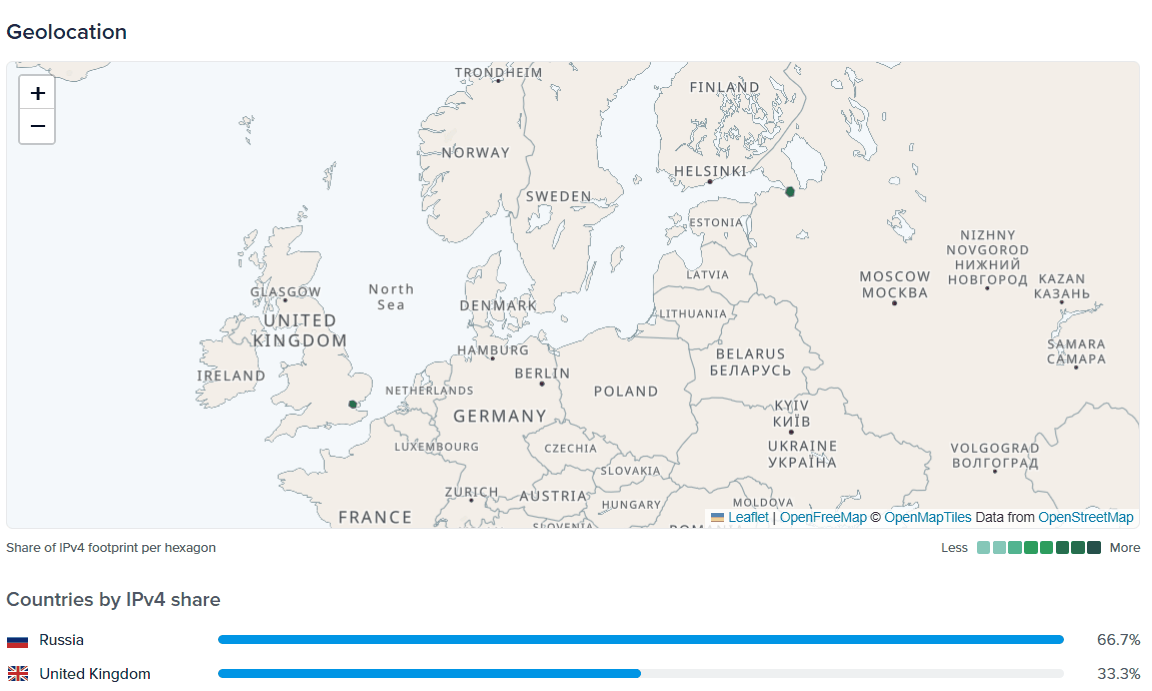
UFO Technologies Limited (AS201738) has 66.7% of its announced IPv4 space geolocated to Saint Petersburg, Russia, and 33.3% to Erith, United Kingdom, via ipinfo.io (Figure 9).
Table 1’s 84.5%/15.5% split is a count of individual traceroute measurements against the 129 domains identified by Xploratio during the investigation. Only two of the three announced IPv4 prefixes currently carry any of the 129 hosted domains (109.238.86.0/24, tracerouting to Erith, UK; and 193.178.158.0/24, tracerouting to Saint Petersburg, Russia). The third, 91.240.118.0/24, hosts none of them at present.
| Location | Traceroute records | Share |
|---|---|---|
| Erith, United Kingdom | 109 of 129 | 84.5% |
| Saint Petersburg, Russia | 20 of 129 | 15.5% |
Table 1. Traceroute test records by physical server location based on Xploratio’s investigation.
IP Space and Upstream Connectivity
UFO Technologies Limited (AS201738) announces three IPv4 prefixes:
- 91.240.118.0/24 — assigned to Chang Way Technologies Co. Limited (RIR: RIPE NCC); a previous company linked to the Russian operator managing UFO Technologies Limited
- 109.238.86.0/24 — assigned to UFO Technologies Limited via LIR Mikhail Tonkonog (RIR: RIPE NCC)
- 193.178.158.0/24 — assigned to UFO Technologies Limited via LIR Mikhail Tonkonog (RIR: RIPE NCC); transferred from IP Connect LLC (RIR: RIPE NCC) on 30 June 2026.
UFO Technologies Limited (AS201738) uses two upstream providers:
- AS41722 (Miran Ltd, Russia)
- AS16276 (OVH SAS, France)
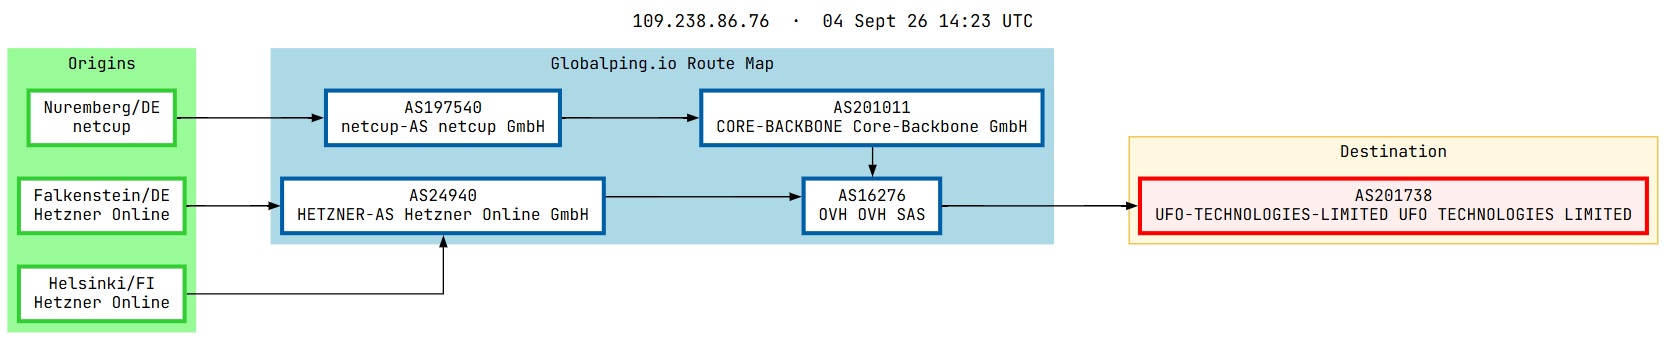
Hetzner Online GmbH is not a registered upstream of AS201738. It appears in Figure 10 because Threathunt.app runs this trace through Globalping, a network measurement platform whose probes are hosted across many providers worldwide. Two of the probes used for this trace, in Falkenstein and Helsinki, happen to run on Hetzner’s own network (shown under Origins in Figure 10), so the path passes through Hetzner as a first hop on its way to AS201738’s actual registered upstream, AS16276 (OVH). This is the physical route the packets take, not AS201738’s registered peering, and the same pattern appears again in AS132359’s traceroute below (Figure 22).
AS201738 — ASN Intelligence
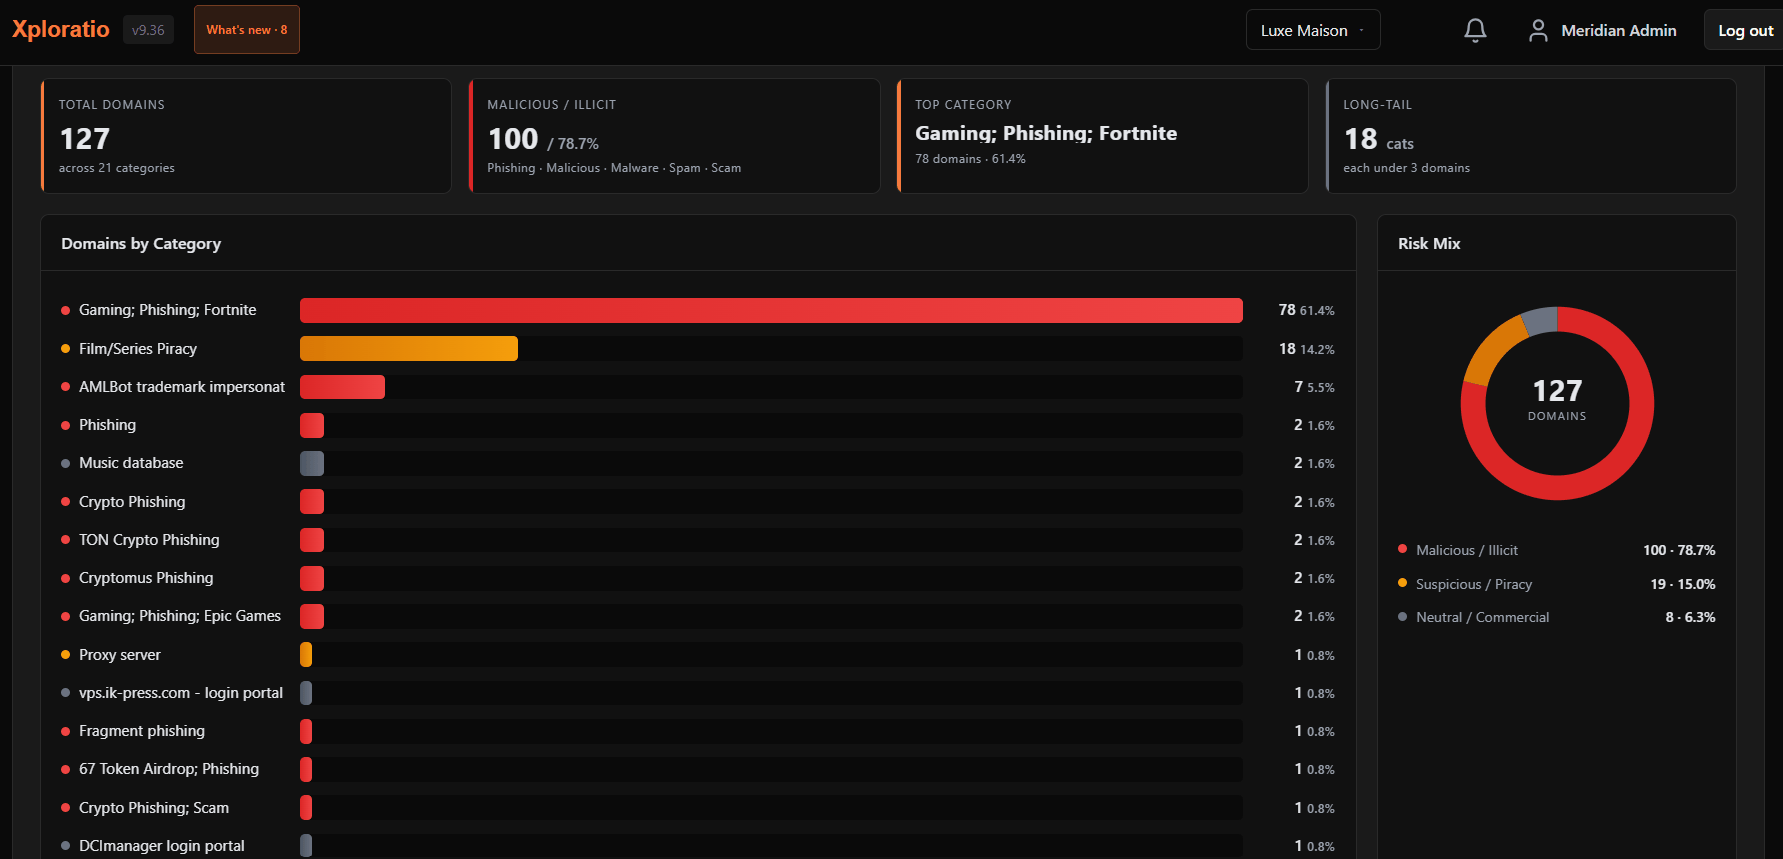
Xploratio’s ASN intelligence identified 127 domains hosted across AS201738, spanning 21 categories, of which 78.7% (100 domains) are malicious or illicit. The single largest category is gaming-related phishing targeting Fortnite, accounting for 61.4% of all hosted content (78 domains).
Figure 11 summarises the top 15 categories via the Xploratio platform; a thematic breakdown follows in Figure 12. The fuller records export analysed for this article contains 129 records (IP servers, subdomains, and domains), two more than this dashboard snapshot, after removing exact-duplicate export rows; every chart from this point on is drawn from that fuller record set.
127 of the 129 records carry an assigned category, matching Figure 11’s 21 categories exactly, while 2 subdomains do not (both already down or erroring at the time of review), and the dashboard’s per-category tally counts only categorised records. This includes records identified solely by IP address and reached via a specific port, such as the vps.ik-press[.]com and DCImanager login portals below, which are categorised and do appear in the 127 total.
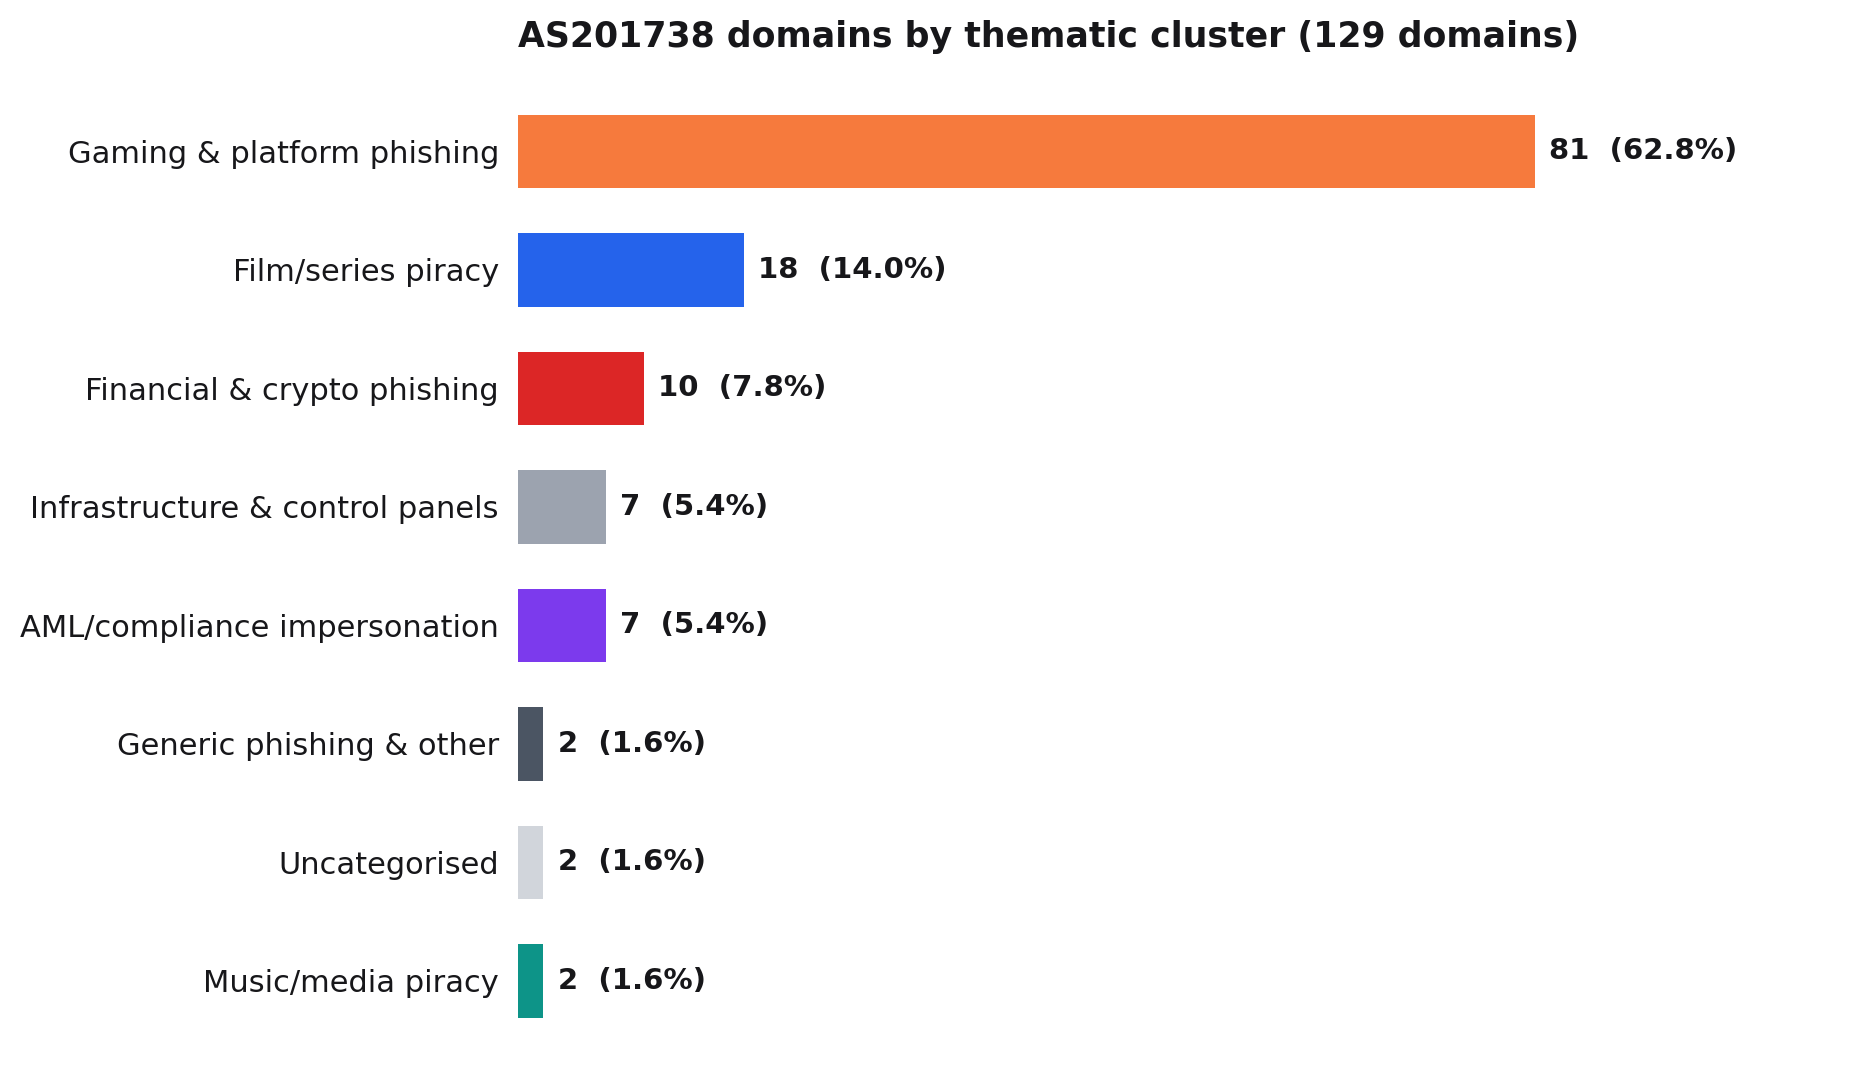
Grouping the 21 raw categories into thematic clusters, as Figure 12 shows, gaming and platform-impersonation phishing — principally targeting Fortnite — dominates the block, followed by film/series piracy and a long tail of financial and crypto-phishing lures.
Still Live: AS201738 Response Status
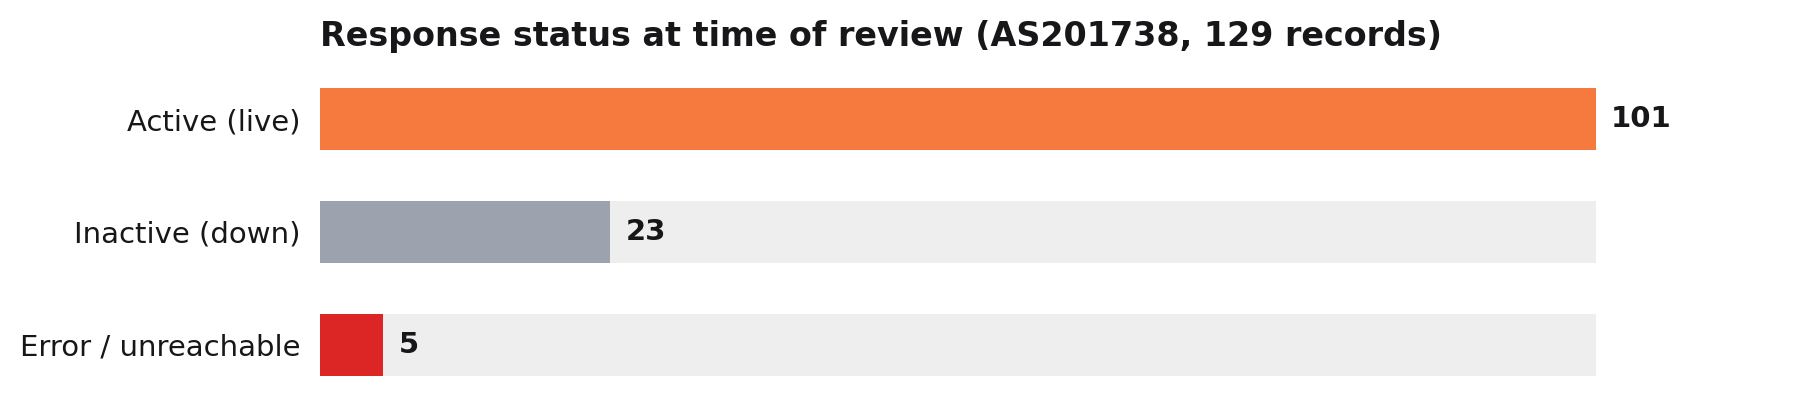
Response status at the time of review. Active is the actionable slice — everything else is already down or erroring.
Of AS201738’s 129 records, 101 (78.3%) currently respond as active, including three that redirect to a live third-party domain (fragment.com or cryptomus.com) rather than serving content directly; 23 (17.8%) are inactive and five (3.9%) return an HTTP error.
Named Networks or Campaigns Hosted on AS201738
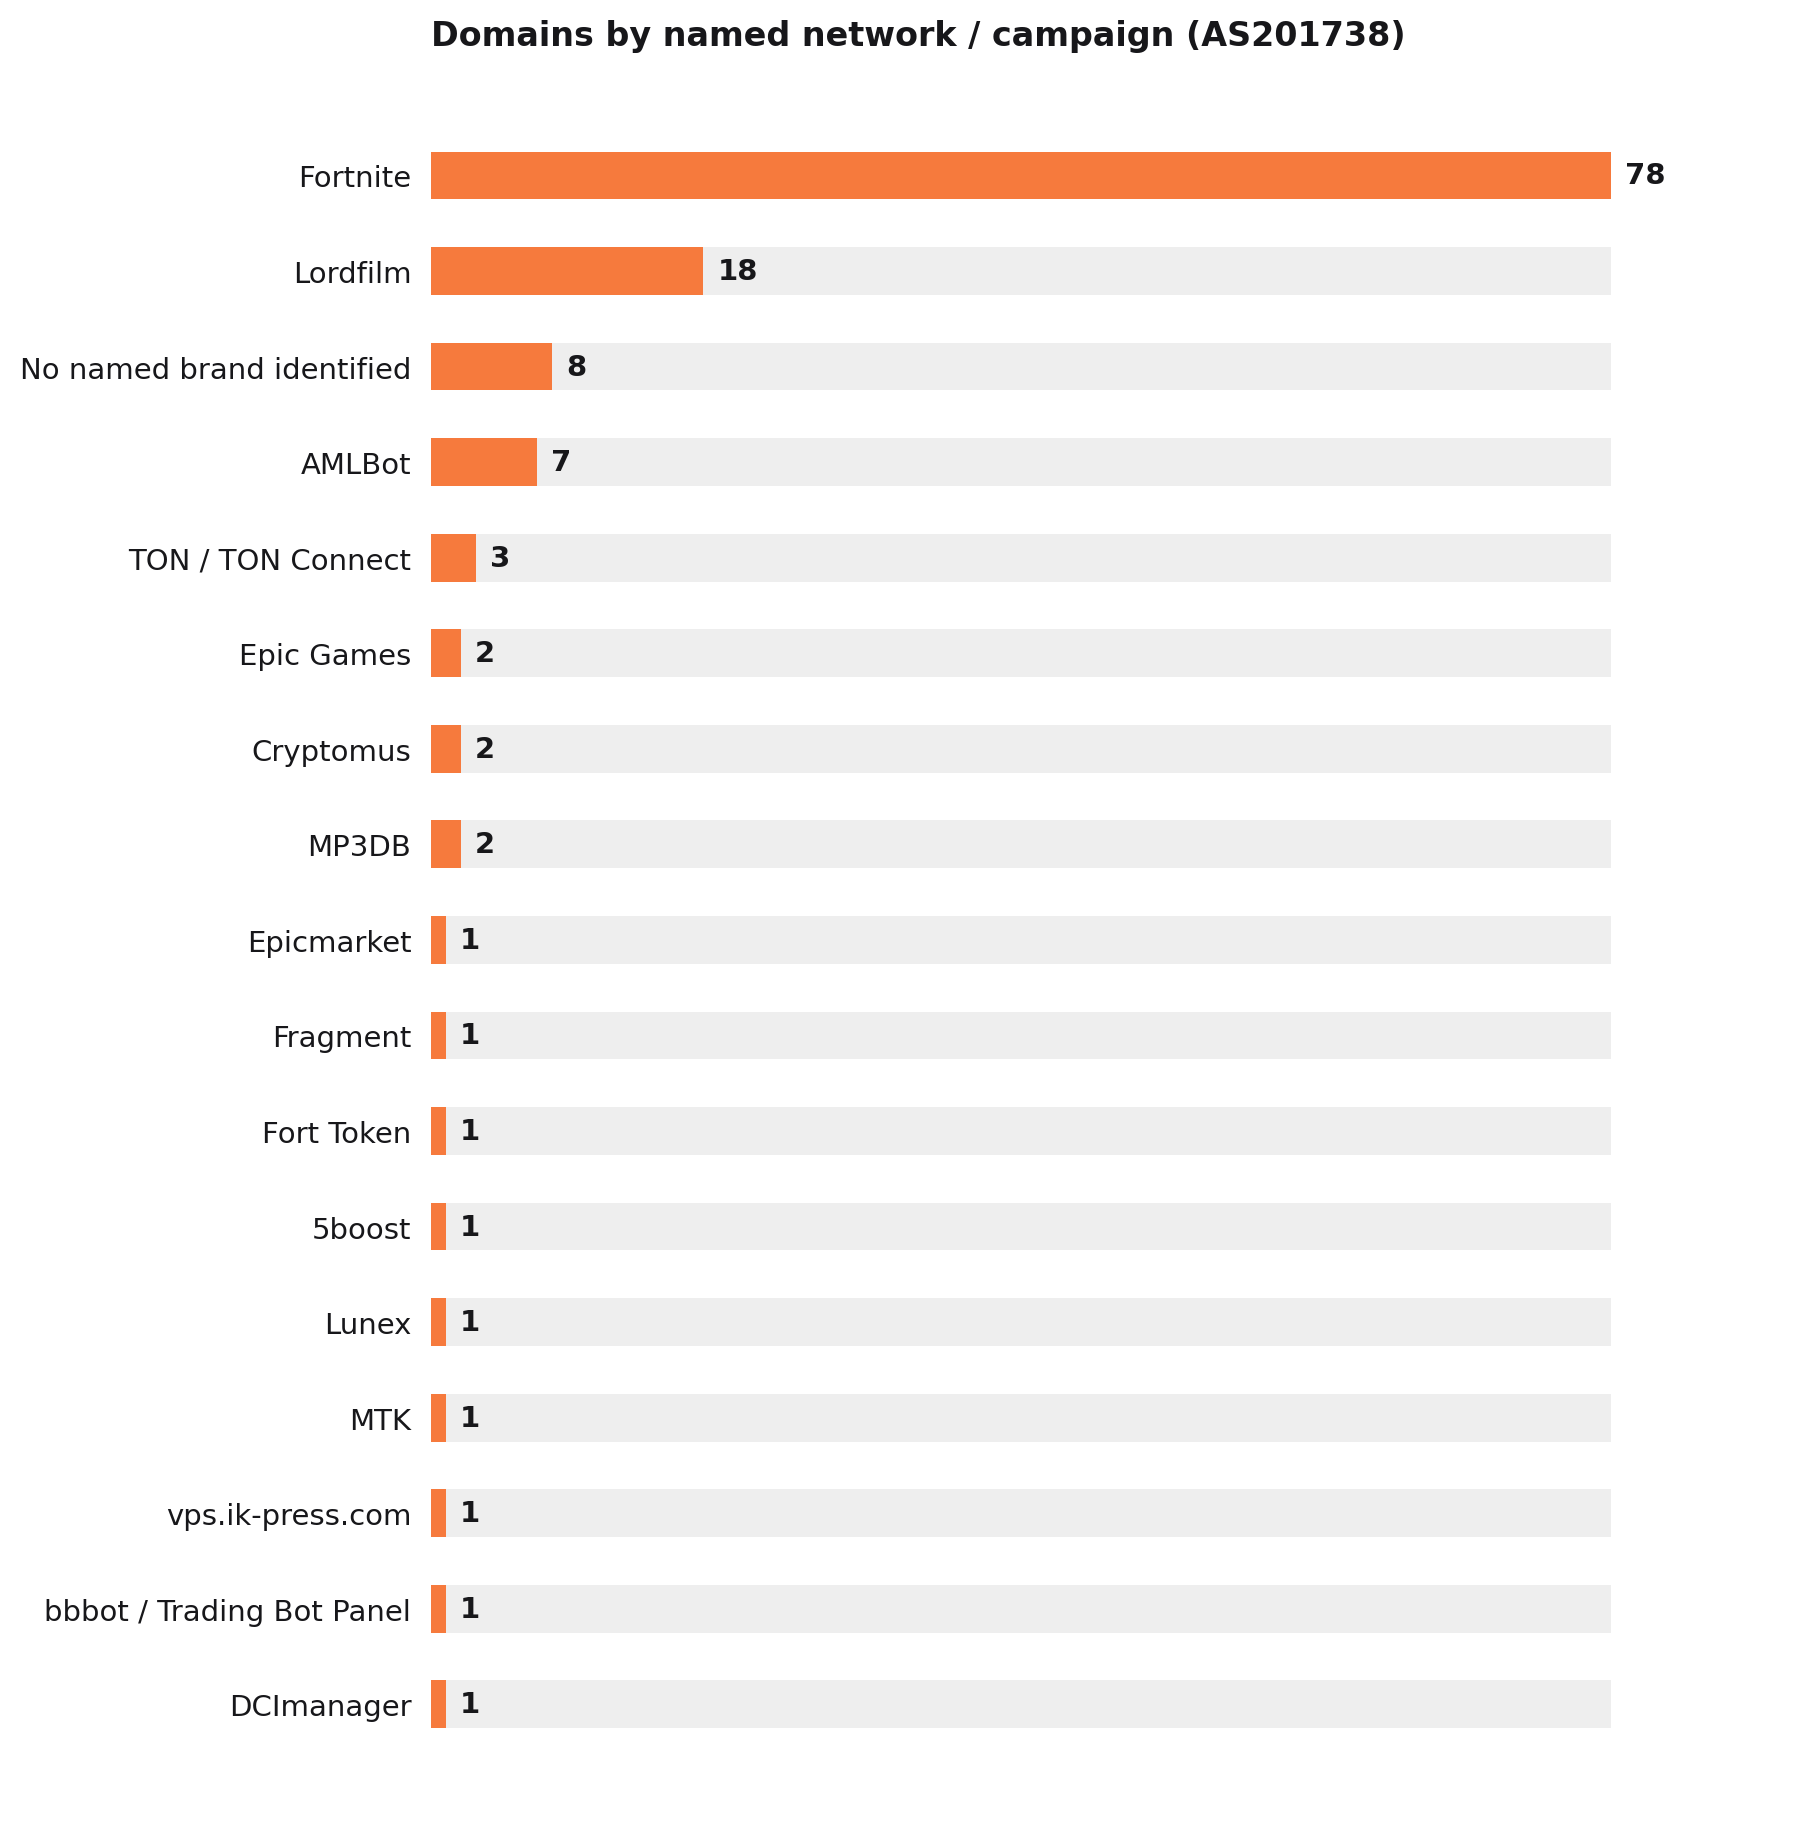
Xploratio’s export records a specific Network value for many hosts — the actual named campaign or infrastructure behind a listing, such as Lordfilm for the piracy mirrors or MP3DB for the music-database pages — which Xploratio uses directly where present. Where no Network value is recorded, Xploratio falls back to the brand named in the category itself (for example, grouping “TON Crypto Phishing” with “TON Connect; Phishing” under TON).
The chart below ranks the resulting named networks by domain count; totals reconcile to all 129 records on the block.
Threat Composition by Host on AS201738
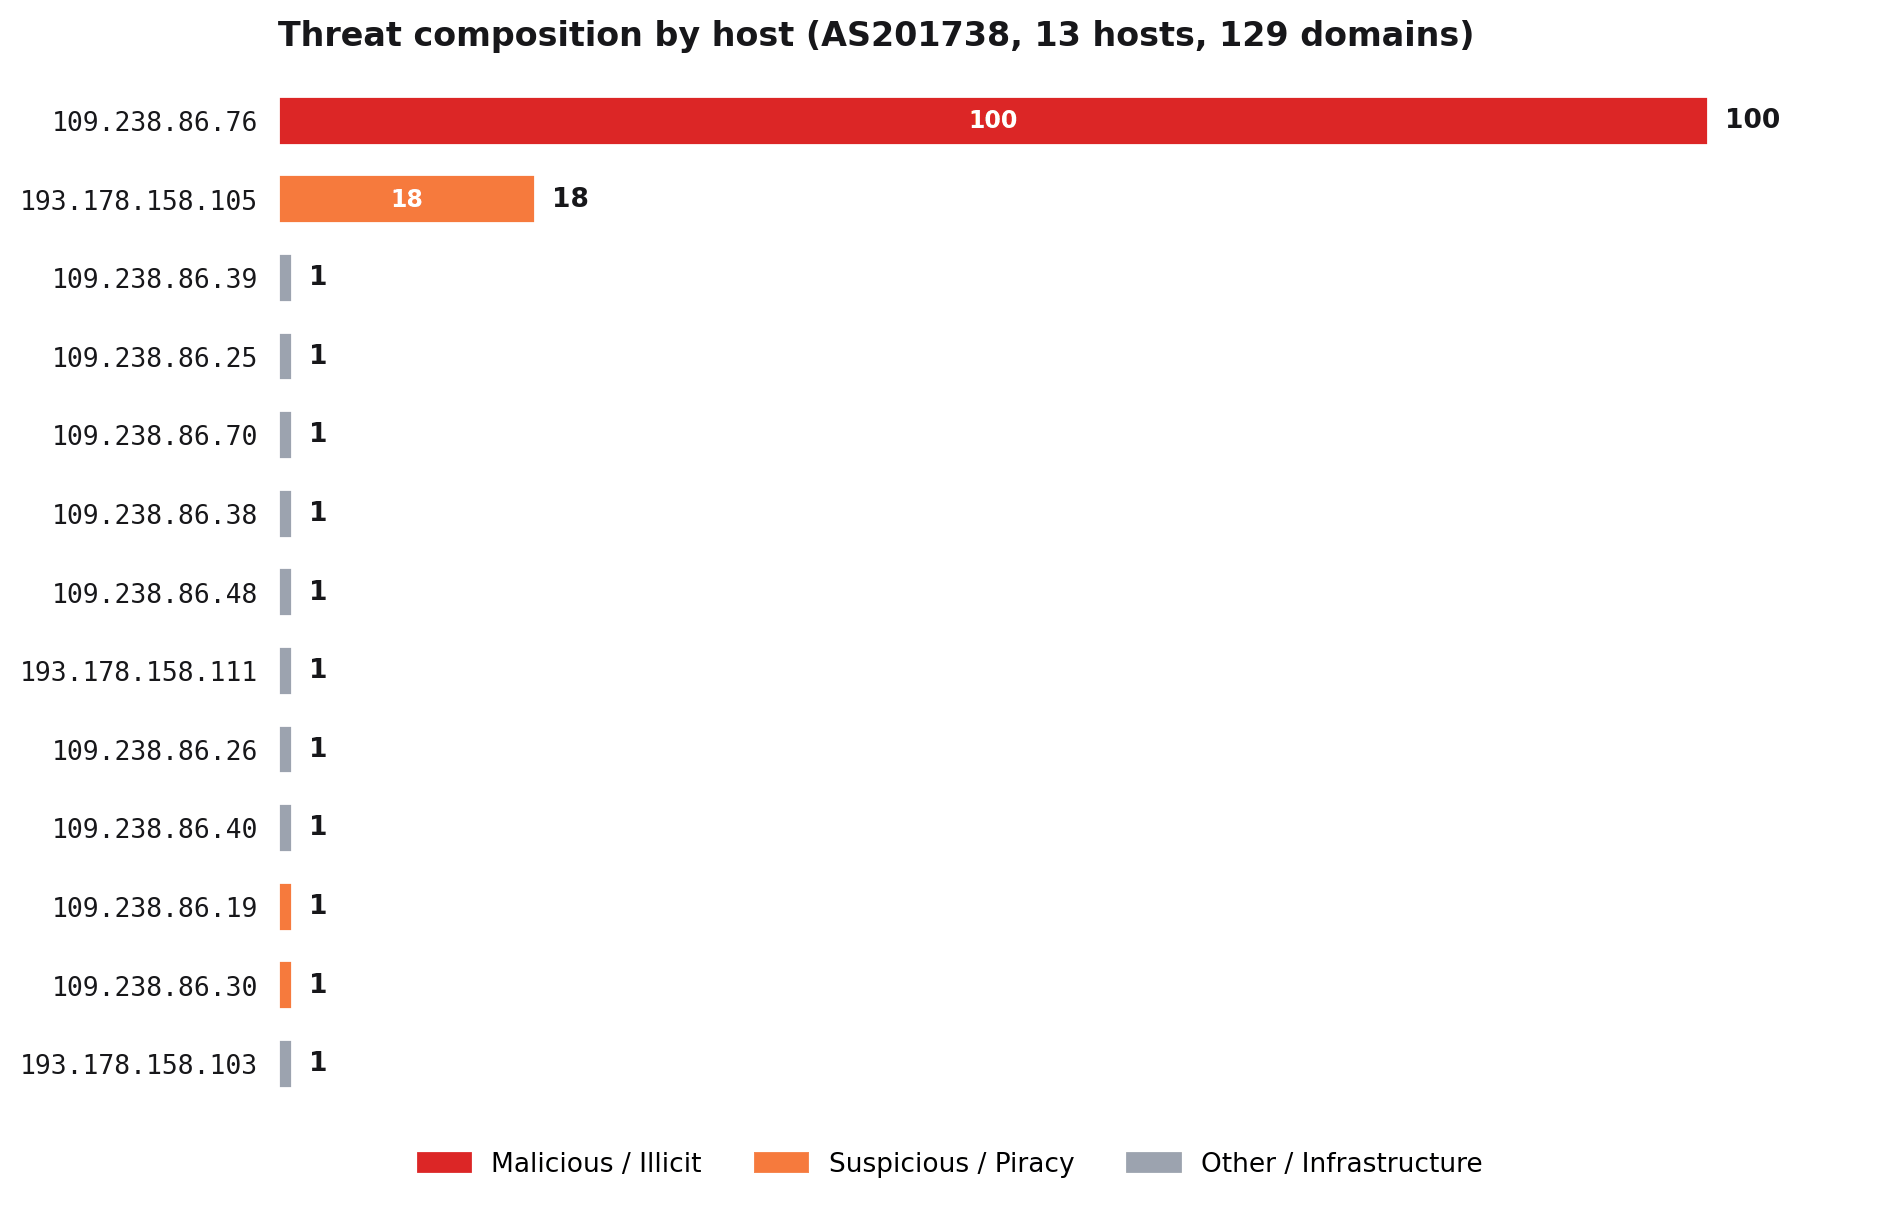
The chart below groups all 129 records by their 13 distinct hosts, showing the risk mix (Malicious/Illicit, Suspicious/Piracy, or Other/Infrastructure) at each one. A single host, 109.238.86[.]76, carries all 100 of the block’s Malicious/Illicit domains, including the 78 Fortnite-branded gaming-phishing domains and a further 22 domains across other gaming and crypto-phishing brands (AMLBot, Epic Games, Cryptomus, TON, and others). The Lordfilm piracy mirrors sit together on 193.178.158[.]105. The remaining eleven hosts are single-purpose infrastructure (login portals, a proxy, a devops box) each serving one or two records.
Hosted Content on AS201738 — Examples
1. LordFilm — Film/Series Piracy
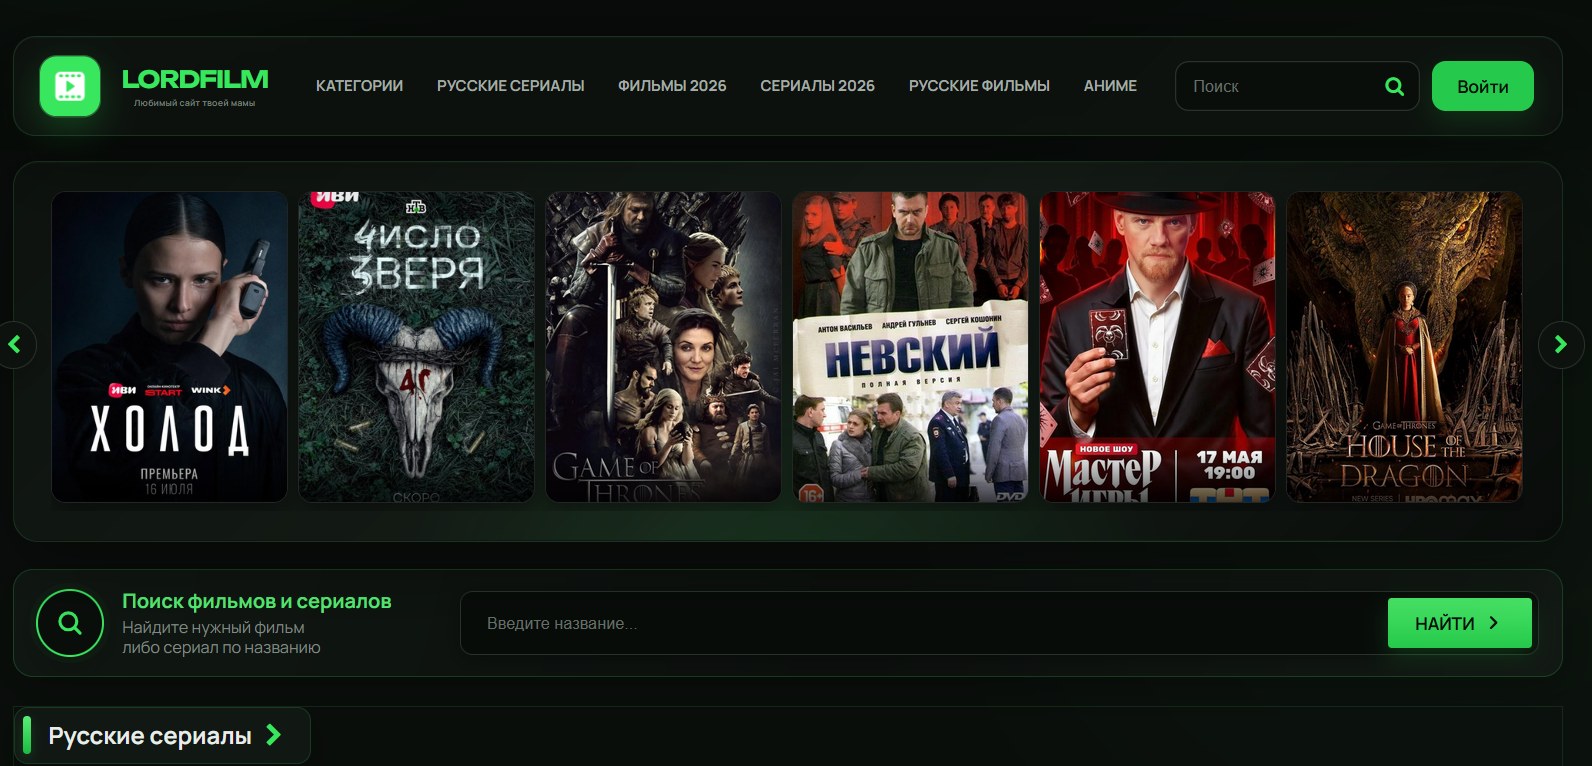
LordFilm (lordfilm[.]mom, and its many mirror domains) is a long-running Russian-language film and television piracy platform, offering unlicensed streaming of current cinema releases and TV series without payment or subscription. Piracy platforms of this kind are typically hosted on bulletproof or abuse-tolerant infrastructure precisely because their business model depends on evading takedown requests from rights holders.
2. Fortnite-Related Phishing — Gaming Phishing
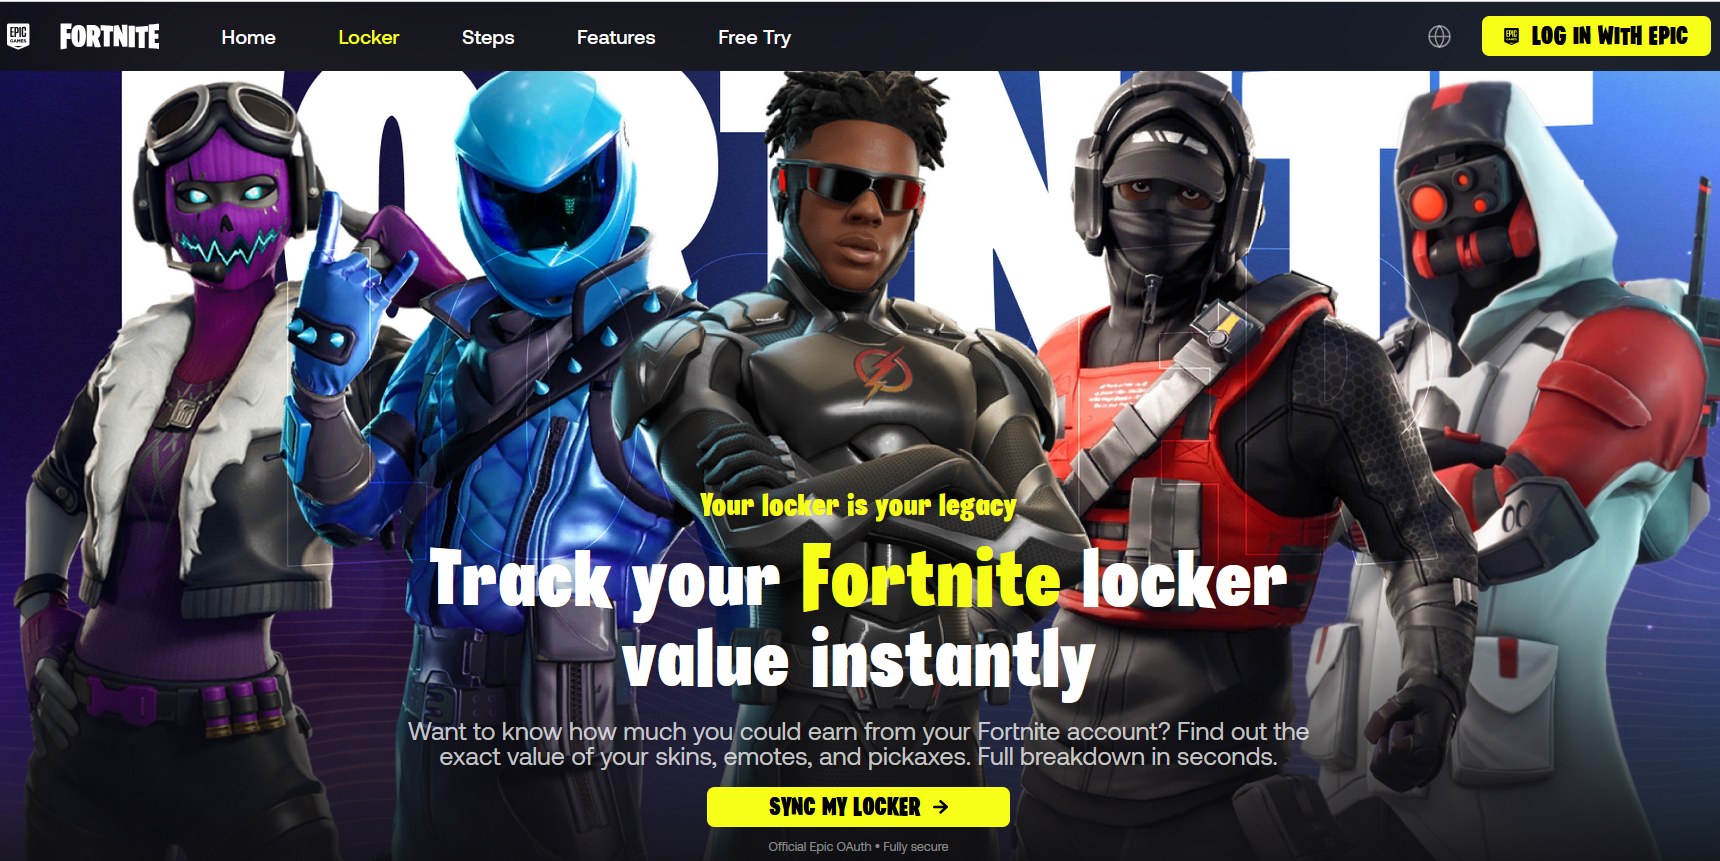
This example impersonates a third-party “Fortnite locker value” tracking tool, luring victims with the promise of valuing their in-game skins and items and prompting them to authenticate via a spoofed Epic Games OAuth flow to “sync” their account. Credentials or session tokens harvested this way are then used to hijack the victim’s Epic Games account and its associated inventory. This template forms part of the 78 domains tagged Gaming; phishing; Fortnite on AS201738 — the single largest content category identified (see AS201738 — ASN Intelligence).
3. TON Crypto Phishing
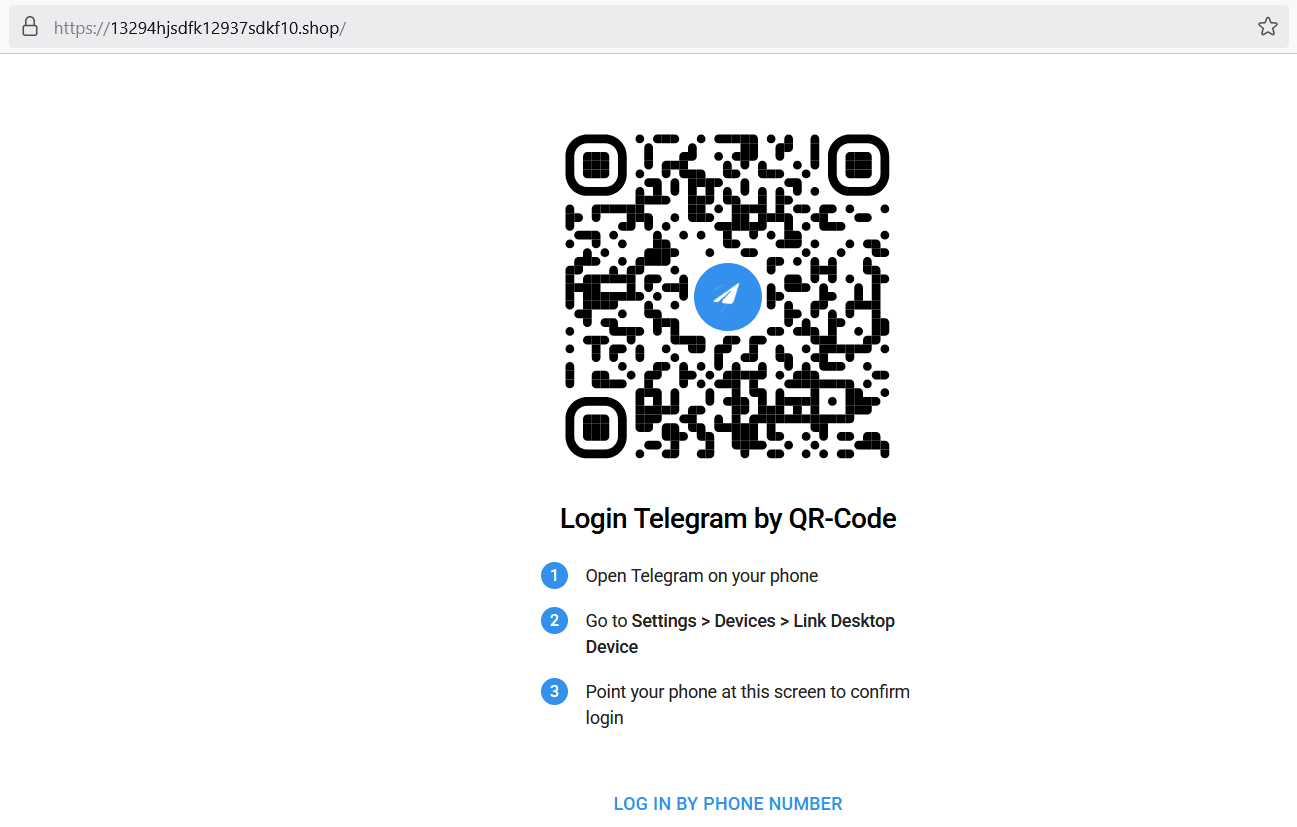
This example presents a spoofed Telegram “Login by QR-code” page. Victims who scan the QR code with their Telegram app unknowingly authorise a new device session, handing the attacker full control of the victim’s Telegram account — a technique frequently used as a precursor to TON (The Open Network) wallet and crypto-asset theft, given Telegram’s native integration with the TON blockchain. This domain is one of two websites tagged TON Crypto Phishing on AS201738.
IP Migration — Traceability
IP migration is the process by which a domain, or a cluster of domains, is moved from one hosting provider to another. Phishing and high-risk piracy campaigns are frequently run from bulletproof infrastructure precisely because it resists takedown; when a host complies with abuse requests — directly, or indirectly via its upstream provider — operators typically migrate their domains to another bulletproof host. Migration can also happen for reasons unrelated to enforcement: campaigns are often short-lived and dynamic by nature, and operators may spread domains across multiple providers simultaneously, or relocate them once a campaign has run its course.
Xploratio traces these migration patterns between bulletproof hosts to build a clearer picture of which providers are used for which malicious campaigns over time.
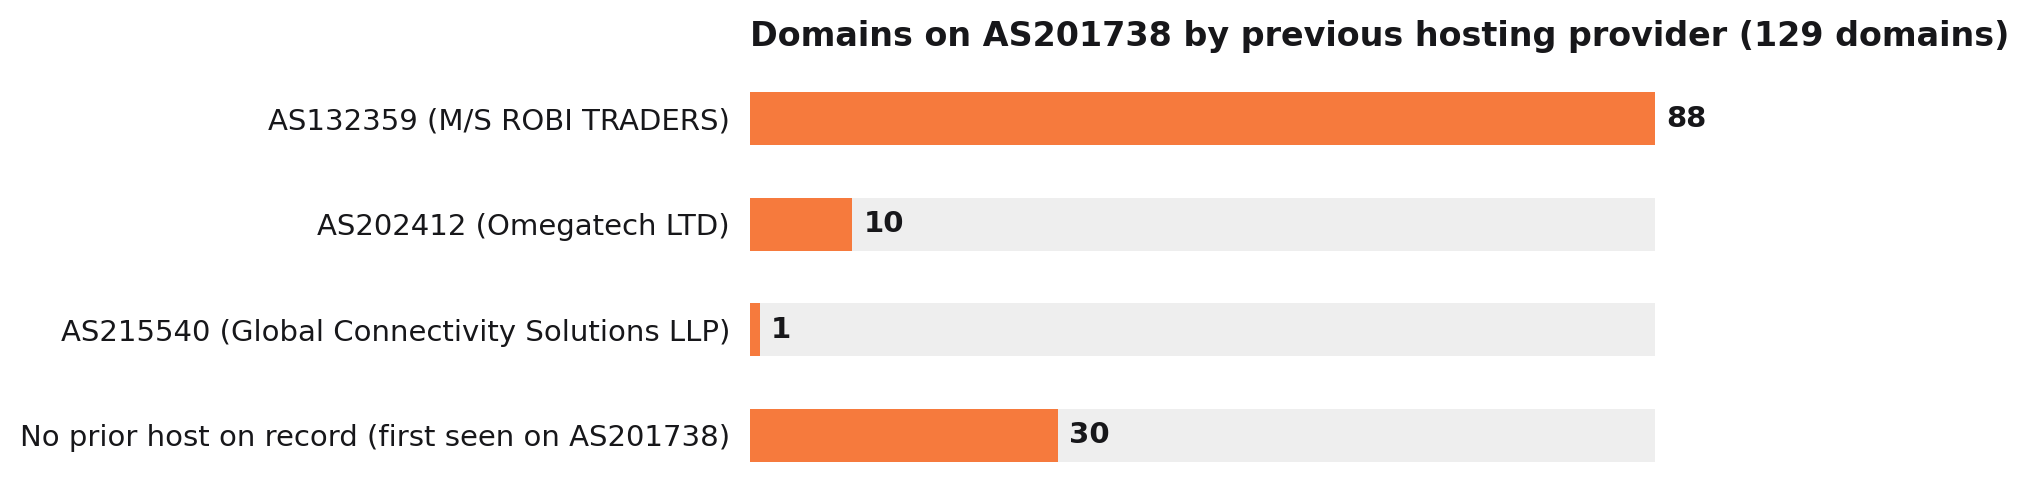
Xploratio identified domains that migrated to AS201738 from two other bulletproof providers: AS202412 (Omegatech LTD) and AS132359 (M/S ROBI TRADERS). A third network observed in the migration history, Global Connectivity Solutions LLP, is not assessed as bulletproof hosting. Of AS201738’s 129 records, 99 carry a recorded previous IP address and origin ASN: 88 migrated from AS132359, ten from AS202412, and one from AS215540 (Global Connectivity Solutions LLP); the remaining 30 have no prior host on record, meaning they were first seen on AS201738.
Further Pivoting: AS132359 (M/S ROBI TRADERS)
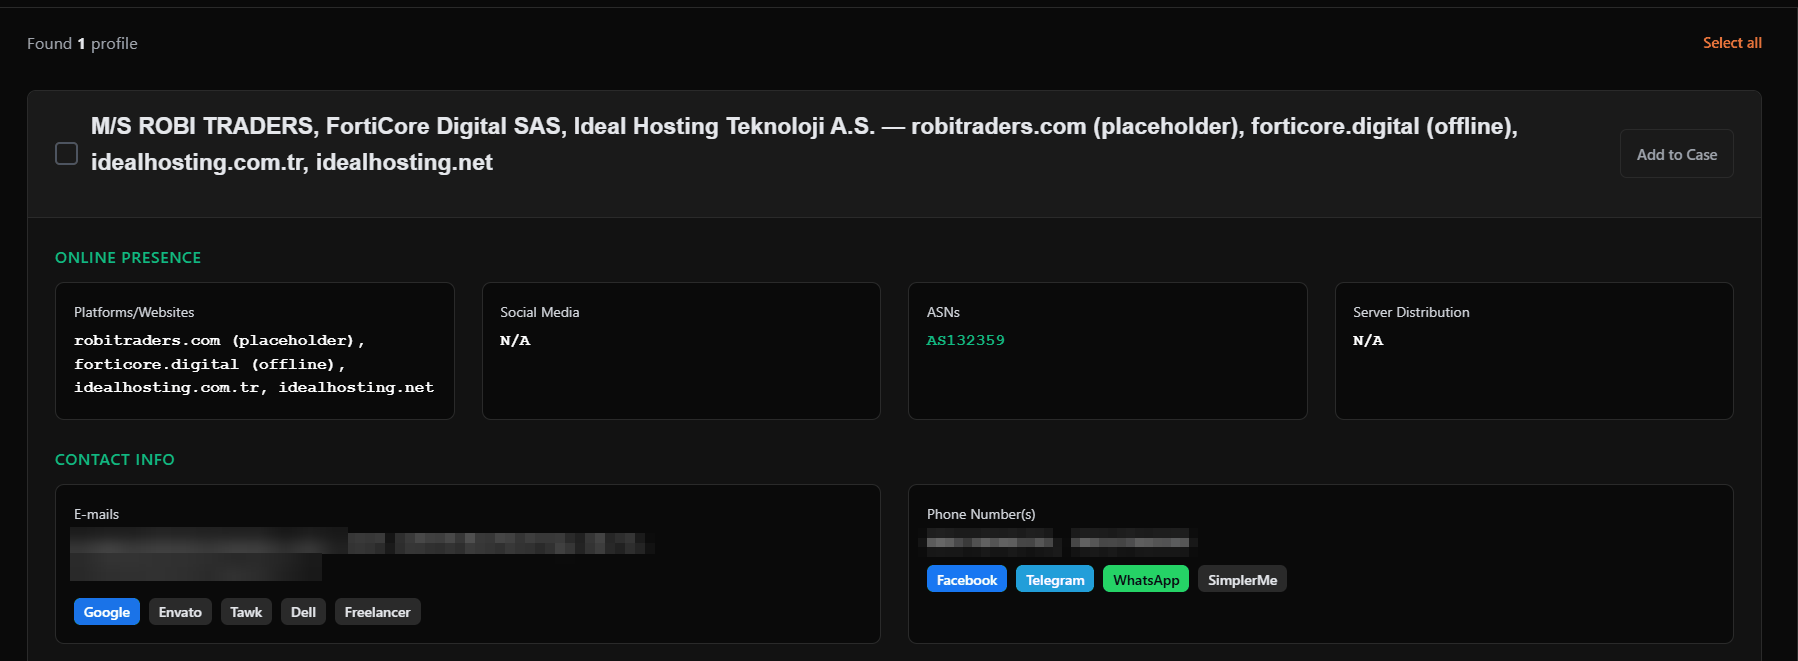
Xploratio pivoted its investigation to AS132359 (M/S ROBI TRADERS), one of the two bulletproof providers identified above as a source of domains migrating onto AS201738. AS132359 is itself flagged on Xploratio’s ASN blocklist, shown in the platform view below.
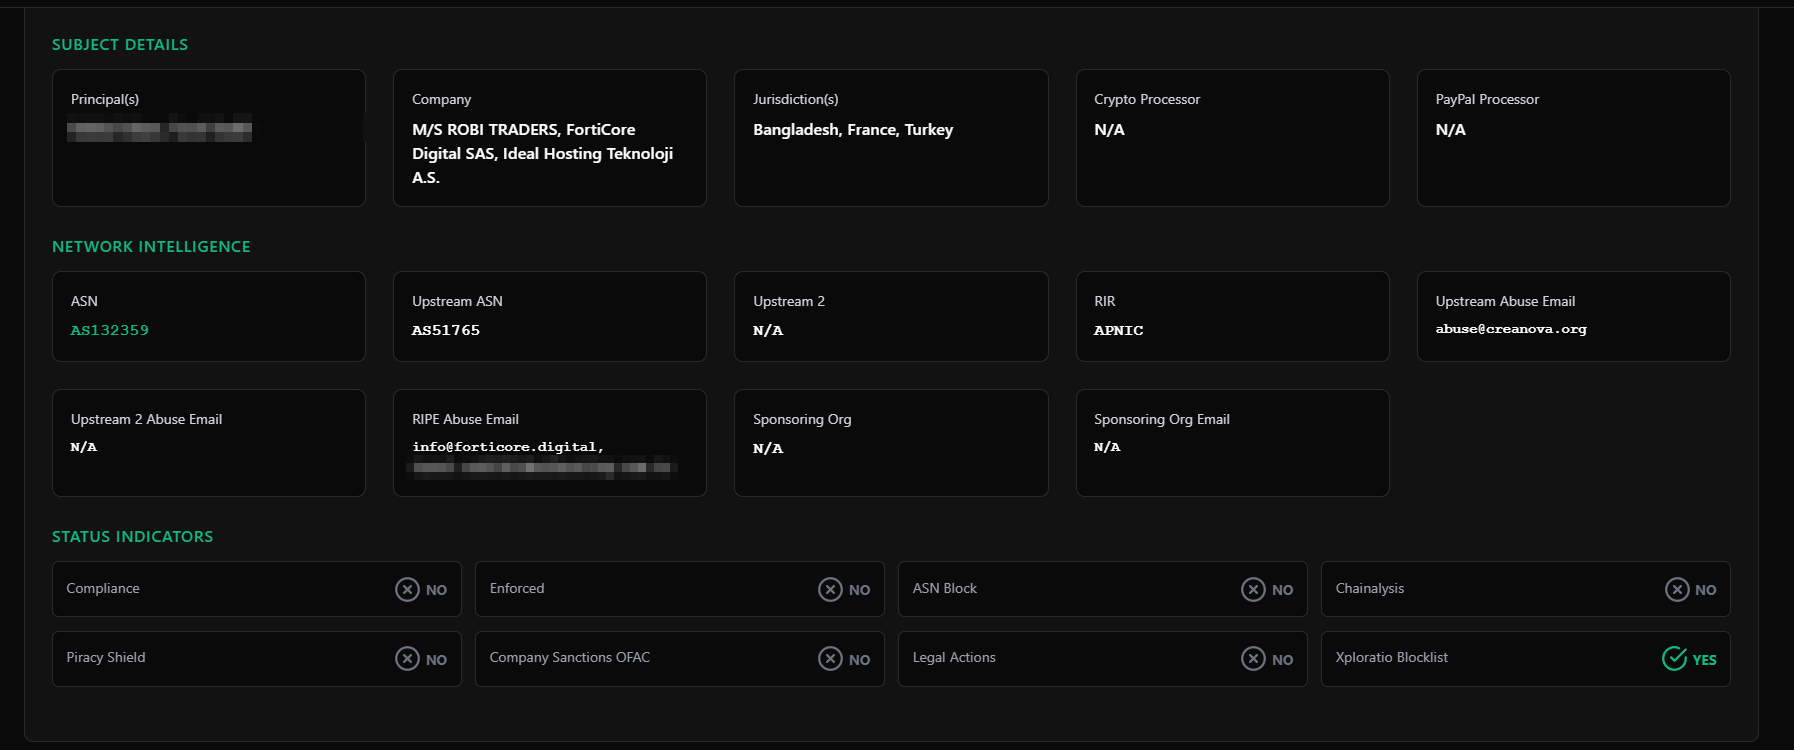
AS132359 hosts a single IPv4 prefix, 46.29.26.0/24, assigned to the Turkish company Ideal Hosting Teknoloji A.Ş.
All 320 records for this prefix, which were identified by Xploratio during this investigation, were tracerouted to Helsinki, Finland via ipinfo.io.
These 320 records (304 after removing 16 duplicated records) resolve to just 19 distinct IP addresses within the block, per the host-level analysis later in this section, with most addresses hosting many domains each.
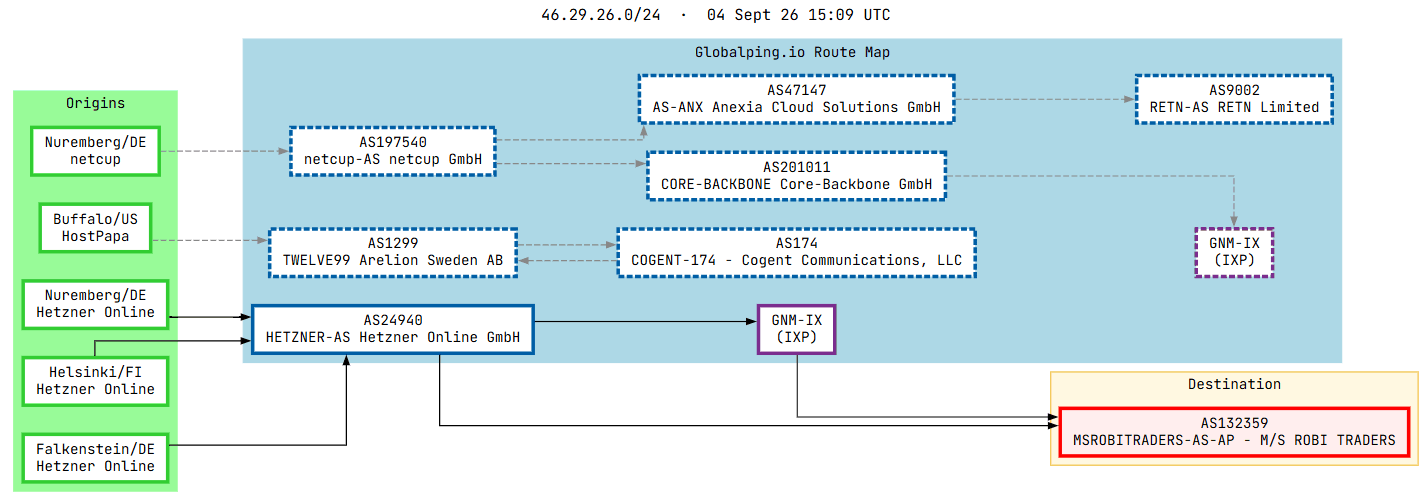
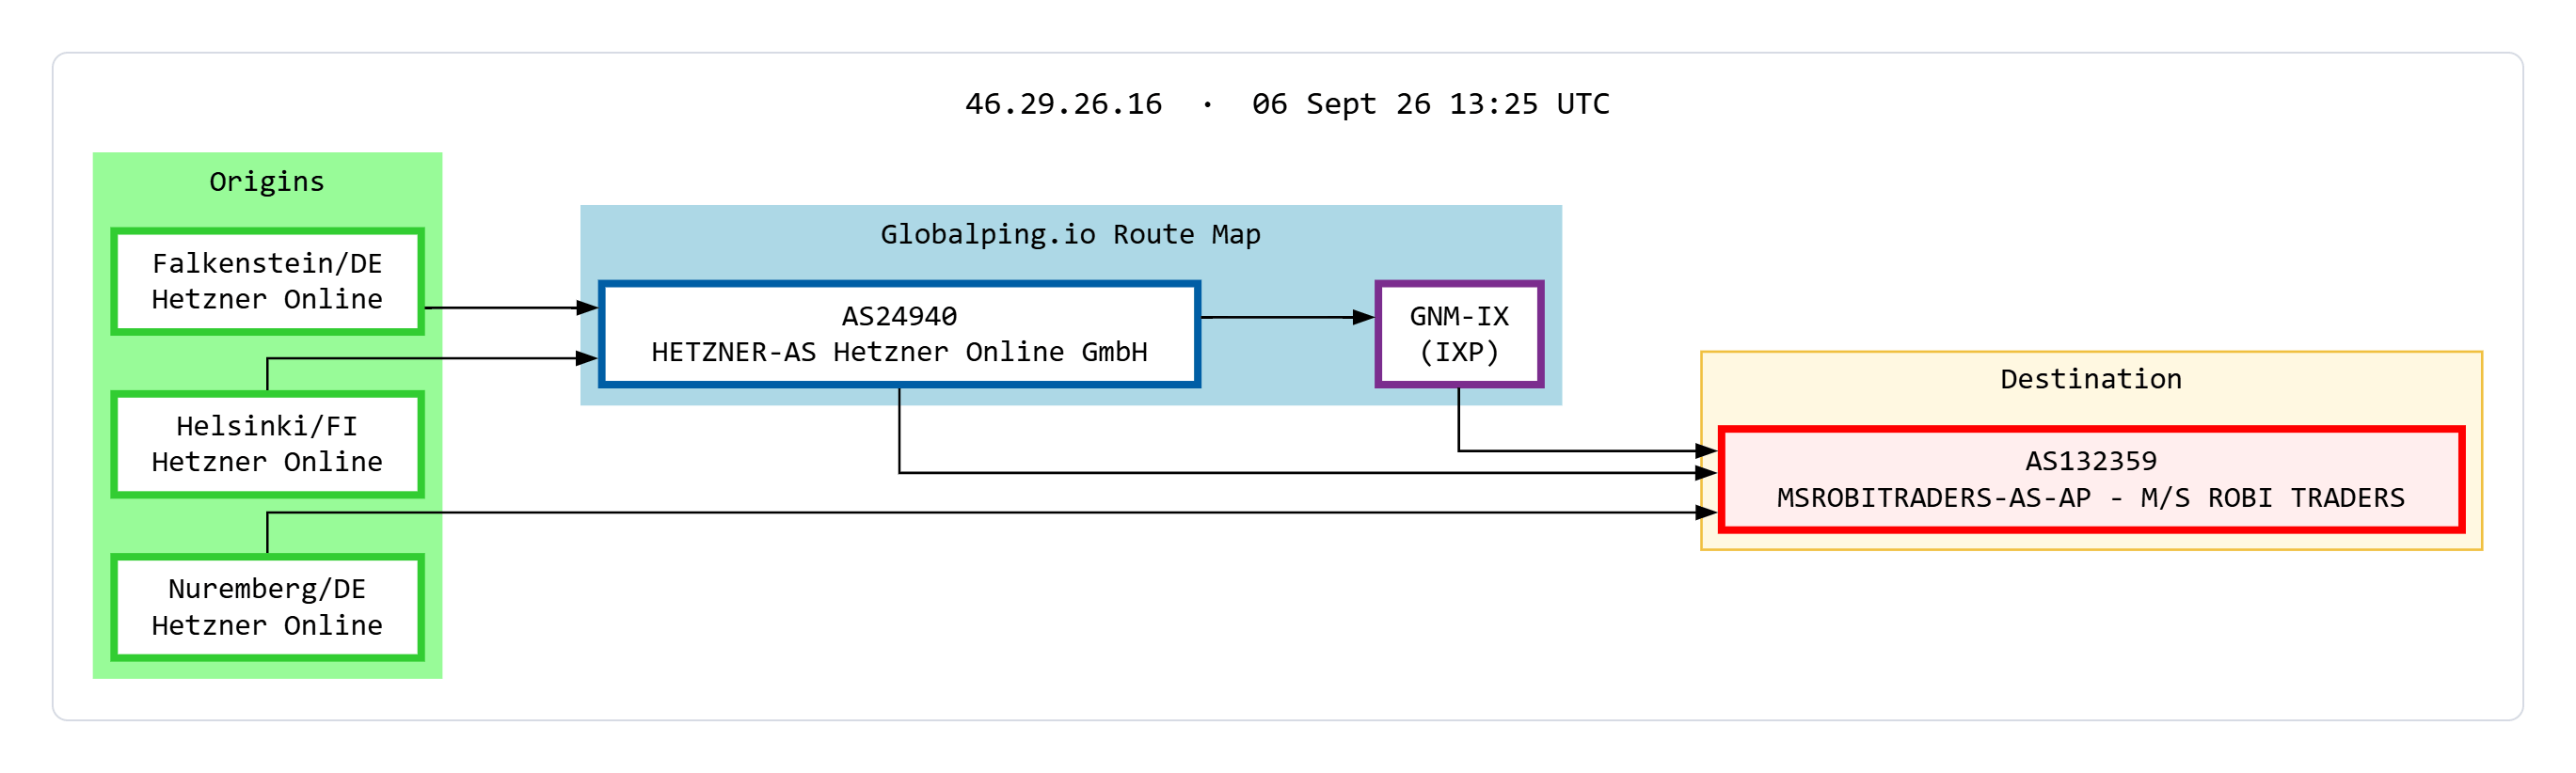
However, traceroute measurements for the 46.29.26.0/24 block show traffic transiting Hetzner Online GmbH, connected via the GNM-IX Internet Exchange Point.
As with AS201738 above, this reflects where Globalping’s probes for this trace happen to be hosted, not a registered peering relationship. AS132359’s own registered upstream is AS51765 (Oy Crea Nova Hosting Solution Ltd).
AS132359 — ASN Intelligence
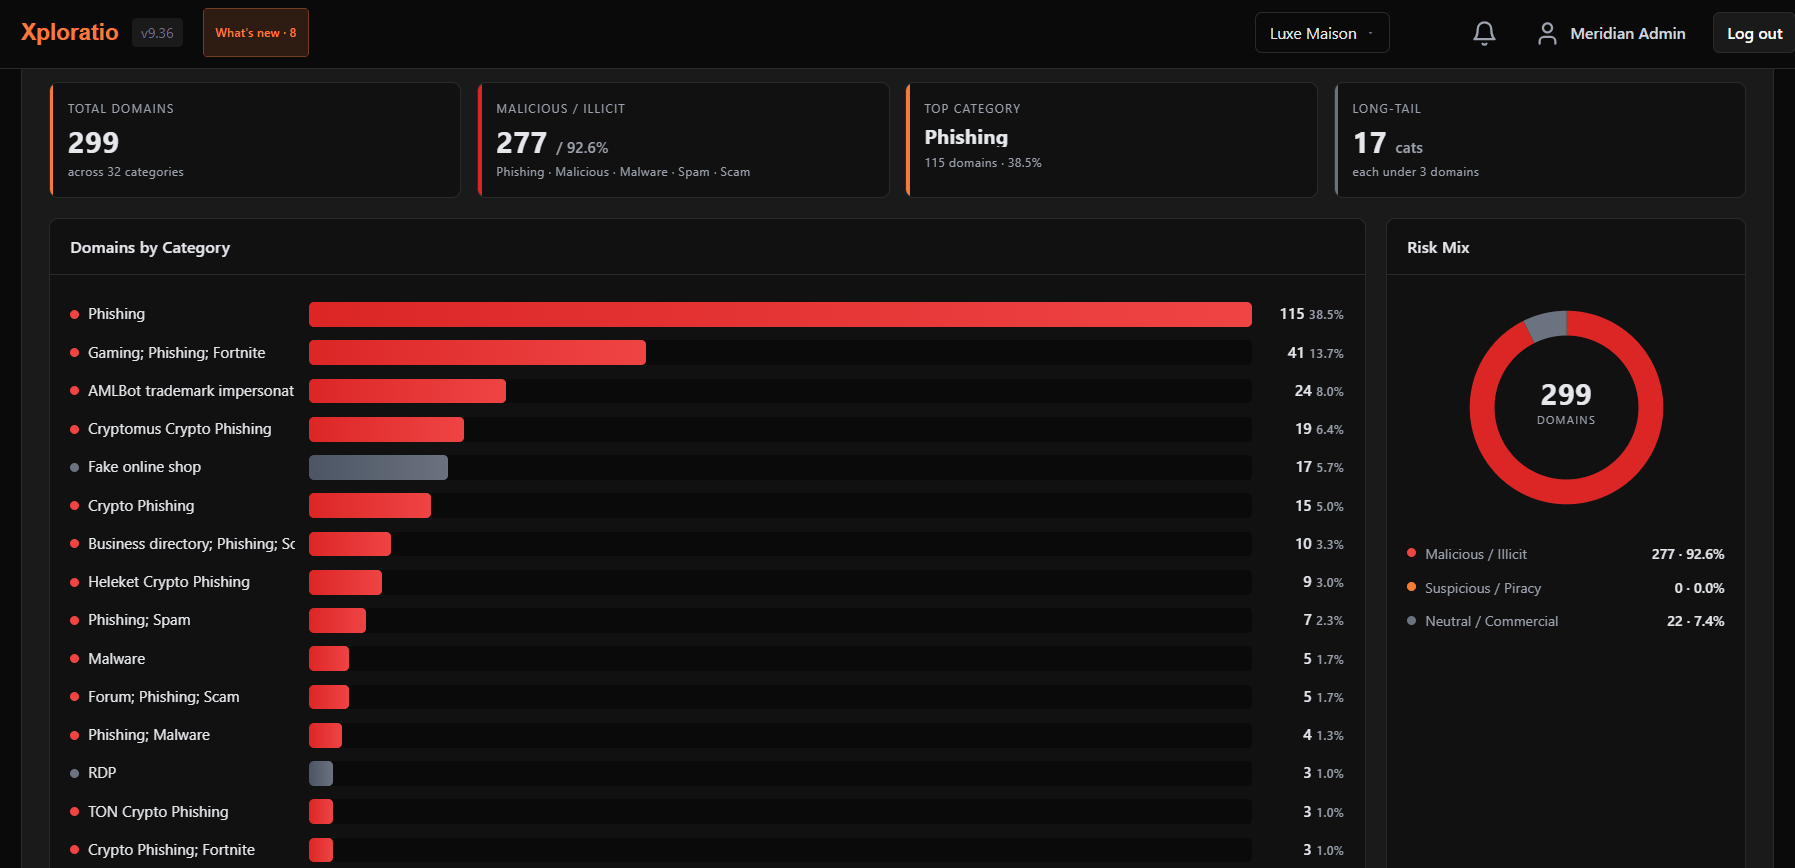
Xploratio’s ASN intelligence identified 299 domains hosted across AS132359, spanning 32 categories, of which 92.6% (277 domains) are malicious or illicit. The single largest category, generic Phishing, accounts for 38.5% of all hosted content (115 domains), spanning brand impersonation of Fortnite, Heleket, Cryptomus, AMLBot, Bybit, and Epic Games.
Figure 24 summarises the top 15 categories via the Xploratio platform; a thematic breakdown follows in Figure 25. The fuller export analysed for this article lists 304 unique records after removing 16 exact-duplicate export records, five more than this dashboard snapshot; every chart from this point on is drawn from that fuller record set.
The cause here is different from AS201738 above: of the 304 records, 4 are identified only by IP address rather than a domain name, and one domain, tractorforrum[.]com, recurs across two export results recorded with overlapping category tags. Counting unique domain names, as the dashboard does, therefore yields 299 domain names (300 domain-bearing rows minus that one repeat), matching the total shown.
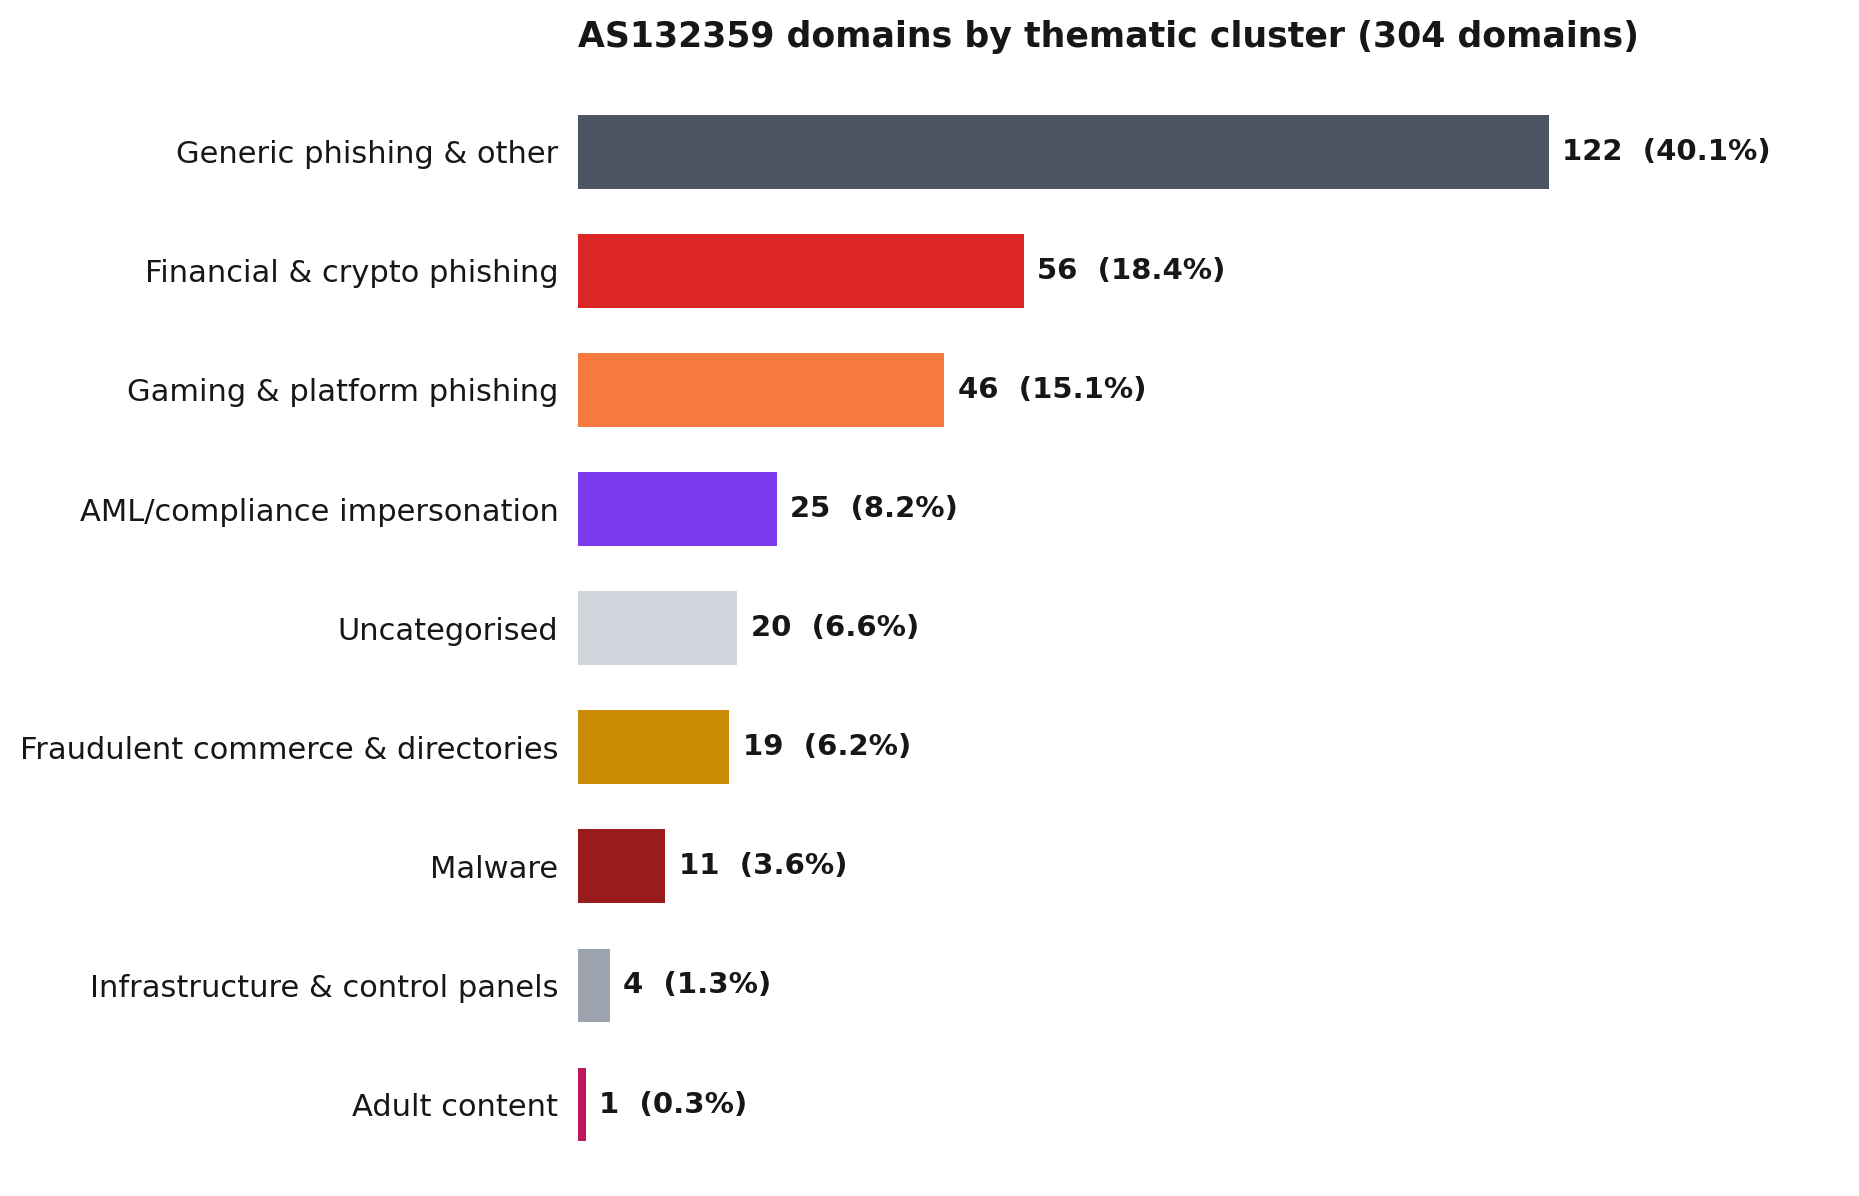
Unlike AS201738, where gaming phishing dominates, Figure 25 shows AS132359’s content is led by generic phishing (40.1%), with a substantial financial and crypto-phishing cluster (18.4%) spanning several exchange and payment-processor brands, and a further 15.1% of gaming-brand phishing concentrated on Fortnite.
Still Live: AS132359 Response Status
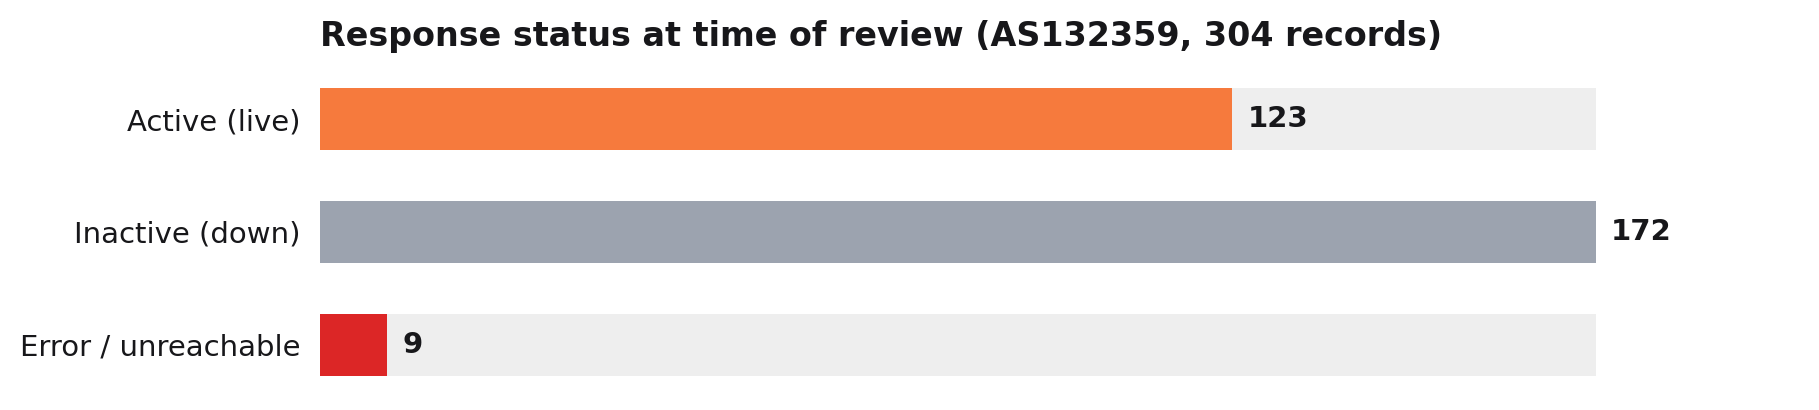
Response status at the time of review. Active is the actionable slice — everything else is already down or erroring.
Of AS132359’s 304 records, 123 (40.5%) currently respond as active, including twelve that redirect to a live third-party domain (fragment.com, cryptomus.com, or heleket.com) rather than serving content directly; 172 (56.6%) are inactive and nine (3.0%) return an HTTP error.
Named Networks or Campaigns Hosted on AS132359
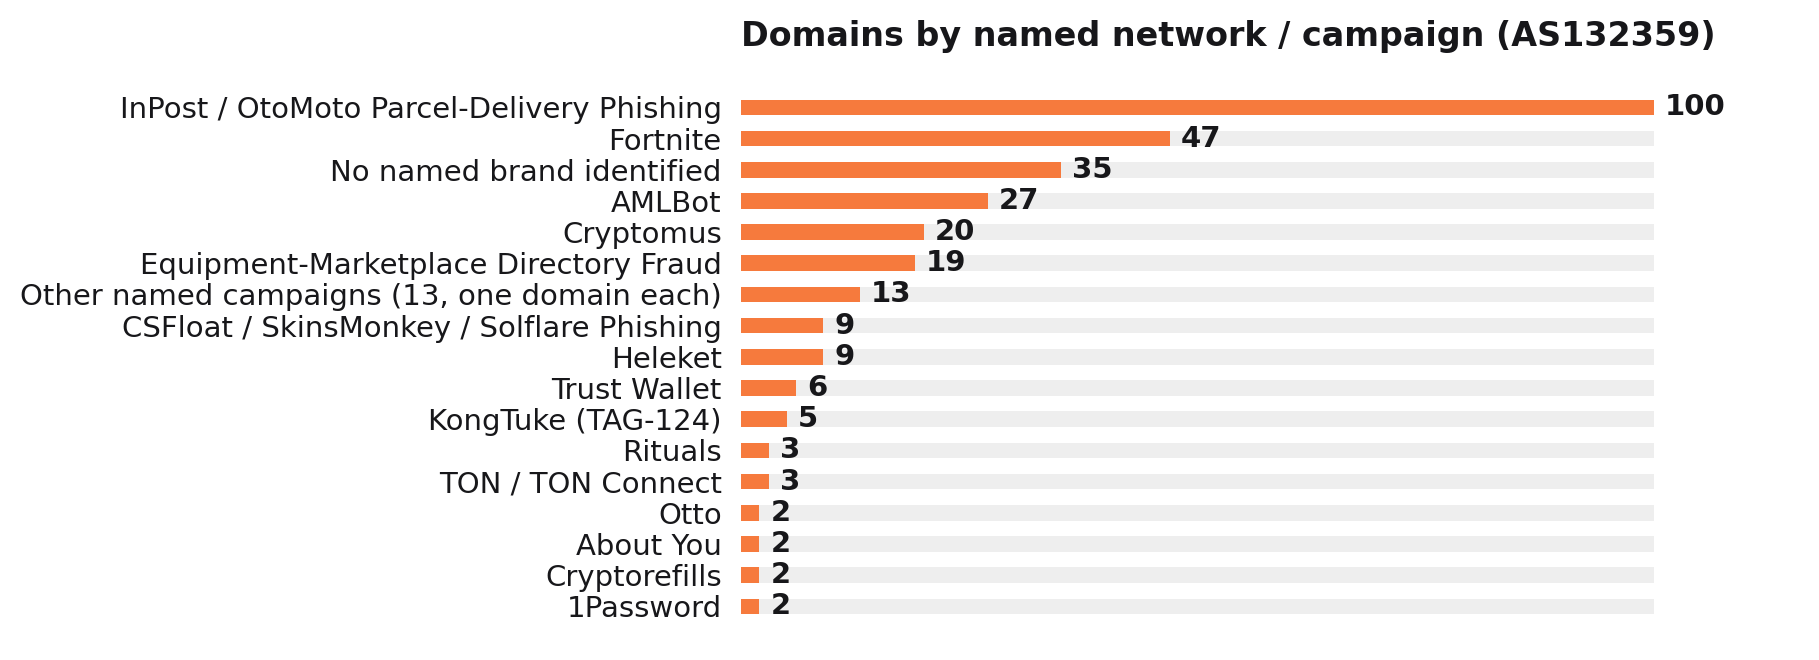
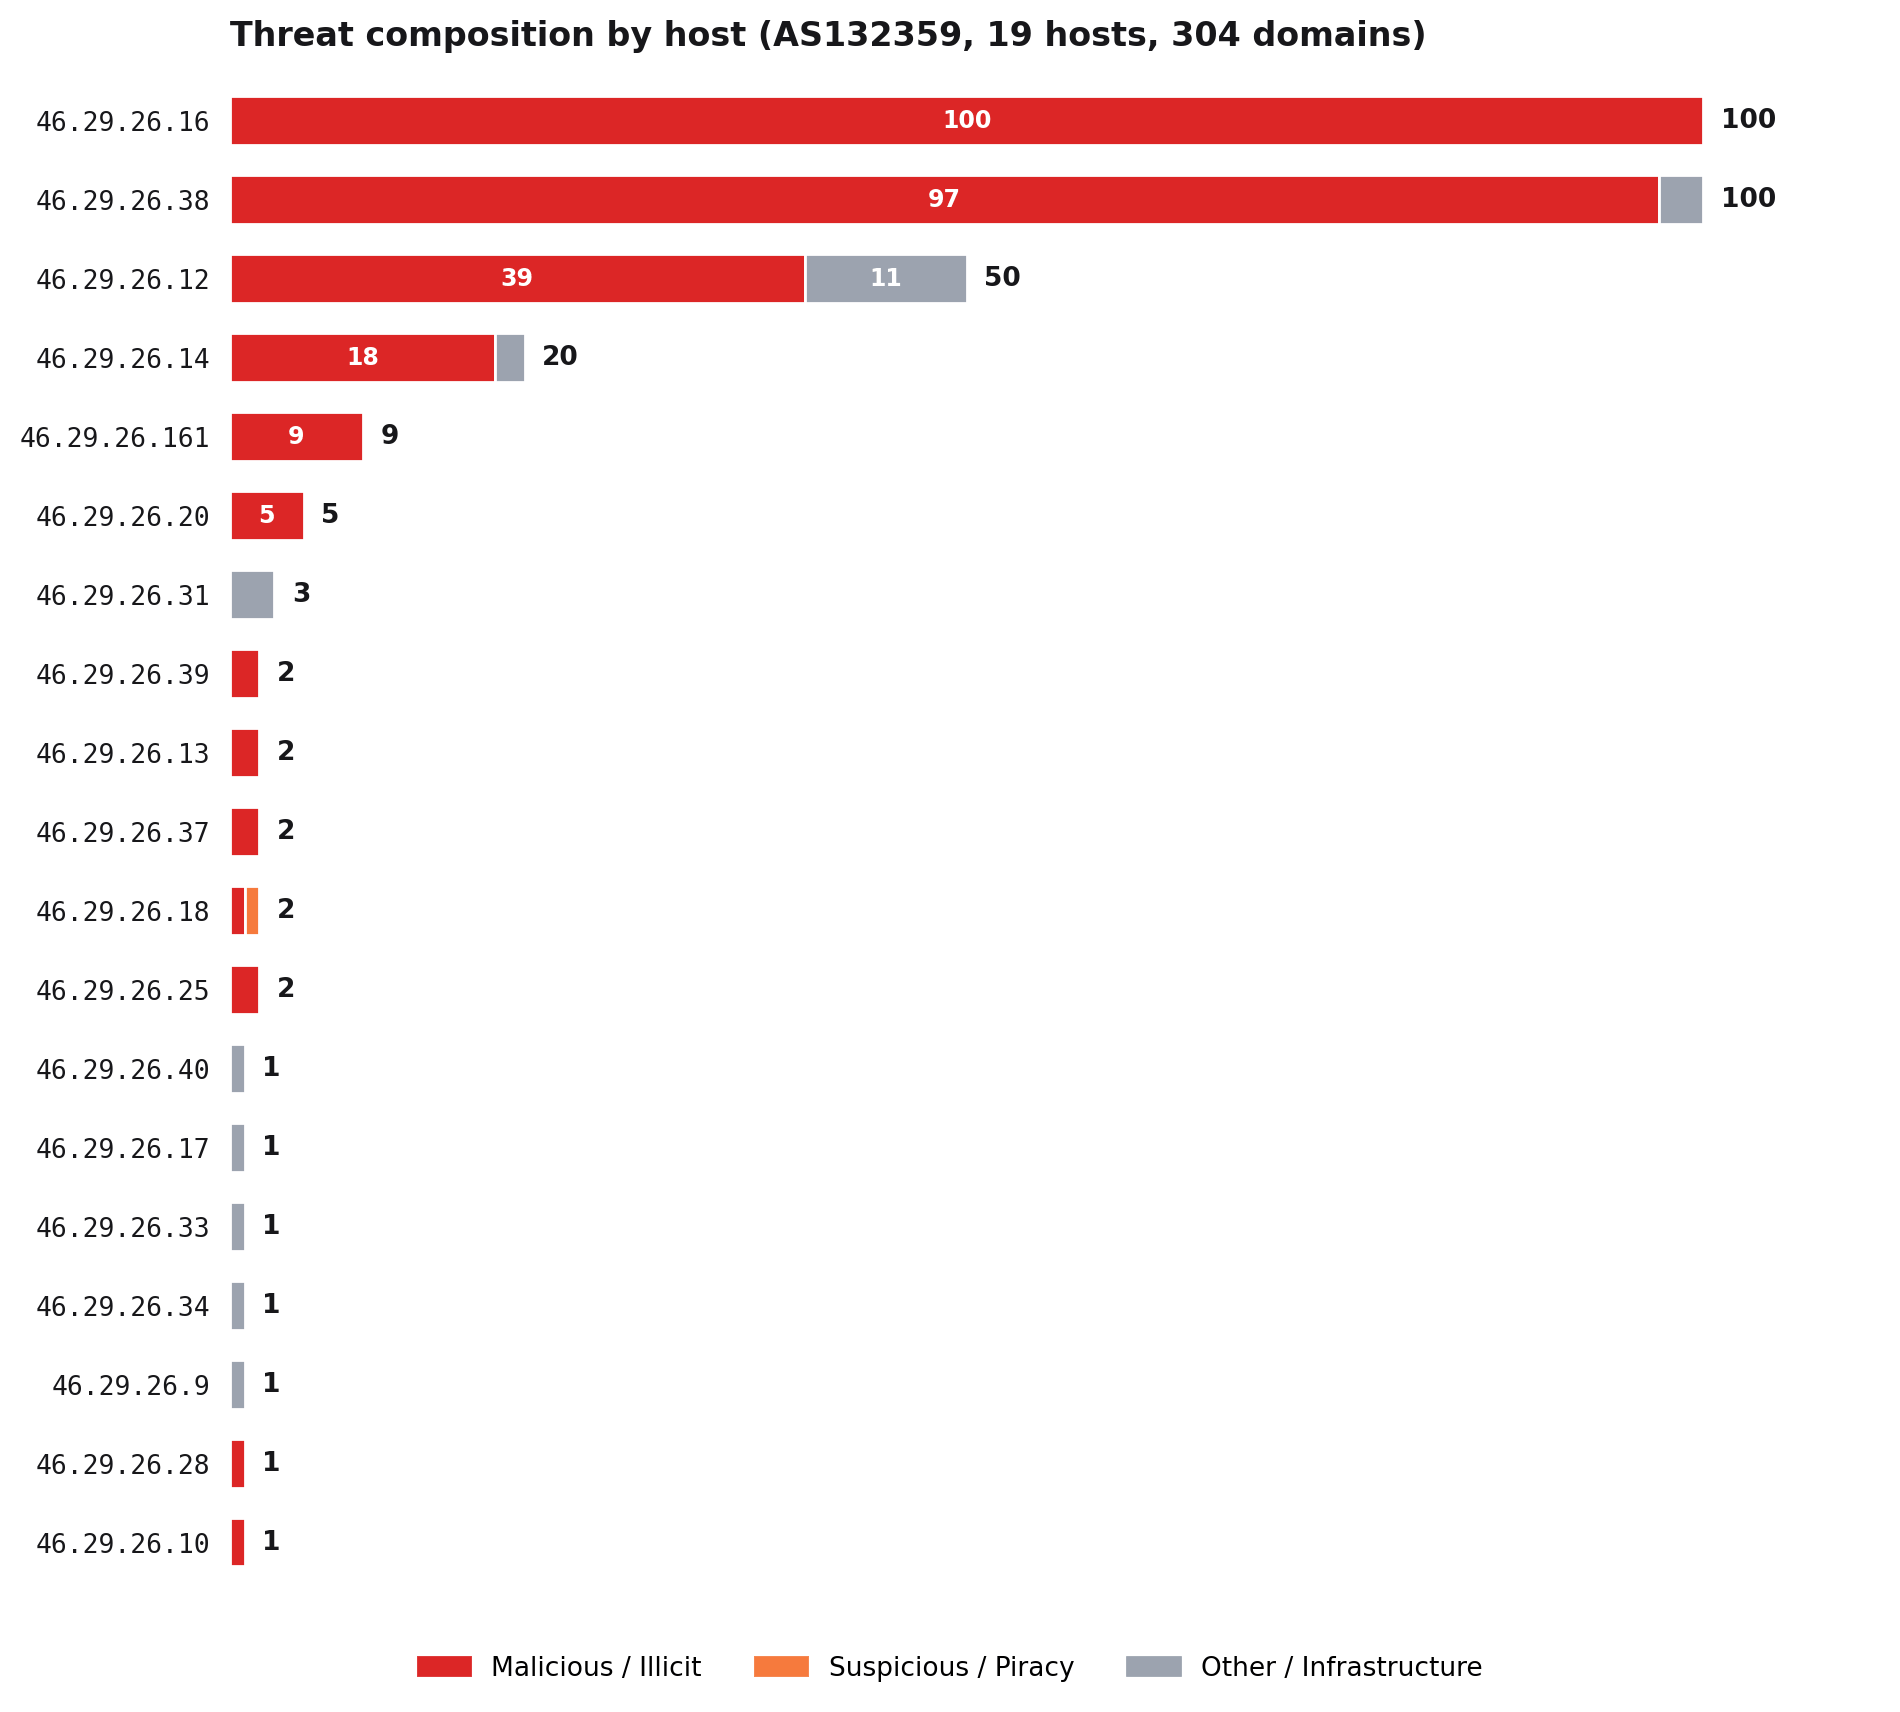
The same method used for AS201738 is applied here. Two hosts account for the largest discoveries: 46.29.26[.]16 serves 100 domains as a single Polish parcel-delivery and OtoMoto smishing operation (InPost / OtoMoto Parcel-Delivery Phishing) — 14 with an explicit InPost/Poczta/OtoMoto string in the domain, the other 86 randomised strings on the identical single-purpose host with no other brand identity — while 46.29.26[.]161 hosts nine domains dedicated to gaming-skin-trading and crypto wallet phishing (CSFloat / SkinsMonkey / Solflare Phishing).
A further 19 domains, all in the fraudulent commerce and directories cluster, typosquat a coherent set of heavy-equipment and business directory brands (MachineryTrader, EquipmentTrader, TractorHouse, Ritchie Bros/RitchieList, My Little Salesman, Yellow Pages, Trustpilot, Manta, and Angi) and are grouped as Equipment-Marketplace Directory Fraud.
Thirteen further named campaigns — Crossover, golove, Coinbase, Bybit, Fort Token, Gram Unlocker, 5boost, Tron, Codashop, TRXSwap, Rifted, Epic Games, and SilkGuard — each account for a single domain and are grouped as “Other named campaigns” in the chart below for legibility.
Figure 25 and Figure 27 group these domains on different bases and are not directly comparable. Figure 25 groups by Category, the content type Xploratio assigns to each domain; Figure 27 groups by the Network field, a separate campaign attribution Xploratio adds when domains share infrastructure with an identified brand, even where the domain string itself carries no brand name. This is why, for example, the 100 InPost/OtoMoto Parcel-Delivery Phishing domains above are categorised simply as Phishing, Phishing; Spam, or Phishing; Malware, so most fall under Figure 25’s Generic phishing & other cluster, while Figure 27 attributes all 100 of them to that named campaign based on the shared host and the 14 domains with an explicit brand string in the domain name.
Threat Composition by Host on AS132359
Two hosts, 46.29.26[.]16 and 46.29.26[.]38, together account for 200 of the 304 records and are almost entirely malicious or illicit; a further two hosts (46.29.26[.]12 and 46.29.26[.]14) carry a mix of malicious and other/infrastructure records, and the remaining fifteen hosts each serve five or fewer records.
Hosted Content on AS132359 — Examples
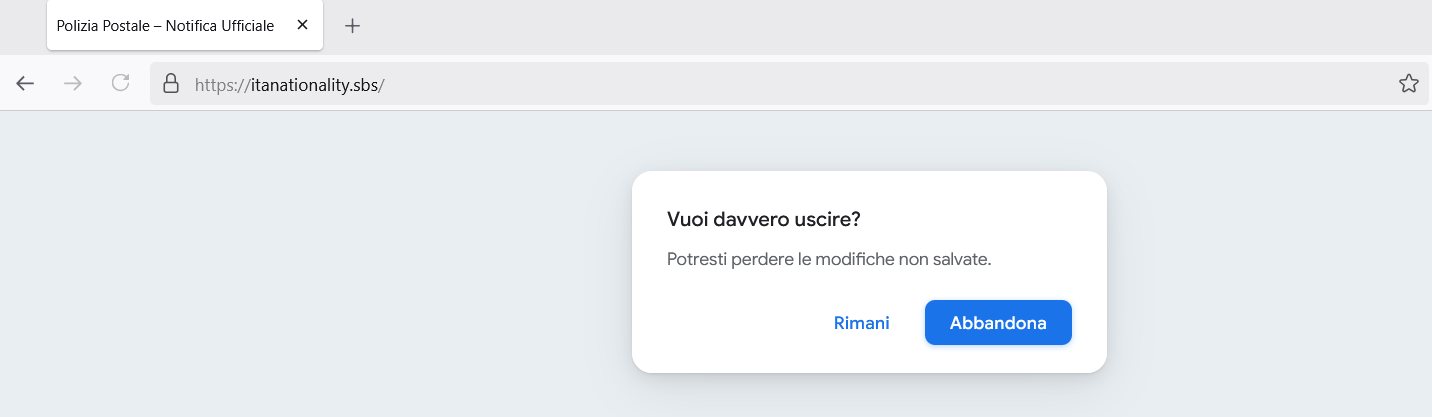
1. Malware Impersonating Polizia Postale
This example impersonates the Italian postal police (Polizia Postale), presenting a fabricated official notice to pressure the victim into surrendering personal or payment details under threat of legal action — a well-established social engineering pattern in which a trusted law enforcement brand is used to override the victim’s usual scepticism.
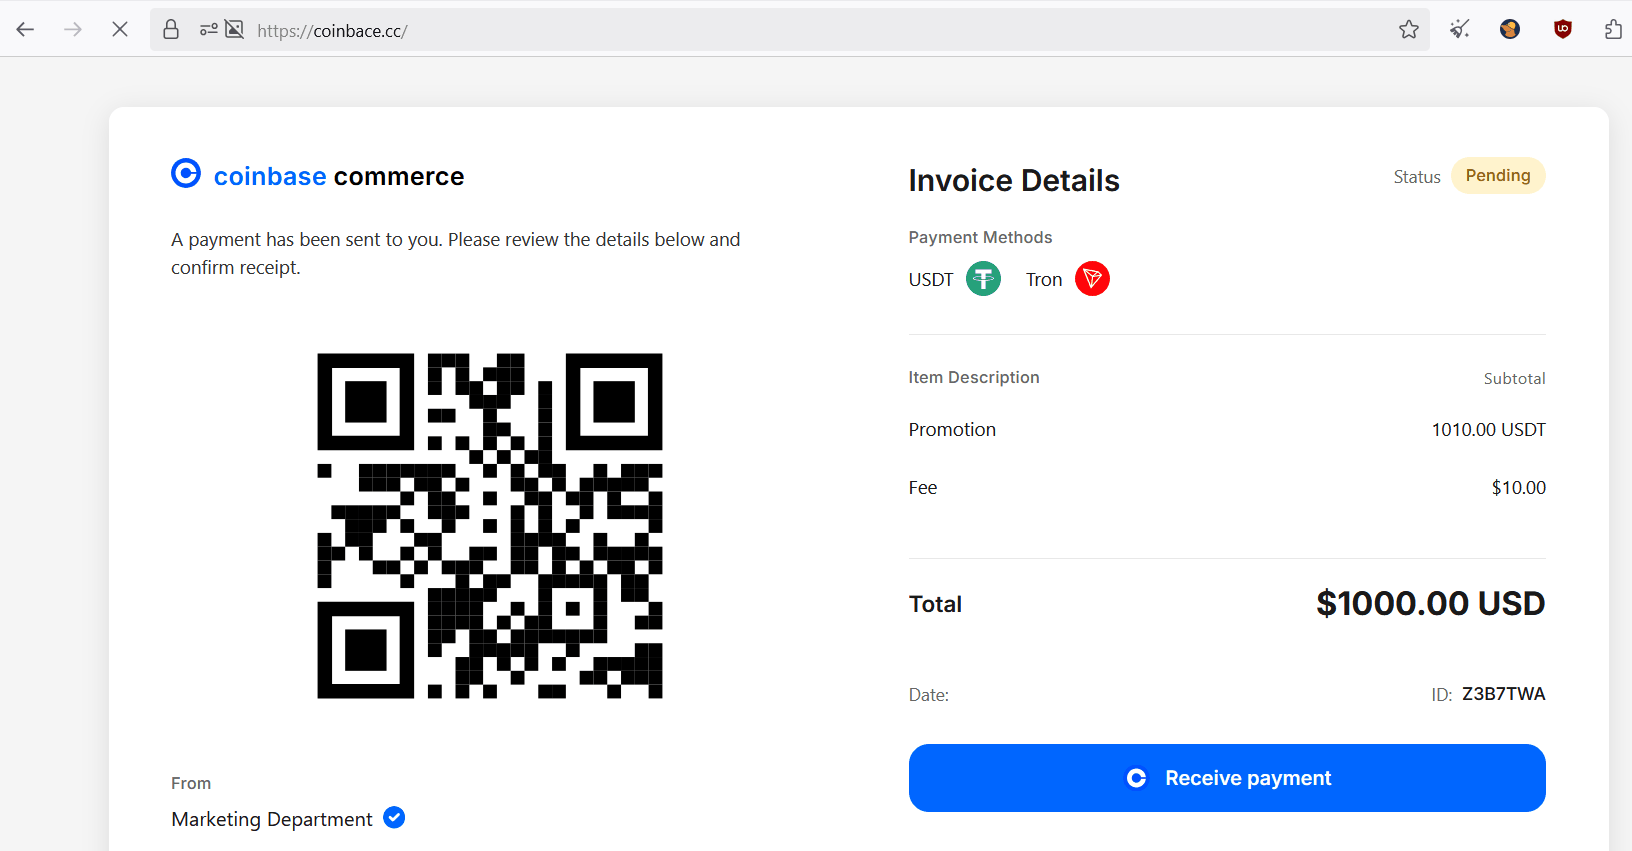
2. Coinbase-Related Phishing
This page mimics a Coinbase Commerce payment notification, directing the victim to scan a QR code or follow a wallet link to “receive” a payment. In practice, interacting with the page authorises an outbound cryptocurrency transfer from the victim’s own wallet — a template consistent with the financial and crypto-phishing cluster identified on this network (Figure 25).
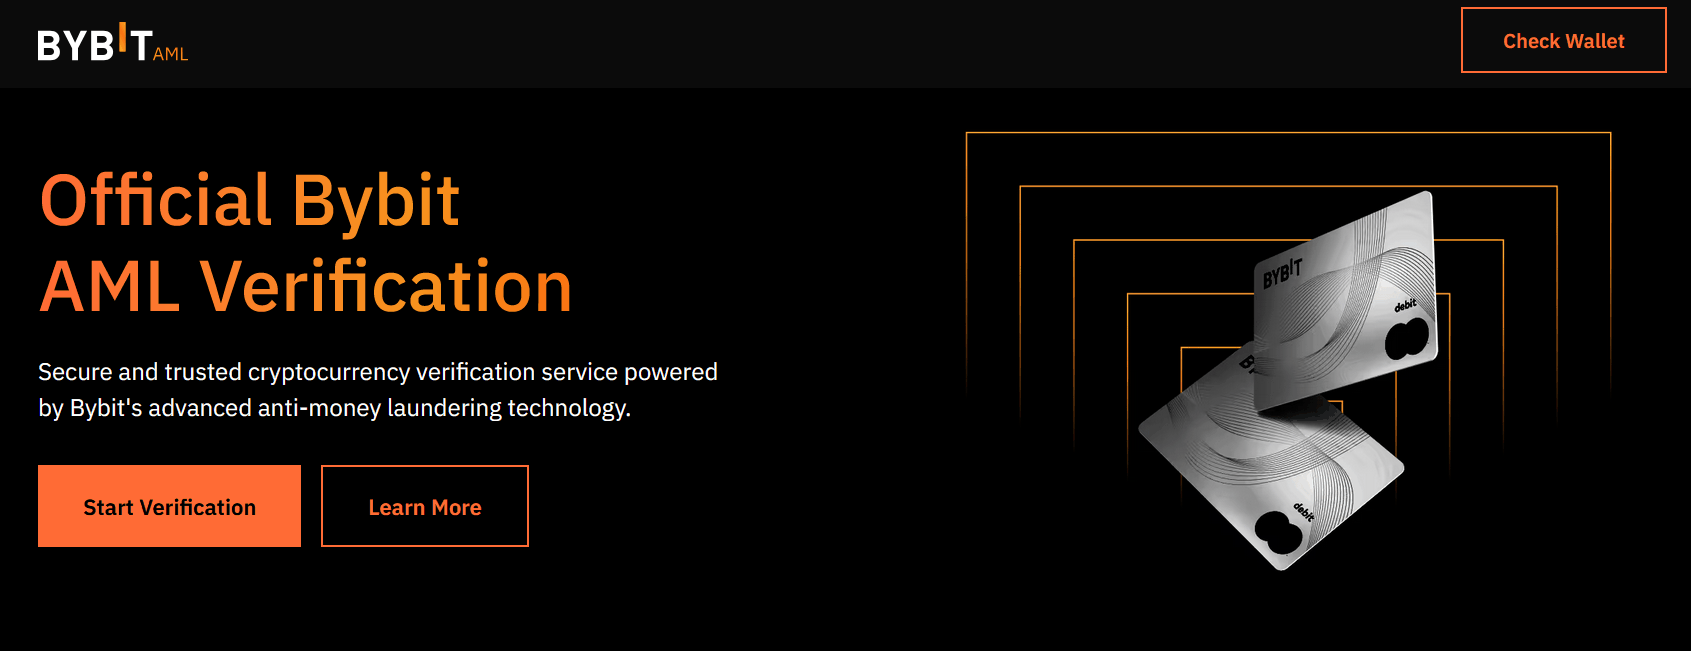
3. Bybit-Related Phishing
This page impersonates Bybit’s anti-money-laundering (“AML”) wallet-verification process, prompting victims to “verify” their wallet to avoid a supposed compliance restriction. Fraudulent AML-verification flows of this kind are typically used to harvest wallet seed phrases or private keys under the guise of a routine compliance check.
Xploratio Disruption Intelligence Services
Bulletproof hosting providers exist specifically to shield high-volume phishing, piracy, fraud, and other malicious infrastructure from takedown — which is precisely why attribution and disruption require more than a single point-in-time observation.
Xploratio’s Disruption Intelligence combines continuous ASN- and IP-level investigation, cross-referenced against threat intelligence feeds and investigators’ verification and validation processes, to build durable attribution chains from a hosting advertisement through to a named operator, and to track how threat actors migrate between bulletproof providers over time.
For organisations defending a brand, platform, or user base against phishing, fraud and piracy at scale, this translates into earlier detection, stronger evidentiary attribution for takedown and legal action, and visibility into infrastructure reused across campaigns — insight a single domain-level takedown cannot provide. To learn how Xploratio’s Disruption Intelligence Services can support your brand protection or anti-fraud programme, contact us.